

Směrovač Huawei E5785-320a (bílý) Síťové standardy: IEEE 802.11aIEEE 802.11acIEEE 802.11gIEEE 802.11bIEEE 802.11n Kapacita baterie: 1500 mAh Typ zdroje: Baterie Vestavěný displej: Ano Typ produktu: Př
Dodání 3 dny
Připojení 5G NR: Podporuje 5G NR s rychlostí stahování až 7,01 Gb/s a odesílání 2,5 Gb/s pro ultrarychlý internet. Silné pokrytí Wi-Fi 7: Nabízí rychlost Wi-Fi až 7,2 Gb/s pro plynulý a nerušený online zážitek. Bez optických vláken: Jednoduše vložte SIM kartu pro okamžitý vysokorychlostní internet
Dodání 3-5 dní

Cisco Catalyst switch C1200-48P-4G - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Řada Cisco Catalyst 1200 je další generací cenově dostupných chytrých přepínačů, které kombinují vysoký výkon a spolehlivost s kompletní sadou funkcí, které potřebujete pro malé a středně velké podnikové sítě. Přepínače fungují na přizpůsobeném softwaru operačního systému Linux a poskytují flexibilní možnosti správy, komplexní možnosti zabezpečení a funkce statického směrování na 3. vrstvě, které daleko přesahují možnosti neřízeného nebo levného přepínače a to za nižší cenu než u plně spravovaných přepínačů. Když potřebujete spolehlivé řešení pro sdílení online zdrojů a připojení počítačů, telefonů a bezdrátových přístupových bodů, chytré přepínače Catalyst řady 1200 poskytují ideální řešení za dostupnou cenu. Stránky produktu: C1200-48P-4G Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 77,38 Switching capacity in gigabits per second (Gbps) 104 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 4 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG) VLAN Support for up to 255 active VLANs simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Auto Surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Enable automatically propagation and configuration of VLANs in a bridged domain Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping Limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported) IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 routing IPv4 routing Wire-speed routing of IPv4 packets Up to 32 static routes and up to 16 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets Security Secure Sockets Layer (SSL) Encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch SSH Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported. IEEE 802.1X (authenticator role) RADIUS authentication, guest VLAN, single/multiple host mode, and single/multiple sessions STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices and a secure auto-configuration. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC]) Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses RADIUS Supports RADIUS authentication for management access. Switch functions as a client Storm control Broadcast, multicast, and unknown unicast DoS prevention DoS attack prevention Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels ACLs Support for up to 512 rules Drop or rate limit based on source and destination MAC, VLAN ID, IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides Time-based ACLs supported Quality of service Priority levels 8 hardware queues Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and Class of Service (802.1p/CoS) Class of service Port based, 802.1p VLAN priority based, IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based, Differentiated Services (DiffServ), classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer, egress shaping and rate control per VLAN, per port, and flow based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.3 ad LACP, IEEE 802.1D (STP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, RFC 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 920, RFC 922, RFC 950, RFC 951, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1213, RFC 1215, RFC 1286, RFC 1350, RFC 1442, RFC 1451, RFC 1493, RFC 1533, RFC 1541, RFC 1542, RFC 1573, RFC 1624, RFC 1643, RFC 1700, RFC 1757, RFC 1867, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2030, RFC 2131, RFC 2132, RFC 2233, RFC 2576, RFC 2616, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 3416, RFC 4330 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet Dual IPv6/IPv4 stack IPv6 Neighbor Discovery (ND) IPv6 stateless address auto-configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) ICMP version 6 IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) support IPv6 QoS Prioritizes IPv6 packets in hardware IPv6 ACL Drop or rate-limit IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) snooping Delivers IPv6 multicast p
Ano, centrál. sklad

Ubiquiti Router EdgeRouter ER-4 Výrobce: Ubiquiti Kategorie: Routery
Skladem, dodání 2-4 dní
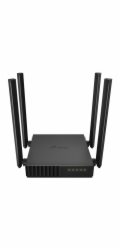
TP-Link Archer C54 bezdrátový router Fast Ethernet Dvoupásmový (2,4 GHz / 5 GHz) Černá Přenosová rychlost sítě Ethernet: 10100 Připojení na síť Ethernet: Ano Síťové standardy: IEEE 802.11acIEEE 802.11
3-5 dní dostupno

NoName POE PŘEPÍNAČ / ROZŠÍŘOVAČ SPT-POE/4G-POE-DIN-E 5PORTOVÝ DELTA NETWORK Výrobce: NoName
Dodání 3-5 dní

SÍŤOVÝ PŘEPÍNAČ 5PORTOVÝ 10/100M/1G/SG1005L-EUR DAHUA – Efektivní síť pro vaši kancelář Dahua DH-SG1005L je vynikajícím řešením pro moderní kanceláře, které potřebují spolehlivou a rychlou síť. Tento 5portový gigabitový switch s podporou rychlostí 10/100/1000 Mbps zajišťuje stabilní připojení, kter
Dodání 3-5 dní
Popis produktu Ubiquiti U7 Pro XGS je nový WiFi 7 UniFi AP. Jedná se o tri-band access point s rychlostí přenosu 5,8Gbps v pásmu 6GHz, až 8,6Gbps v 5GHz pásmu a až 688 Mbps v pásmu 2,4GHz a pokročilým šifrováním WPA3. U7-Pro-XGS je určeno k WiFi pokrytí
Ano, centrál. sklad
TP-Link Archer NX500 - Výkonný 5G router s technológiou Wi-Fi 6 poskytujúci duálne pásmo s rýchlosťami až 3000 Mbps (2402 Mbps na 5 GHz + 574 Mbps na 2,4 GHz). Podporuje 5G sieť s rýchlosťou sťahovania až 4,67 Gbps. Funguje na princípe Plug & Play - stačí vložiť SIM kartu. Vybavený gigabitovými LAN/WAN portmi pre káblové pripojenie. Kompatibilný s EasyMesh pre rozšírenie pokrytia. Ideálny pre domácnosti s potrebou stabilného a rýchleho pripojenia cez 5G sieť, vhodný pre streamovanie, hranie online hier a pripojenie viacerých zariadení súčasne.
Dodání 3 dny
Cisco Catalyst switch C1200-8T-D Řada Cisco Catalyst 1200 je další generací cenově dostupných chytrých přepínačů, které kombinují vysoký výkon a spolehlivost s kompletní sadou funkcí, které potřebujete pro malé a středně velké podnikové sítě. Přepínače fungují na přizpůsobeném softwaru operačního systému Linux a poskytují flexibilní možnosti správy, komplexní možnosti zabezpečení a funkce statického směrování na 3. vrstvě, které daleko přesahují možnosti neřízeného nebo levného přepínače a to za nižší cenu než u plně spravovaných přepínačů. Když potřebujete spolehlivé řešení pro sdílení online zdrojů a připojení počítačů, telefonů a bezdrátových přístupových bodů, chytré přepínače Catalyst řady 1200 poskytují ideální řešení za dostupnou cenu. Stránky produktu: C1200-8T-D Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 11,9 Switching capacity in gigabits per second (Gbps) 16 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 4 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG) VLAN Support for up to 255 active VLANs simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Auto Surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Enable automatically propagation and configuration of VLANs in a bridged domain Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping Limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported) IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 routing IPv4 routing Wire-speed routing of IPv4 packets Up to 32 static routes and up to 16 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets Security Secure Sockets Layer (SSL) Encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch SSH Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported. IEEE 802.1X (authenticator role) RADIUS authentication, guest VLAN, single/multiple host mode, and single/multiple sessions STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices and a secure auto-configuration. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC]) Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses RADIUS Supports RADIUS authentication for management access. Switch functions as a client Storm control Broadcast, multicast, and unknown unicast DoS prevention DoS attack prevention Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels ACLs Support for up to 512 rules Drop or rate limit based on source and destination MAC, VLAN ID, IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides Time-based ACLs supported Quality of service Priority levels 8 hardware queues Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and Class of Service (802.1p/CoS) Class of service Port based, 802.1p VLAN priority based, IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based, Differentiated Services (DiffServ), classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer, egress shaping and rate control per VLAN, per port, and flow based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.3 ad LACP, IEEE 802.1D (STP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, RFC 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 920, RFC 922, RFC 950, RFC 951, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1213, RFC 1215, RFC 1286, RFC 1350, RFC 1442, RFC 1451, RFC 1493, RFC 1533, RFC 1541, RFC 1542, RFC 1573, RFC 1624, RFC 1643, RFC 1700, RFC 1757, RFC 1867, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2030, RFC 2131, RFC 2132, RFC 2233, RFC 2576, RFC 2616, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 3416, RFC 4330 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet Dual IPv6/IPv4 stack IPv6 Neighbor Discovery (ND) IPv6 stateless address auto-configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) ICMP version 6 IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) support IPv6 QoS Prioritizes IPv6 packets in hardware IPv6 ACL Drop or rate-limit IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) snooping Delivers IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, Ping, Traceroute, Simple Network Time Protocol (SNTP), Trivial File Transfer Protocol (TFTP),
Ano, centrál. sklad
ZyXEL USG FLEX 50H + Gold Security Pack; Bezpečnostní brána poskytující rychlou a vysoce účinnou ochranu, špičkový výkon pro virtuální privátní sítě (VPN) a sjednocené řízení ochrany proti hrozbám (UTM). Zajišťuje komplexní ochranu síťové infrastruktu...
Ano, centrál. sklad

PLANET SGS-6310-24P4X; Stohovatelný řízený L3 PoE switch, 24x RJ-45 10/100/1000 Base-T, 4x 10G SFP+ Base-SR/LR , 1x RJ-45 (RS-232) konzolový port, PoE+ injektory 802.3af/at s celkovým napájením...
Ano, centrál. sklad

PLANET GSD-1002M; Administrovatelný přepínač s gigabitovými porty a duálním napájením. 8x portů 1000Base-T, 2x porty 100/1000Base-X SFP(DDM). Port shaper, VLAN 802.1Q, agregace propojení LACP, podpora QoS, STP/RS...
Ano, centrál. sklad

Popis produktu UXG-Fiber je kompaktní 10 gigabitový router, který disponuje (1) WAN 10Gbps portem, (2) 10Gbps SFP+ porty (1x WAN, 1x LAN) a (4) LAN 1/2.5Gbps porty s jedním PoE-OUT portem s podporou PoE+ 802.3af/at. Kompaktní, ale výkonné provedení tak podporuje funkci multi-WAN včetně možnosti load balancing, nechybí podpora IDS/IPS. Router má implementovanou podporu různých typů VPN, včetně site-to-site VPN. Napájení je řešeno prostřednictvím napájecího adaptéru 54V/1,1A, napájecí adaptér je součástí balení. Klíčové vlastnosti • 5Gbps routing s podporou IDS/IPS • (1) WAN 10Gbps + (1) 10Gbps SFP+ WAN • (4) 2.5Gbps LAN + (1) 10Gbps SFP+ • Multi-WAN + load balancing • Podpora VPN, včetně site-to-site VPN Obsah balení • Zařízení • Patch kabel • Napájecí adaptér 54V/1,1A Technické parametry Konektory a rozhraní Rychlosti WAN:(1) 1/2.5/10Gbps + (1) 10Gbps SFP+ Možnost více WAN:Ano Rychlost LAN:(4) 10/100/1000/2500Mbps Gigabit LAN:Ano Optické rozhraní:(2) 10Gbps Napájení Typ napájení:DC konektor Typy PoE:PoE-Out (pouze) Podporované PoE-Out standardy:802.3af, 802.3at Počet PoE Out portů:1 Max. spotřeba energie [W]:25 Napájení přes konektor/svorkovnici:54V / 1,1A Fyzické charakteristiky Provedení:Desktop Šasi:Plastové Tlačítka:Reset Provozní teplota [°C]:0 až 40 Hmotnost [g]:605 Šířka [mm]:213 Výška [mm]:30 Hloubka [mm]:128 Hardware CPU:ARM Cortex-A73 Frekvence CPU [MHz]:2200 Počet CPU jader:4 RAM [MB]:2048 Software Podporované VPN:L2TP, IPSec, OpenVPN, WireGuard Management:UniFi Network Podpora IPv6:Ano
Ano, centrál. sklad

Draytek Vigor 2927lac router
Dodání 3-5 dní
Cisco switch CBS220-8P-E-2G Řada Cisco Business 220 jsou jednoduché a cenově dostupné chytré switche pro sítě podnikové třídy. Díky podpoře mobilních aplikací, nástroji Cisco Business Dashboard a několika možnostem PoE+ poskytuje CBS220 robustní síť v rámci omezeného rozpočtu. Stránky produktu: CBS220-8P-E-2G Quick start guide: Quick start guide Switching capacity Forwarding rate in millions of packets per second (mpps; 64-byte packets) 14,88 Switching capacity in Gigabits per second (Gbps) 20 Layer 2 switching MAC table Up to 8,192 Media Access Control (MAC) addresses Spanning Tree Protocol (STP) Standard 802.1d Spanning Tree support, enabled by default Fast convergence using 802.1w (Rapid Spanning Tree [RSTP]) Multiple Spanning Tree instances using 802.1s (MSTP) 16 instances are supported Port grouping Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation Load balance based on source and destination MAC address, or source and destination MAC/IP VLAN Support for up to 256 Virtual Local Area Networks (VLANs) simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Auto voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS QinQ VLAN VLANs transparently cross a service provider network while isolating traffic among customers Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Protocols for automatically propagating and configuring VLANs in a bridged domain Head-of-Line (HOL) blocking HOL blocking prevention Jumbo frame Frame sizes up to 9,216 supported Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP. Automatic Media-Dependent Interface Crossover (MDIX) Automatically adjusts transmit and receive pairs if an incorrect cable type (crossover or straight-through) is installed. Security ACLs Drop or rate limit based on source and destination MAC, VLAN ID or IP address, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, Transmission Control Protocol (TCP)/ User Datagram Protocol (UDP) source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, Internet Group Management Protocol (IGMP) packets, TCP flag Support up to 512 rules Port security Creates the ability to lock source MAC addresses to ports; limits the number of learned MAC addresses IEEE 802.1X (authenticator role) 802.1X: Remote Authentication Dial-in User Service (RADIUS) authentication; guest VLAN; Single-host, multiple-host, and multisession mode RADIUS, TACACS+ Supports RADIUS and Terminal Access Controller Access Control System (TACACS) authentication; switch functions as a client MAC address filtering Supported Storm control Broadcast, multicast, and unknown unicast DoS protection DOS attack prevention STP Bridge Protocol Data Unit (BPDU) Guard This security mechanism protects the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. Spanning Tree Loop Guard This feature provides additional protection against Layer 2 forwarding loops (STP loops). Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. SCP also uses SSH. SSH v1 and v2 are supported. Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch QoS Priority levels 8 hardware queues per port Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and class of service (802.1p/CoS) Class of service Port-based; 802.1p VLAN priority-based; IPv4/v6 IP precedence, Type of Service (ToS), and DSCP-based; Differentiated Services (DiffServ); classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer; egress shaping and rate control; per VLAN, per port, and flow-based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization. Multicast Internet Group Management Protocol (IGMP) Versions 1, 2, and 3 Snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; supports 256 multicast groups IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad LACP, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.1D (STP, GARP, and GVRP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, Request for Comments (RFC) 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 922, RFC 920, RFC 950, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1350, RFC 1533, RFC 1541, RFC 1624, RFC 1700, RFC 1867, RFC 2030, RFC 2616, RFC 2131, RFC 2132, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 2576, RFC 4330, RFC 1213, RFC 1215, RFC 1286, RFC 1442, RFC 1451, RFC 1493, RFC 1573, RFC 1643, RFC 1757, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2233, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 1157, RFC 1493, RFC 1215, RFC 3416 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet IPv6/IPv4 Dual Stack IPv6 neighbor and router discovery (ND) IPv6 stateless address auto-configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) ICMP version 6 IPv6 ACL Drop or rate limit IPv6 packets in hardware IPv6 QoS Prioritize IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) Snooping Deliver IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, DHCP Client, DHCP Autoconfig, Cisco Discovery Protocol (CDP), Link Layer Discovery Protocol (LLDP) IPv6 Requests for Comments (RFCs) supported RFC 4443 (which obsoletes RFC2463) - ICMP version 6 RFC 4291 (which obsoletes RFC 3513) - IPv6 address architecture RFC 4291 - IPv6 addressing architecture RFC 2460 - IPv6 specification RFC 4861 (which obsoletes RFC 2461) - Neighbor discovery for IPv6 RFC 4862 (which obsoletes RFC 2462) - IPv6 stateless address auto-configuration RFC 1981 - Path MTU discovery RFC 4007 - IPv6 scoped address architecture RFC 3484 - Default address selection mechanism Management Cisco Business Dashboard Support direct management with Cisco Business Dashboard and mobile app. Eliminates the need to set up a separate hardware or virtual machine for the Cisco Business Dashboard Probe on site. Cisco Business mobile app Mobile app for Cisco Business Switch and Wireless products. Helps to set up a local network in minutes and provide easy management at your fingertips. Cisco Network Plug and Play (PnP) agent The Cisco Network Plug and Play solution provides a simple, secure, unified, and integrated offering to ease new branch or campus device rollouts or for provisioning updates to an existing network. The solution provides a unified approach to provision Cisco routers, switches, and wireless devices with a zero touch deployment experience. Supports Cisco PnP Connect Web user interface Built-in switch configuration utility for easy browser-ba
Dodání 3-5 dní
Upgradujte na 10GbE nyní pomocí našeho cenově dostupného switche 10GbE typu plug-and-play. 5portový 10GBASE-T neřízený switch QNAP QSW-3205-5T umožňuje snadný a jednoduchý upgrade na rychlost 10GbE. Toto cenově výhodné řešení zajišťuje stabilní a vysokory
Ano, centrál. sklad

PLANET GUP-805A-95W; PoE++ konvertor pro snadný přechod mezi metalickým a optickým vedením ( 100/1000 Base-X na 10/100/1000 Base-T ). Napájení v rozsahu DC 52–55 V (napájecí adaptér součástí),...
Ano, centrál. sklad
D-Link G530 - 5G NR AX3000 Wi-Fi 6 Router
Dodání 3-5 dní
52-port Gigabit Stackable Smart Managed Switch včetně 4 10g SFP+
Dodání 3 dny
PLANET GS-4210-16T2S; Spravovatelný přepínač 16 portů 1000Base-T, 2x SFP porty 100/1000Base-X. Web/SNMPv3/telnet správa, podpora IPv4/IPv6. VLAN 802.1Q, QoS-shaper, statický trunk LACP, IGMPv3, Spannig tree. ACL+...
Dodání 3-5 dní

8PORTOVÝ PŘEPÍNAČ DAHUA SF1008-EUR – Perfektní řešení pro malé počítačové sítě PŘEPÍNAČ SF1008-EUR je spolehlivý 8portový přepínač od společnosti Dahua, určený pro malé počítačové sítě a rezidenční sítě. Jeho robustní konstrukce a vysoký výkon z něj činí vynikající volbu pro ty, kteří hledají efekt
Dodání 3-5 dní
Objevte plný potenciál vaší sítě. Objevte spolehlivé a efektivní síťové zařízení typu plug-and-play. Díky 16 portům 10/100 Mbps s PoE a dalším 2 uplink portům (RJ45 1000 Mbps) a SFP portu (optické vlákno 1000 Mbps) vám zařízení umožňuje vytvořit flexibilní a škálovatelnou lokální síť (LAN) bez zbyt
Dodání 3-5 dní

Acer Connect Ovia T520 WiFi 7 Tri-band Mesh Router Part Number: FF.G3ATA.001 Parametry Model: BE9300 Wifi: 802.11 a/b/g/n/ac/ax/be 2x2 MIMO, Tri band 2.4GHz (688Mbps) / 5GHz (2882Mbps/160MHz) / 6GHz (5765Mbps) Rozhraní: MLO, 1x WAN 2.5GbE, 3x LAN 2.5GbE Procesor: 1.5 GHz Quad-Core ARM Processor Paměť: RAM 512MB DDR3L Storage: 128MB NAND Výbava: Acer Connect App, FOTA software update, WPS button, Pin Hole reset, 6 interních antén, Passive Cooling Bezpečnost: pokročilé šifrování, VPN, firewall, rodičovská kontrola Adaptér: 12 V / 2 A Ethernet kabel: Ano Fyzické parametry: o116x202 mm, 840 g Balení: 1 pack
Ano, centrál. sklad

PLANET IXT-900-2X1PD; Průmyslový 10G konvertor pro snadný přechod mezi metalickým a optickým vedením ( 10G/5G/2.5G/1G/100M Base-T na 10G/2.5G/1G/100M Base-X s duálním SFP+ portem). Průmyslové provede...
Ano, centrál. sklad

Intellinet Network Solutions SFP Modul MiniGBIC/SFP+ 10GBase-LR modul (507479)
Dodání 3-5 dní
Cisco Catalyst switch C1300-12XT-2X (12x10GbE,2xSFP+) - REFRESH
Ano, centrál. sklad

PLANET ICG-2515-NR; Průmyslová bezpečnostní brána 5G/LTE infrastruktury IoT/M2M (machine-to-machine), 3x LAN, 1x LAN/WAN, 1x WAN), 1x sériový port RJ-45 (DB9), 2x SIM slot (redundantní) , 2x digitální vst...
Ano, centrál. sklad

PLANET POE-E202 PoE extender pro prodloužení Ethernet segmentu 1000Base-T ze 100 m na delší vzdálenosti včetně podpory napájení IEEE 802.3af/at . Porty 1x napájený + 2x napájecí, výkon celkem 25 W , podpora přenosu VLAN, ESD+EFT ochrany. Řešení prodloužení segmentu ethernet včetně zvětšení dosahu napájení PoE (power over ethernet). Jedná se o jednoduché zařízení dovolující prodloužit maximální délku ethernet segmentu ze 100 m na 200 m nebo až 500 m včetně zachování napájení IEEE 802.3at zařízení na konci vedení. Aplikace extenderu je ideální v místě použití IP kamer nebo bezdrátových přístupových bodů na jejich delší přípojné vzdálenosti. Cenově se tak jedná o levné rozšíření možnosti instalovat napájená zařízení do míst vzdálenějších od centrálního switche nebo racku. Použití spočívá v jednoduchém vložení extenderu na přerušené vedení. ZÁKLADNÍ SPECIFIKACE Fyzické vlastnosti: Porty: 3 x RJ-45 10/100/1000Base-T Paměť: 2k MAC adres, buffer 2 Mb Propustnost: sběrnice 6 Gbps, provozně 4,46 Mpps Podpora přenosu: JumboFrame 10 KB Provedení: na zeď Napájení: IEEE 802.3at DC 52-56 V, celkový příkon do 36 W Ochrana: ESD do 2 kV, EFT do 2 kV Provozní teplota: 0 až +50 °C Rozměry: 140 x 77 x 28 mm Hmotnost: 234 g POE funkce: Celkový napájecí výkon: 25 W, IEEE 802.3af, IEEE 802.3at Počet injektorů: 1 x až 30,8 W (vstup), 2 x až 25 W Typ napájení: End-span Pokročilé funkce: Rozšiřuje dosah PoE na dalších 100 metrů
Ano, centrál. sklad

NETGEAR Smart GS752TXUP
Dodání 3-5 dní

Cisco switch CBS250-24T-4X - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Řada Cisco Business 250 představuje novou generaci cenově dostupných inteligentních switchů, které kombinují vysoký síťový výkon, zabezpečení a spolehlivost s komplexní sadou síťových funkcí potřebných pro spolehlivou síť malých firem. Záruka platná do End of Support 31. 10. 2029. Oznámení End of Life pro CISCO CBS250 Stránky produktu: CBS250-24T-4X Quick start guide: Quick start guide Switching capacity (All switches are wire-speed and nonblocking) Forwarding rate in millions of packets per second (mpps; 64-byte packets) 95,23 Switching capacity in Gigabits per second (Gbps) 128 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 4 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG) VLAN Support for up to 255 active VLANs simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Protocols for automatically propagating and configuring VLANs in a bridged domain IGMP (versions 1, 2, and 3) snooping Internet Group Management Protocol (IGMP) limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported) IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router HOL blocking Head-of-Line (HOL) blocking prevention Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP. Layer 3 routing IPv4 routing Wire-speed routing of IPv4 packets Up to 32 static routes and up to 16 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets Security Secure Sockets Layer (SSL) SSL encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported. IEEE 802.1X (authenticator role) Remote Authentication Dial-In User Service (RADIUS) authentication, guest VLAN, single/multiple host mode, and single/multiple sessions STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices, and secure autoconfig. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC]) Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses RADIUS Supports RADIUS authentication for management access. Switch functions as a client. Storm control Broadcast, multicast, and unknown unicast DoS prevention Denial-of-Service (DoS) attack prevention Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels Access Control Lists (ACLs) Support for up to 512 rules Drop or rate limit based on source and destination MAC, VLAN ID or IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides Time-based ACLs supported QoS Priority levels 8 hardware queues Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and class of service (802.1p/CoS) Class of service Port based; 802.1p VLAN priority based; IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based; Differentiated Services (DiffServ); classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer; egress shaping and rate control; per VLAN, per port, and flow based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.3 ad LACP, IEEE 802.1D (STP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, RFC 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 920, RFC 922, RFC 950, RFC 951, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1213, RFC 1215, RFC 1286, RFC 1350, RFC 1442, RFC 1451, RFC 1493, RFC 1533, RFC 1541, RFC 1542, RFC 1573, RFC 1624, RFC 1643, RFC 1700, RFC 1757, RFC 1867, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2030, RFC 2131, RFC 2132, RFC 2233, RFC 2576, RFC 2616, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 3416, RFC 4330 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet IPv6/IPv4 Dual Stack IPv6 Neighbor Discovery (ND) IPv6 stateless address auto configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) Internet Control Message Protocol (ICMP) version 6 IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) support USGv6 and IPv6 Gold Logo certified IPv6 QoS Prioritize IPv6 packets in hardware IPv6 ACL Drop or rate limit IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) snooping Deliver IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, Ping, Traceroute, Simple Network Time Protocol (SNTP), Trivial File Transfer Protocol (TFTP), Simple Network Management Protocol (SNMP), Remote Authentication Di
Ano, centrál. sklad

PLANET IPOE-270; Průmyslový injektor pro napájení po Ethernetovém kabelu, standard IEEE 802.3bt PoE++ do příkonu až 180 W , pracuje i na 1/2,5/5Gb propojení. Krytí IP30 , kovová skříň, pracovní teplota -40 až +75 °C , montáž na DIN lištu nebo přímo na...
Dodání 3-5 dní

Teltonika RS232 wireless access point - DAP142
Dodání 3-5 dní
Cisco Catalyst switch C1300-48P-4G Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu. Stránky produktu: C1300-48P-4G Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 77.38 Switching capacity in gigabits per second (Gbps) 104.0 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4093 VLANs simultaneously Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN Auto surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported) IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wire-speed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Security Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through a web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard Prevents edge devices not in the network administrator’s control from becoming STP root nodes STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) DHCP snooping Filters out DHCP messages with unregistered IP addresses and/or from unexpected or untrusted interfaces. This prevents rogue devices from behaving as DHCP servers IP Source Guard (IPSG) When IPSG is enabled at a port, the switch filters out IP packets received from the port if the source IP addresses of the packets have not been statically configured or dynamically learned from DHCP snooping. This prevents IP address spoofing Dynamic ARP Inspection (DAI) The switch discards ARP packets from a port if there are no static or dynamic IP/MAC bindings or if there is a discrepancy between the source or destination addresses in the ARP packet. This prevents man-in-the-middle attacks IP/MAC/port binding (IPMB) The preceding features (DHCP snooping, IPSG, and DAI) work together to prevent Denial-of-Service (DoS) attacks in the network, thereby increasing network availability Secure Core Technology (SCT) Makes sure that the switch will receive an
Ano, centrál. sklad
Improvizace. Přizpůsobování. Překonání obtíží. “Způsob myšlení může být velmi užitečný, ale někdy
Skladem v eshopu
TP-Link TL-SG3428XF JetStream 24-Port SFP L2+ Managed Switch se 4 10GE SFP+ Sloty Bleskurychlé odchozí připojení 10G - 4 sloty SFP+ s rychlostí 10 Gbit/s umožňují vysoce propustné širokopásmové připojení a přepínací kapacitu bez blokování. Gigabitové rychlosti - 20 gigabitových portů SFP a 4 gigabitové kombinované porty SFP/RJ45 nabízí vysokorychlostní a spolehlivé spojení s dalšími switchi a zařízeními. Integrováno do platformy Omada SDN - Funkce ZTP (Zero-Touch Provisioning), centralizovaná cloudová správa a inteligentní monitorování. Centralizovaná správa - Cloudový přístup a aplikace Omada pro maximální pohodlí a snadnou správu. Statické směrování - Pomáhá směrovat tok dat po lokální síti, čímž zajišťuje efektivní využívání síťových prostředků. Robustní strategie zabezpečení - Funkce vázání na adresu IP-MAC, ACL, zabezpečení portů, ochrana proti útokům DoS, funkce Storm Control, funkce DHCP Snooping, ověřování protokolem 802.1X a Radius a další funkce. Optimalizovaný přenos hlasu a videa v aplikacích - L2/L3/L4 QoS a funkce IGMP Snooping. Samostatná správa - Webové rozhraní, CLI (konzolový port, Telnet, SSH), SNMP, RMON a funkce Dual Image přináší pokročilé možnosti správy. Stránky produktu: https://www.tp-link.com/cz/business-networking/managed-switch/tl-sg3428xf/ Technické specifikace HARDWARE FEATURES Interface • 20× Gigabit SFP Ports • 4× Gigabit SFP/RJ45 Combo Ports • 4× 10G SFP+ Slots • 1× RJ45 Console Port • 1× Micro-USB Console Port Fan Quantity 1 Fan Power Supply Dual Reduant Power Supplies 100-240 V AC~50/60 Hz Dimensions (WxDxH) 17.3 × 8.7 × 1.7 in (440 × 220 × 44 mm) Mounting Rack Mountable Max Power Consumption 35.7 W (110 V/60 Hz) Max Heat Dissipation 121.81 BTU/hr (110 V/60 Hz) PERFORMANCE Switching Capacity 128 Gbps Packet Forwarding Rate 95.23 Mpps MAC Address Table 16 K Packet Buffer Memory 12 Mbit Jumbo Frame 9 KB SOFTWARE FEATURES Quality of Service • 8 priority queues • 802.1p CoS/DSCP priority • Queue scheduling - SP (Strict Priority) - WRR (Weighted Round Robin) - SP+WRR • Bandwidth Control - Port/Flow based Rating Limiting • Smoother Performance • Action for Flows - Mirror (to supported interface) - Redirect (to supported interface) - Rate Limit - QoS Remark L2 and L2+ Features • Link Aggregation - static link aggregation - 802.3ad LACP - Up to 8 aggregation groups, containing 8 ports per group • Spanning Tree Protocol - 802.1d STP - 802.1w RSTP - 802.1s MSTP - STP Security: TC Protect, BPDU Filter, Root Protect • Loopback Detection - Port based - VLAN based • Flow Control - 802.3x Flow Control - HOL Blocking Prevention • Mirroring - Port Mirroring - CPU Mirroring - One-to-One - Many-to-One - Tx/Rx/Both L2 Multicast • IGMP Snooping - IGMP v1/v2/v3 Snooping - Fast Leave - IGMP Snooping Querier - IGMP Authentication • IGMP Authentication • MLD Snooping - MLD v1/v2 Snooping - Fast Leave - MLD Snooping Querier - Static Group Config - Limited IP Multicast • MVR • Multicast Filtering: 256 profiles and 16 entries per profile VLAN • VLAN Group - Max 4K VLAN Groups • 802.1Q Tagged VLAN • MAC VLAN: 30 Entries • Protocol VLAN: Protocol Template 16, Protocol VLAN 16 • Private VLAN • GVRP • VLAN VPN (QinQ) - Port-Based QinQ - Selective QinQ • Voice VLAN Access Control List • Time-based ACL • MAC ACL - Source MAC - Destination MAC - VLAN ID - User Priority - Ether Type • IP ACL -Source IP - Destination IP - Fragment - IP Protocol - TCP Flag - TCP/UDP Port - DSCP/IP TOS - User Priority • Combined ACL • Packet Content ACL • IPv6 ACL • Policy - Mirroring - Redirect - Rate Limit - QoS Remark • ACL apply to Port/VLAN Security • IP-MAC-Port Binding - 512 Entries - DHCP Snooping - ARP Inspection - IPv4 Source Guard: 100 Entries • IPv6-MAC-Port Binding - 512 Entries - DHCPv6 Snooping - ND Detection - IPv6 Source Guard: 100 Entries • DoS Defend • Static/Dynamic Port Security - Up to 64 MAC addresses per port • Broadcast/Multicast/Unicast Storm Control - kbps/ratio control mode • 802.1X - Port base authentication - Mac base authentication - VLAN Assignment - MAB - Guest VLAN - Support Radius authentication andaccountability • AAA (including TACACS+) • Port Isolation • Secure web management through HTTPS with SSLv3/TLS 1.2 • Secure Command Line Interface (CLI) management with SSHv1/SSHv2 • IP/Port/MAC based access control IPv6 • IPv6 Dual IPv4/IPv6 • Multicast Listener Discovery (MLD) Snooping • IPv6 ACL • IPv6 Interface • Static IPv6 Routing • IPv6 neighbor discovery (ND) • Path maximum transmission unit (MTU) discovery • Internet Control Message Protocol (ICMP) version 6 • TCPv6/UDPv6 • IPv6 applications - DHCPv6 Client - Ping6 - Tracert6 - Telnet (v6) - IPv6 SNMP - IPv6 SSH - IPv6 SSL - Http/Https - IPv6 TFTP L3 Features • 16 IPv4/IPv6 Interfaces • Static Routing - 48 static routes • Static ARP - 128 Static Entries • Proxy ARP • Gratuitous ARP • DHCP Server • DHCP Relay - DHCP Interface Relay - DHCP VLAN Relay • DHCP L2 Relay Advanced Features • Automatic Device Discovery • Batch Configuration • Batch Firmware Upgrading • Intelligent Network Monitoring • Abnormal Event Warnings • Unified Configuration • Reboot Schedule MIBs • MIB II (RFC1213) • Interface MIB (RFC2233) • Ethernet Interface MIB (RFC1643) • Bridge MIB (RFC1493) • P/Q-Bridge MIB (RFC2674) • RMON MIB (RFC2819) • RMON2 MIB (RFC2021) • Radius Accounting Client MIB (RFC2620) • Radius Authentication Client MIB (RFC2618) • Remote Ping, Traceroute MIB (RFC2925) • Support TP-Link private MIB MANAGEMENT Omada App Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Centralized Management • Omada Cloud-Based Controller • Omada Hardware Controller (OC300) • Omada Hardware Controller (OC200) • Omada Software Controlle Cloud Access Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Zero-Touch Provisioning Yes. Requiring the use of Omada Cloud-Based Controller. Management Features • Web-based GUI • Command Line Interface (CLI) through the console port, telnet • SNMP v1/v2c/v3 - Trap/Inform - RMON (1,2,3,9 groups) • SDM Template • DHCP/BOOTP Client • 802.1ab LLDP/LLDP-MED • DHCP AutoInstall • Dual Image, Dual Configuration • CPU Monitoring • Cable Diagnostics • EEE • Password Recovery • SNTP • System Log OTHERS Certification CE, FCC, RoHS Package Contents • TL-SG3428XF Switch • Power Cord • Quick Installation Guide • Rackmount Kit • Rubber Feet System Requirements Microsoft Windows 98SE, NT, 2000, XP, Vista™ or Windows 7/8/10/11, MAC OS, NetWare, UNIX or Linux. Environment • Operating Temperature: 0–45 ? (32–113 ?); • Storage Temperature: -40–70 ? (-40–158 ?) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% RH non-condensing
Dodání 3-5 dní

Na popisu produktu pracujeme a doplníme jej v nejbližší možné době. Produkt je možné zakoupit
Skladem, dodání 2-4 dní

Ubiquiti Ufiquiti UFP -Viewport Unifi Chraňte viewport Poe - adaptér HDMI, 4K 30fps
Skladem, dodání 2-4 dní

USW-Enterprise-8-PoE UBNT UniFi Switch Enterprise 8 PoE UniFi Switch Enterprise 8 PoE je spolehlivý switch s managementem v desktop provedení. Jedné se o konfigurovatelný výkonný L3 přepínač s kapacitou 80 Gbps , rychlostí směrování 59,52 Mpps a 1,3" dotykovým displejem. Switch je osazen osmi 2,5G PoE+ RJ-45 a dvěma 10G SFP+ sloty pro uplink. Celková napájecí PoE+ kapacita switche je 120 W (802.3af/at) . Switch lze navíc upevnit ke zdi, díky přiloženému držáku. 8x 2,5G 802.3af/at PoE+ RJ-45 port 2x 10G SFP+ slot 120 W PoE kapacita (802.3af/at) 1,3" dotykový displej Možnost montáže na stěnu (montážní sada je součástí) UniFi Controller UniFi Switche jsou součástí platformy UniFi SDN (Software-Defined Networking), která umožňuje dohled a řízení koncových zařízení v síti, vše přehledně v grafickém rozhraní UniFi Controller . UniFi Controller poskytuje monitoring sítě, správu UniFi zařízení, mapy, zobrazení statistik a nastavení účtů. UniFi Controller je neustále vylepšován, a proto doporučujeme používat aktuální verzi, kterou stahujte na stránkách Ubiquiti v sekci Downloads . ZÁKLADNÍ SPECIFIKACE Porty: 8x 2,5G RJ-45, 2x 10G SFP+ Kapacita switche: 80 Gbps Rychlost směrování: 59,52 Mpps Podpora PoE: ano (802.3af/at, 120 W PoE budget) Rozměry: 248 x 200 x 44 mm Hmotnost: 2,4 kg Užitečné odkazy: stránky výrobce UBNT.com aktuální verze airOS datasheety, uživatelské příručky výpočet parametrů bezdrátového spoje - AirLink návody pro začátečníky - BeansTalk video-návody (ubnt youtube channel) Ubiquiti Wiki Ubiquiti oficiální fórum
Skladem v eshopu

NATEC multiport Fowler Plus USB-C->HUB USB 3.0 3x HDMI 4K USB-C PD RJ45 SD Micro SD
Dodání 3 dny
Cisco Catalyst switch C1300-12XS - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Sada pro montáž do racku není součástí balení. Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu. Stránky produktu: C1300-12XS Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 178.57 Switching capacity in gigabits per second (Gbps) 240 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4093 VLANs simultaneously Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN Auto surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported) IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wire-speed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Stacking Hardware stacking Up to 8 switches in a stack. Up to 200 ports managed as a single system with hardware failover Stacking is supported on the following models: Family 1: C1300-16P-4X, C1300-24T-4X, C1300-24P-4X, C1300-24FP-4X, C1300-48T-4X, C1300-48P-4X, C1300-48FP-4X, C1300-8MGP-2X, C1300-24MGP-4X, C1300-48MGP-4X Family 2: C1300-12XT-2X, C1300-12XS, C1300-16XTS, C1300-24XS, C1300-24XT, C1300-24XTS PIDs from the same Family can be stacked together. Cross-stacking between Families is not supported. High availability Fast stack failover delivers minimal traffic loss. Support for LAG across multiple units in a stack Plug-and-play stacking configuration/management Active/standby for resilient stack control Auto-numbering Hot swap of units in stack Ring and chain stacking options, auto stacking port speed, flexible stacking port options High-speed stack interconnects Cost-effective high-speed 10 Gigabit Ethernet fiber interfaces Security Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through a web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP
Ano, centrál. sklad
Aruba Instant On 1830 48G 4SFP 370W Switch (24x RJ45 10/100/1000 24x Class4 PoE) Aruba Instant On 1830 8G Switch (JL810A) Aruba Instant On 1830 8G 4p Class4 PoE 65W Switch (JL811A) Aruba Instant On 1830 24G 2SFP Switch (JL812A) Aruba Instant On 1830 24G 12p Class4 PoE 2SFP 195W Switch (JL813A) Aruba Instant On 1830 48G 4SFP Switch (JL814A) Aruba Instant On 1830 48G 24p Class4 PoE 4SFP 370W Switch (JL815A) I/O ports and slots 8 RJ-45 autosensing 10/100/1000 ports IEEE 802.3af Class 3 PD (port 1) (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE-TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 8 RJ-45 autosensing 10/100/1000 ports IEEE 802.3at Class 4 PoE (ports 1-4) (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE-TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 24 RJ-45 autosensing 10/100/1000 ports (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE-TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 2 SFP 1GbE ports 24 RJ-45 autosensing 10/100/1000 ports IEEE 802.3at Class 4 PoE (ports 1-12) (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE-TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 2 SFP 1GbE ports 48 RJ-45 autosensing 10/100/1000 ports (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE-TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 4 SFP 1GbE ports 48 RJ-45 autosensing 10/100/1000 ports IEEE 802.3at Class 4 PoE (ports 1-24) (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE-TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 4 SFP 1GbE ports Physical Characteristics Dimensions 157.0(d) x 173.0(w) x 39.1(h) mm 195.1(d) x 245.1(w) x 43.9(h) mm 215.9(d) x 443.0(w) x 43.9(h) mm 253.0(d) x 443.0(w) x 43.9(h) mm 253.0(d) x 443.0(w) x 43.9(h) mm 351.0(d) x 443.0(w) x 43.9(h) mm Weight 1.70 lb (0.77 kg) 3.40 lb (1.54 kg) 5.50 lb (2.49 kg) 7.65 lb (3.47 kg) 7.80 lb (3.54 kg) 10.90 lb (4.94 kg) Processor and Memory ARM Cortex-A9 @ 800MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5MB ARM Cortex-A9 @ 800MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5MB ARM Cortex-A9 @ 800MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5MB ARM Cortex-A9 @ 800MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5MB "RM Cortex-A9 @ 800MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5MB ARM Cortex-A9 @ 800MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5MB Aruba Instant On 1830 8G Switch (JL810A) Aruba Instant On 1830 8G 4p Class4 PoE 65W Switch (JL811A) Aruba Instant On 1830 24G 2SFP Switch (JL812A) Aruba Instant On 1830 24G 12p Class4 PoE 2SFP 195W Switch (JL813A) Aruba Instant On 1830 48G 4SFP Switch (JL814A) Aruba Instant On 1830 48G 24p Class4 PoE 4SFP 370W Switch (JL815A) Performance 100 Mb latency < 5.2 uSec < 5.2 uSec < 5.2 uSec < 5.2 uSec < 5.2 uSec < 5.2 uSec 1000 Mb latency < 2.8 uSec < 2.8 uSec < 2.8 uSec < 2.8 uSec < 2.8 uSec < 2.8 uSec 10000 Mb latency n/a n/a n/a n/a n/a n/a Throughput (Mpps) 11.90 Mpps 11.90 Mpps 38.68 Mpps 38.68 Mpps 77.37 Mpps 77.37 Mpps Capacity 16 Gbps 16 Gbps 52 Gbps 52 Gbps 104 Gbps 104 Gbps MAC address table size (# of entries) 8,000 entries 8,000 entries 16,000 entries 16,000 entries 16,000 entries 16,000 entries Reliability MTBF (years) 188.2 105.9 203.6 96.6 114.4 83.5 Environment Operating temperature 32°F to 104°F (0°C to 40°C) 32°F to 104°F (0°C to 40°C) 32°F to 104°F (0°C to 40°C) 32°F to 104°F (0°C to 40°C) 32°F to 104°F (0°C to 40°C) 32°F to 104°F (0°C to 40°C) Operating relative humidity 15% to 95% @ 104°F (40°C) 15% to 95% @ 104°F (40°C) 15% to 95% @ 104°F (40°C) 15% to 95% @ 104°F (40°C) 15% to 95% @ 104°F (40°C) 15% to 95% @ 104°F (40°C) Nonoperating/ storage temperature -40°F to 158°F (-40°C to 70°C) -40°F to 158°F (-40°C to 70°C) -40°F to 158°F (-40°C to 70°C) -40°F to 158°F (-40°C to 70°C) -40°F to 158°F (-40°C to 70°C) -40°F to 158°F (-40°C to 70°C) Nonoperating/ storage relative humidity 15% to 95% @ 140°F (60°C) 15% to 95% @ 140°F (60°C) 15% to 95% @ 140°F (60°C) 15% to 95% @ 140°F (60°C) 15% to 95% @ 140°F (60°C) 15% to 95% @ 140°F (60°C) Altitude up to 10,000 ft (3 km) up to 10,000 ft (3 km) up to 10,000 ft (3 km) up to 10,000 ft (3 km) up to 10,000 ft (3 km) up to 10,000 ft (3 km) Acoustics 1 Fanless Fanless Fanless LWAd = 3.1 Bel LpAm (Bystander) = 17 dB LWAd = 3.4 Bel LpAm (Bystander) = 19 dB LWAd = 4.0 Bel LpAm (Bystander) = 25 dB Notes: 1 Acoustics measured in 23°C semi-anechoic chamber with a loading of 100% traffic and (for JL813A and JL815A) 50% PoE on all ports. Measured in accordance with ISO 7779. Declared in accordance with ECMA-109:2010. Values presented are the Declared A-Weighted Sound Power Level (LWAd) and the mean Bystander A-Weighted Sound Pressure Level (LpAm) 100% traffic Fanless Fanless Fanless LWAd = 3.1 Bel LpAm (Bystander) = 17 dB LWAd = 3.4 Bel LpAm (Bystander) = 19 dB LWAd = 3.5 Bel LpAm (Bystander) = 20 dB 100% traffic / 0% PoE Fanless Fanless Fanless LWAd = 3.1 Bel LpAm (Bystander) = 17 dB - LWAd = 3.5 Bel LpAm (Bystander) = 20 dB 100% traffic / 50% PoE Fanless Fanless Fanless LWAd = 3.1 Bel LpAm (Bystander) = 17 dB - LWAd = 4.0 Bel LpAm (Bystander) = 25 dB 100% traffic / 100% PoE Fanless Fanless Fanless LWAd = 5.1 Bel LpAm (Bystander) = 35 dB - LWAd = 5.7 Bel LpAm (Bystander) = 41 dB Aruba Instant On 1830 8G Switch (JL810A) Aruba Instant On 1830 8G 4p Class4 PoE 65W Switch (JL811A) Aruba Instant On 1830 24G 2SFP Switch (JL812A) Aruba Instant On 1830 24G 12p Class4 PoE 2SFP 195W Switch (JL813A) Aruba Instant On 1830 48G 4SFP Switch (JL814A) Aruba Instant On 1830 48G 24p Class4 PoE 4SFP 370W Switch (JL815A) Electrical Characteristics Frequency 50Hz/60Hz 50Hz/60Hz 50Hz/60Hz 50Hz/60Hz 50Hz/60Hz 50Hz/60Hz AC voltage 100-127VAC / 200- 240VAC 100-127VAC / 200- 240VAC 100-127VAC / 200- 240VAC 100-127VAC / 200- 240VAC 100-127VAC / 200- 240VAC 100-127VAC / 200- 240VAC Current 12V -- 1.0A 1.0A/0.5A 0.4A/0.3A 2.7A/1.4A 0.9A/0.6A 5.2A/2.6A Maximum power rating 100-127V: 8.09W 200-220V: 8.05W 100-127V: 86.07W 200-220V: 83.67W 100-127V: 19.1W 200-220V: 19W 100-127V: 244.6W 200-220V: 237.2W 100-127V: 40.2W 200-220V: 40W
Skladem, dodání 2-4 dní

PLANET GSD-805v2; 8portový Gigabitový desktopový přepínač. Portové VLAN s možnou izolací portů. ESD+EFT ochrany proti elektrostatice a přepětí. Energeticky úsporný dle IEEE 802.3az. Kovová skříň, interní napájecí zdroj, bez ventilátorů. Gigabitové pře...
Ano, centrál. sklad

CyberPower PDU24005 poskytuje výstup z jednotky UPS, generátoru nebo síťového napájení pro více připojených zařízení v infrastruktuře IT. Duální napájecí kabely lze zapojit do samostatných nezávislých zdrojů napájení a zajistit tak redundanci pro zařízení s jedním vstupním napájením. Pokud zvolený zdroj energie překročí požadované prahové hodnoty nebo selže, ATS PDU se automaticky přepne na druhý zdroj napájení, aby byl zajištěn nepřetržitý provoz. Jednotka je vybavena multifunkčním displejem vyměnitelným za provozu, který zobrazuje provozně důležité hodnoty v reálném čase včetně proudu, vstupního napětí, spotřeby energie v ampérech a wattech. Digitální LCD displej lze také barevně konfigurovat, což umožňuje uživatelům snadnou údržbu a názorné sledování ATS PDU. Uživatelé mohou měnit barvy LCD a snadno tak identifikovat zařízení mezi více počítači v serverovně a IT prostředí. Firmware lze také pohodlně upgradovat prostřednictvím portu USB, což zajišťuje, že jsou uživatelům k dispozici nejnovější funkce a aktualizace. Produkt lze připojit k počítači prostřednictvím sériového portu pro zajištění lokální správy ATS PDU. Model PDU24005 Funkce Metered Fáze (Vstup/výstup) 1:1 Vstup Maximální vstupní proud 16 A Jmenovité vstupní napětí 200 - 240 Vac Vstupní kmitočet 50 / 60 Hz Typ vstupu IEC-320 C20 (2) Délka napájecího kabelu 3,05 m Výstup Jmenovité výstupní napětí 200 - 240 Vac Výstupní kmitočet 50 / 60 Hz Počet výstupů 10 Typ výstupů IEC-320 C13 (8), IEC-320 C19 (2) Ochrana proti přetížení Ne Správa a komunikace Ovládací SW Intelligent PDU Web Interface LCD informační displej Ano - kW, Voltage, Amperage, Network Information, HW/FW Version Porty RJ45 - DB9 sériový MNGMT karta Volitelně (RMCARD205) Podporované protokoly SNMP/HTTP Fyzické parametry Rozměry (V x Š X H) (mm) 44 x 433 x 215 Hmotnost (kg) 3.2 Výška v racku 1U Informace výrobce Stránka produktu Zde Záruka 24 měsíců Dodávka obsahuje ATS, montážní držáky, sada šroubů, vyvazovací pásky, uchacení kabelů, RJ45 / DB9 sériový port připojení kabel, uživatelský manuál, registrační karta, CD napájecí šňůra 10 ft IEC-320 C19/C20 (2)
Ano, centrál. sklad
Přístupový bod Ubiquiti Unifi UAP Nano HD 5 PCS. (UAP-nanohd-5)
Dodání 3-5 dní
DIGITUS USB-C 3.0 Duální HDMI KVM přepínač, 2portový, 4K60Hz, řada Core Dva počítače, dva monitory – kompletní ovládání pomocí jediné kombinace klávesnice a myši a dokonale ostrý obraz v rozlišení 4K. Přepínač DIGITUS® USB-C 3.0 Duální HDMI KVM z řady Cor
Ano, centrál. sklad

Mesh systém, podpora Wi-Fi standardů 802.11 a/b/g/n/ac, rychlost až 1900 MB/s při souběžném 2pásmovém připojení (2.4 GHz: 600 Mbps + 5 GHz: 1300 Mbps).3x LAN/WAN, podpora IPV4 a IPV6. Šifrování WPA2-PSK, MU-MIMO, Beamforming, rodičovská kontrola. Bílá.
Skladem v eshopu

TP-Link M7350; LTE router M7350 je špičkové zařízení pro sdílení v bezdrátových 4G sítích. Stačí vložit 4G SIM kartu do zařízení a okamžitě vytvořit volitelný dvoupásmový Wi-Fi hotspot. Směrovač M7350 dokáže díky rych...
Ano, centrál. sklad
GWN7062E je bezpečný dvoupásmový router AX3000 poháněný nejnovější technologií Wi-Fi 6 (802.11ax). Ideální pro malé kanceláře a pracovníky vykonávající činnost z domova. GWN7062E poskytuje 2,4G 2×2:2 a 5G 3x3:2 MU-MIMO s technologií XTRA Range s beamformingem pro maximální propustnost sítě a rozšíř
Ano, centrál. sklad
LANCOM 1800VAW EU
Dodání 3-5 dní
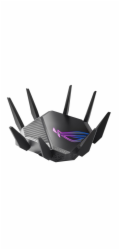
Router Asus Asus GT-AxE11000
Skladem v eshopu
Rozbočovač z USB-C na 2x USB 3.0 a 1x USB 2.0. Rozměry produktu (š x h x v): 6,68 x 4,14 x 1,05 cm Hmotnost produktu: 36,5 g Co je obsaženo v krabici: Rozbočovač z USB-C na 3x USB-A Dokumentace HP Elite x2 1012 G2 (1LV21EA) HP Elite x2 1013 G3 (2TT29ES, 2TS94EA) HP EliteBook 1030 G1 (X2F02EA, X2F03EA) HP EliteBook 1040 G3 (Y8R13EA, V1B07EA, V1A83EA, V1A81EA) HP EliteBook 1040 G4 (1EQ14EA, 1EP90EA, 1EP77EA, 1EP15EA, 1EP72EA) HP EliteBook 725 G3 (P4T48EA) HP EliteBook 725 G4 (Z2V98EA) HP EliteBook 745 G3 (T4H58EA) HP EliteBook 745 G4 (Z2W04EA) HP EliteBook 755 G3 (T4H59EA) HP EliteBook 755 G4 (Z2W12EA) HP EliteBook 820 G3 (T9X49EA, V1C05EA) HP EliteBook 820 G4 (Z2V77EA, Z2V91EA) HP EliteBook 830 G5 (3JW96EA, 3JX24EA) HP EliteBook 840 G3 (V1C06EA, T9X25EA, T9X21EA, X2F51EA, T9X29EA, T9X59EA) HP EliteBook 840 G4 (Z2V62EA, Z2V44EA, 2NB10ES) HP EliteBook 840 G5 (3JY08ES, 3JX65EA, 3JX27EA, 3JY07ES) HP EliteBook 850 G3 (T9X18EA, V1C07EA, V1C48EA) HP EliteBook 850 G4 (Z2W85EA, Z2W82EA, Z2W94EA) HP EliteBook 850 G5 (2FH32AV, 3JY09ES, 3JX13EA, 3JX19EA) HP EliteBook Folio G1 (V1C41EA) HP EliteBook x360 1020 G2 (1EM62EA, 1EP66EA, 1EM56EA) HP EliteBook x360 1030 G2 (Z2W63EA, Z2W74EA, Z2W73EA, 1EP08EA) HP EliteBook x360 1030 G3 (4QZ23ES, 4QZ22ES, 3ZH02EA, 4QZ21ES) HP Chromebook 14 G5 (3GJ76EA) HP Pro x2 612 G2 (L5H59EA, L5H56EA, L5H67EA) HP ProBook 640 G2 (T9X00EA, T9X07EA) HP ProBook 640 G3 (Z2W32EA) HP ProBook 640 G4 (3JY19EA, 3JY22EA, 3ZG57EA) HP ProBook 645 G3 (Z2W15EA) HP ProBook 650 G2 (V1C30EA, V1C09EA) HP ProBook 650 G3 (Z2W60EA, Z2W48EA, 2TM78ES) HP ProBook 650 G4 (3ZG58EA, 3UP84EA, 3UN48EA, 3ZG59EA, 4QZ20ES) HP ProBook 655 G2 (V1C08EA) HP ProBook 655 G3 (Z2W19EA) HP ProBook x360 11 G1 (Z3A45EA, Z2Z54ES) HP ZBook 14u G4 (1RQ70EA, 1RQ67EA) HP ZBook 14u G5 (2ZC32ES, 2ZC03EA, 2ZC31ES, 2ZC33ES, 2ZC34EA) HP ZBook 15 G3 (T7V54EA, V2D00AW, 1RQ39ES, T7V52EA, X3W51AW, T7V51EA) HP ZBook 15 G5 (2ZC42EA, 2ZC64EA, 2ZC40EA, 4QH14EA) HP ZBook 15u G3 (T7W10EA, T7W14EA, T7W16EA, T7W12EA) HP ZBook 15u G5 (2ZC08EA, 2ZC30ES, 2ZC29ES) HP ZBook 15v G5 (2ZC56EA) HP ZBook 17 G3 (T7V63EA, T7V60EA, T7V62EA, V2D21AW) HP ZBook 17 G4 (1RQ84EA, Y6K25EA, 1RQ79EA, 1RQ80EA, Y6K23EA, Y6K36EA) HP ZBook 17 G5 (4QH25EA, 2ZC68EA, 2ZC45EA, 4QH26EA, 2ZC47EA, 2ZC48EA, 4QH41ES, 4QH34ES) HP ZBook Studio G3 (T7W04EA) HP ZBook Studio G4 (Y6K16EA, Y6K32EA, Y6K15EA) HP ZBook Studio G5 (4QH10EA) HP ZBook Studio x360 G5 (4QH13EA)
Dodání 3-5 dní

Switch Intellinet Network Solutions Inellinet 561921 Switch 2.5g, 10/100/1000/2500, 5x RJ45 Poe+ 55
Skladem, dodání 2-4 dní
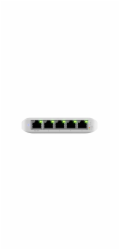
USW-Flex-Mini je maličký 5-portový Gigabitový switch se správou přes UniFi Controller od Ubiquiti Networks v desktop provedení s prvním portem podporující PoE In. PoE IN na Eth1 Jeho největší předností je gigabitový POE IN na portu č.1 pro snadnou exp
Skladem v eshopu
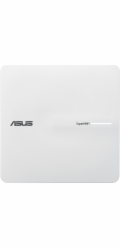
ASUS ExpertWiFi EBA63 AX3000 Dual-Band WiFi 6 (802.11ax) PoE Access Point, podpora až 5 SSID a VLAN, Self-defined Network, podpora PoE & PoE+, aplikace pro snadnou správu, kompatibilní s AiMesh Bezproblémové a rozšiřitelné připojení — Užijte si nepřetržitý roaming s WiFi 6 rychlostí až 3000 Mb/s, podporou až 100 aktivních zařízení a snadnou škálovatelností, abyste splnili vyvíjející se potřeby vaší podnikové sítě. Zabezpečené a segmentované sítě – Snadné nastavení WiFi sítě prostřednictvím Self-defined Networks a vylepšené podnikové zabezpečení s podporou VLAN, které nabízí až pět SSID pro segregaci zařízení a stanovení priorit v různých obchodních scénářích. Flexibilní nasazení s PoE – Podpora připojení Power over Ethernet (PoE) a AC adaptérů, což poskytuje všestranné možnosti instalace. Přizpůsobí se jakémukoli prostoru — Podporuje stropní a nástěnnou montáž, aby se vešly do různých podnikových prostředí s větší flexibilitou. Vyrobeno pro bezpečnost a spolehlivost — V souladu s normami IEC 60601-1-2 a s horní polovinou zařízení vyrobenou z materiálů, které splňují normu hořlavosti plastů UL94 5VB*, zajišťuje EBA63 stabilní a spolehlivé spojení. Specifikace Technické Specifikace Síťový standard IEEE 802.11a IEEE 802.11b IEEE 802.11g WiFi 4 (802.11n) WiFi 5 (802.11ac) WiFi 6 (802.11ax) IPv4 IPv6 Datový přenos 802.11a: až 54 Mbps 802.11b: až 11 Mbps 802.11g: až 54 Mbps WiFi 4 (802.11n): až 300 Mbps WiFi 5 (802.11ac): až 1734 Mbps WiFi 6 (802.11ax) (2,4 GHz): až 574 Mbps WiFi 6 (802.11ax) (5 GHz): až 2402 Mbps Anténa 4x Vnitřní anténa Paměť 256 MB Flash 512 MB RAM Operační frekvence 2.4 GHz 5 GHz Konektory 1x Gigabit Ethernet Port (Podporuje PoE) Napájení 802.3af PoE 12 V s max. 1,5 A proud DC (síťový adaptér součástí dodávky) Váha 426 g
Skladem v eshopu
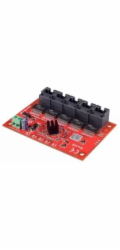
ASW-5-50-OF – 5portový gigabitový LAN switch 10/100/1000 Mb/s ASW-5-50-OF je moderní síťové zařízení nabízející pět gigabitových portů s rychlostí 10/100/1000 Mb/s. Díky své všestrannosti je ideální pro širokou škálu aplikací, od malých kanceláří až po složitější dohledové systémy. ASW-5-50-OF je p
Dodání 3-5 dní

Ruijie Networks RG-ES206GS-P network switch Managed L2 Gigabit Ethernet (10/100/1000) Power over Ethernet (PoE) Black
Dodání 3-5 dní
LANCOM 1803VAW EU
Dodání 3-5 dní
Switch od značky TP-Link, 24× GLan, správa přes Omada SDN, VLAN, QoS, tichý chod, odolné kovové tělo, možnost instalace na stůl i do racku, snadná instalace plug-and-play.
Skladem v eshopu
TP-Link Deco M5(2-pack) Deco Wi-Fi pro celý dům Deco je nejjednodušší cesta, jak zaručit, aby Wi-Fi signál byl silný v každém koutku vašeho domu. Užijte si rychlé a stabilní Wi-Fi připojení i pro celou armádu zařízení s pokrytím 350 m2. Nastavení již nemůže být snadnější díky aplikaci Deco, která vás provede jednotlivými kroky. Deco využívá systém více jednotek současně, které zajistí bezproblémové pokrytí signálem Wi-Fi a přecházení mezi jeho jednotlivými částmi v rámci celého domu – zbavte se míst se slabým signálem jednou provždy! Díky vyspělé technologii Deco Mesh jednotky vzájemně spolupracují a vytvářejí jednu sjednocenou síť v celém domě s jedním názvem. Když budete domem procházet, zařízení se budou automaticky připojovat vždy k té jednotce Deco, která jim zajistí signál s nejvyšší možnou rychlostí. Systém Deco M5 se dvěma jednotkami zvládne pokrýt 350 m2. A pokud byste potřebovali pokrýt ještě větší plochu, stačí kdykoli přidat další jednotku Deco. Deco M5 poskytuje rychlé a stabilní připojení s rychlostí až 1267 Mb/s a funguje ve spojení s jakýmkoli typem poskytovatele internetového připojení (ISP) a modemem. Deco dokáže zvládat provoz i pro velmi zatížené sítě a poskytuje připojení bez zadrhávání a zpoždění pro více než 100 zařízení současně. Bezpečnostní balík TP-Link HomeCare™ je sada individuálně přizpůsobených a zabezpečených funkcí, která obsahuje rodičovskou kontrolu, integrovaný antivirus a řízení kvality služeb (QoS). Nastavení je ještě snadnější než dosud díky aplikaci Deco, která vás provede jednotlivými kroky Stránky produktu: https://www.tp-link.com/cz/home-networking/deco/deco-m5/v2%20(2-pack)/ Technické specifikace WIRELESS Standards Wi-Fi 5 IEEE 802.11ac/n/a 5 GHz IEEE 802.11n/b/g 2.4 GHz WiFi Speeds AC1300 5 GHz: 867 Mbps (802.11ac) 2.4 GHz: 400 Mbps (802.11n) WiFi Range 3-5 Bedroom Houses (3-pack) TP-Link Mesh Technology Optional Ethernet backhaul work together to link Deco units to provide seamless coverage 4× Antennas (Internal) Multiple antennas form a signal-boosting array to cover more directions and large areas Beamforming Concentrates wireless signal strength towards clients to expand WiFi range WiFi Capacity Medium Dual-Band Distribute devices to different bands for optimal performance MU-MIMO Simultaneously communicates with multiple MU-MIMO clients Working Modes Router Mode Access Point Mode HARDWARE Ethernet Ports 2× Gigabit Ports *Per Deco Unit Supports WAN/LAN auto-sensing Buttons Reset Button SECURITY WiFi Encryption WPA-Personal WPA2-Personal Network Security SPI Firewall Access Control HomeCare™ Antivirus Malicious Site Checker Port Intrusion Prevention Infected Device Isolation Notification and Log Guest Network 1× 5 GHz Guest Network 1× 2.4 GHz Guest Network SOFTWARE Protocols IPv4 IPv6 Service Kits HomeCare™ Learn More> Parental Controls HomeCare™ Parental Controls Custom Profiles Content Filtering URL FIltering Time Limit Time Schedule (Bed Time) Log Insight Usage Monitor Monthly Reports WAN Types Dynamic IP Static IP PPPoE PPTP L2TP Quality of Service HomeCare™ QoS QoS by Device QoS by Application Cloud Service OTA Firmware Upgrade TP-Link ID DDNS NAT Forwarding Port Forwarding UPnP IPTV IGMP Proxy IGMP Snooping Bridge Tag VLAN DHCP Address Reservation DHCP Client List Server DDNS TP-Link Management Deco App TEST DATA WiFi Transmission Power CE: FCC: PHYSICAL Dimensions (W×D×H) 4.7 × 4.7 × 1.5 in (120 × 120 × 38 mm) Package Contents Deco M5 (3-pack) 3 Deco M5 Units 1 RJ45 Ethernet Cable 3 Power Adapters 1 Quick Installation Guide Deco M5 (2-pack) 2 Deco M5 Units 1 RJ45 Ethernet Cable 2 Power Adapters 1 Quick Installation Guide Deco M5 (1-pack) 1 Deco M5 Unit 1 RJ45 Ethernet Cable 1 Power Adapter 1 Quick Installation Guide OTHERS System Requirements Android 5.0 or later iOS 9.0 or later *Note: The minimum system requirements will be updated alongside updates to the app, subject to official website information. Certifications CE, FCC, IC, NCC, BSMI, IDA, RCM, JPA, JRF, VCCI, KC, RoHS Environment Operating Temperature: 0°C~40°C (32°F ~104°F) Storage Temperature: -40°C~70°C (-40°F ~158°F) Operating Humidity: 10%~90% non-condensing Storage Humidity: 5%~90% non-condensing
Ano, centrál. sklad
TP-Link ER8411 Omada VPN Router s 10G porty Integrováno do Omada SDN - Zero-Touch Provisioning (ZTP), centralizovaná správa cloudu a inteligentní monitorování. Centralizovaná správa - Přístup ke cloudu a aplikace Omada pro maximální pohodlí a snadnou správu. Dva 10GE SFP+ porty - 1× WAN a 1× WAN/LAN 10GE SFP+ porty poskytují vysokorychlostní agregační konektivitu. Až 10 portů WAN - Porty Fiber a RJ45 WAN s vyvážením zátěže zvyšují míru využití vícelinkového širokopásmového připojení. Vysoce bezpečná VPN - SSL/IPSec/PPTP/L2TP VPN & OpenVPN/L2TP přes IPSec VPN jsou ideální pro použití ve více síťových větvích a pro WFH. Bohaté bezpečnostní funkce - Výkonná brána firewall, obrana DoS, filtrování IP/MAC/URL a vazba IP-MAC a aktivace ALG jedním kliknutím poskytují prvotřídní zabezpečení. Learn more about Omada Cloud SDN>? Learn more about TP-Link 10G Multi-Gig technology > Stránky produktu: https://www.tp-link.com/us/business-networking/omada-sdn-router/er8411/ Technické specifikace HARDWARE FEATURES Standards and Protocols • IEEE 802.3, 802.3u, 802.3ab, IEEE 802.3x, IEEE 802.1q • TCP/IP, DHCP, ICMP, NAT, PPPoE, NTP, HTTP, HTTPS, DNS, IPSec, PPTP, L2TP, OpenVPN, SNMP Interface • 2× 10GE SFP+ Ports (1 WAN, 1 WAN/LAN) • 1× 1GE SFP WAN/LAN Ports • 8× 1GE RJ45 WAN/LAN Ports • 1× RJ45 Console Ports • 2× USB Ports (Connecting 4G/3G Modem as WAN Backup) Button Reset Button Power Supply Redundant Dual Power Supplies (100–240 VAC, 50/60 Hz) LED PWR, SYS, WAN, LAN, USB, FAN Dimensions (WxDxH) 17.3 × 8.7 × 1.7 in (440 × 220 × 44 mm) BASIC FUNCTIONS WAN Connection Type • Static/Dynamic IP • PPPoE • PPTP • L2TP • 6to4 Tunnel • Pass-Through • Mobile Broadband: 4G/3G modem for backup via USB port MAC Clone Modify WAN/LAN MAC Address DHCP • DHCP Server/Client • DHCP Address Reservation • Multi-net DHCP • Multi-IP Interfaces IPv6 Yes VLAN 802.1Q VLAN IPTV IGMP v2/v3 Proxy ADVANCED FUNCTIONS ACL IP/Port/Protocol/Domain Name Filtering Advanced Routing • Static Routing • Policy Routing Bandwidth Control • IP/Port-based Bandwidth Control • Guarantee & Limited Bandwidth Load Balance • Intelligent Load Balance • Application Optimized Routing • Link Backup (Timing, Failover) • Online Detection NAT • One-to-One NAT • Multi-Net NAT • Virtual Server • Port Triggering • NAT-DMZ • FTP/H.323/SIP/IPSec/PPTP ALG, UPnP Security • SPI Firewall • VPN Passthrough • FTP/H.323/PPTP/SIP/IPsec ALG • DoS Defence, Ping of Death • Local Management Session Limit IP-based Session Limit SECURITY Filtering WEB Group Filtering URL Filtering Web Security ARP Inspection • Sending GARP Packets • ARP Scanning • IP-MAC Binding Attack Defense • TCP/UDP/ICMP Flood Defense • Block TCP Scan (Stealth FIN/Xmas/Null) • Block Ping from WAN Access Control Source/Destination IP Based Access Control AUTHENTICATION Web Authentication • No Authentication • Simple Password • Hotspot(Local User / Voucher / SMS / Radius) • External Radius Sever • External Portal Sever • Facebook Check-In • Instagram Follow MANAGEMENT Omada App Yes Centralized Management • Omada Hardware Controller (OC300) • Omada Hardware Controller (OC200) • Omada Software Controller • Omada Cloud-Based Controller Cloud Access Yes (Through OC300, OC200, Omada Software Controller, or Omada Cloud-Based Controller) Service Dynamic DNS (Dyndns, No-IP, Peanuthull, Comexe) Maintenance • Time Setting • Diagnostic • Firmware Upgrade • Factory Defaults/Reboot • Backup&Restore • System Log • Remote Management • Statistics • Controller Settings • SNMP Management Features • Automatic Device Discovery • Intelligent Network Monitoring • Abnormal Event Warnings • Unified Configuration • Reboot Schedule • Captive Portal Configuration OTHERS Certification CE, FCC, RoHS Package Contents • Omada 10G Multi-WAN Security Gateway ER8411 • Power Cord • Rack-Mount Kit • Quick Installation Guide Environment • Operating Temperature: 0–40 ? (32–104 ?); • Storage Temperature: -40–70 ? (-40–158 ?) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% RH non-condensing
Skladem v eshopu
GS1920-48v2, 48 Port Smart Managed Switch 48x Gigabit Copper and 4x Gigabit dual pers., hybird mode, standalone or NebulaFlex Cloud Inteligentní řízený přepínač v novém atraktivním provedení! Produkty řady GS1920v2 s novým stylovým vzhledem navazují n
Dodání 3-5 dní
Cisco Meraki MX68W Enterprise License and Support, 1 Day
Dodání 3-5 dní

Cudy AC1200 bezdrátový router Fast Ethernet Dvoupásmový (2,4 GHz / 5 GHz) Oranžová Počet sítí pro hosty (5 GHz): 1 Přenosová rychlost sítě Ethernet: 10100 Aktivace portů: Ano Připojení na síť Ethernet
Dodání 3-5 dní

QGD-1600 společnosti QNAP je první spravovaný přepínač na světě, který podporuje virtuální počí...
Dodání 3-5 dní
ASUS TUF-BE3600 wireless router Gigabit Ethernet Dual-band (2.4 GHz / 5 GHz) Black
Ano, centrál. sklad
Přepněte Netgear M4250-40G8XF-POE+ (GSM4248PX-100EUS)
Skladem, dodání 2-4 dní
ETHERNET PORT CONFIGURATION 8 Gigabit ports PLUG-AND-PLAY Simple set up with no software to install or configuration needed and zero maintenance FULL PERFORMANCE Non-blocking switching architecture for maximum throughput at wire speed PHYSICAL SPE
Ano, centrál. sklad

Cisco switch CBS220-48T-4X - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Řada Cisco Business 220 jsou jednoduché a cenově dostupné chytré switche pro sítě podnikové třídy. Díky podpoře mobilních aplikací, nástroji Cisco Business Dashboard a několika možnostem PoE+ poskytuje CBS220 robustní síť v rámci omezeného rozpočtu. Stránky produktu: CBS220-48T-4X Quick start guide: Quick start guide Switching capacity Forwarding rate in millions of packets per second (mpps; 64-byte packets) 130,94 Switching capacity in Gigabits per second (Gbps) 176 Layer 2 switching MAC table Up to 8,192 Media Access Control (MAC) addresses Spanning Tree Protocol (STP) Standard 802.1d Spanning Tree support, enabled by default Fast convergence using 802.1w (Rapid Spanning Tree [RSTP]) Multiple Spanning Tree instances using 802.1s (MSTP) 16 instances are supported Port grouping Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation Load balance based on source and destination MAC address, or source and destination MAC/IP VLAN Support for up to 256 Virtual Local Area Networks (VLANs) simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Auto voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS QinQ VLAN VLANs transparently cross a service provider network while isolating traffic among customers Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Protocols for automatically propagating and configuring VLANs in a bridged domain Head-of-Line (HOL) blocking HOL blocking prevention Jumbo frame Frame sizes up to 9,216 supported Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP. Automatic Media-Dependent Interface Crossover (MDIX) Automatically adjusts transmit and receive pairs if an incorrect cable type (crossover or straight-through) is installed. Security ACLs Drop or rate limit based on source and destination MAC, VLAN ID or IP address, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, Transmission Control Protocol (TCP)/ User Datagram Protocol (UDP) source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, Internet Group Management Protocol (IGMP) packets, TCP flag Support up to 512 rules Port security Creates the ability to lock source MAC addresses to ports; limits the number of learned MAC addresses IEEE 802.1X (authenticator role) 802.1X: Remote Authentication Dial-in User Service (RADIUS) authentication; guest VLAN; Single-host, multiple-host, and multisession mode RADIUS, TACACS+ Supports RADIUS and Terminal Access Controller Access Control System (TACACS) authentication; switch functions as a client MAC address filtering Supported Storm control Broadcast, multicast, and unknown unicast DoS protection DOS attack prevention STP Bridge Protocol Data Unit (BPDU) Guard This security mechanism protects the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. Spanning Tree Loop Guard This feature provides additional protection against Layer 2 forwarding loops (STP loops). Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. SCP also uses SSH. SSH v1 and v2 are supported. Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch QoS Priority levels 8 hardware queues per port Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and class of service (802.1p/CoS) Class of service Port-based; 802.1p VLAN priority-based; IPv4/v6 IP precedence, Type of Service (ToS), and DSCP-based; Differentiated Services (DiffServ); classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer; egress shaping and rate control; per VLAN, per port, and flow-based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization. Multicast Internet Group Management Protocol (IGMP) Versions 1, 2, and 3 Snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; supports 256 multicast groups IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad LACP, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.1D (STP, GARP, and GVRP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, Request for Comments (RFC) 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 922, RFC 920, RFC 950, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1350, RFC 1533, RFC 1541, RFC 1624, RFC 1700, RFC 1867, RFC 2030, RFC 2616, RFC 2131, RFC 2132, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 2576, RFC 4330, RFC 1213, RFC 1215, RFC 1286, RFC 1442, RFC 1451, RFC 1493, RFC 1573, RFC 1643, RFC 1757, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2233, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 1157, RFC 1493, RFC 1215, RFC 3416 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet IPv6/IPv4 Dual Stack IPv6 neighbor and router discovery (ND) IPv6 stateless address auto-configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) ICMP version 6 IPv6 ACL Drop or rate limit IPv6 packets in hardware IPv6 QoS Prioritize IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) Snooping Deliver IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, DHCP Client, DHCP Autoconfig, Cisco Discovery Protocol (CDP), Link Layer Discovery Protocol (LLDP) IPv6 Requests for Comments (RFCs) supported RFC 4443 (which obsoletes RFC2463) - ICMP version 6 RFC 4291 (which obsoletes RFC 3513) - IPv6 address architecture RFC 4291 - IPv6 addressing architecture RFC 2460 - IPv6 specification RFC 4861 (which obsoletes RFC 2461) - Neighbor discovery for IPv6 RFC 4862 (which obsoletes RFC 2462) - IPv6 stateless address auto-configuration RFC 1981 - Path MTU discovery RFC 4007 - IPv6 scoped address architecture RFC 3484 - Default address selection mechanism Management Cisco Business Dashboard Support direct management with Cisco Business Dashboard and mobile app. Eliminates the need to set up a separate hardware or virtual machine for the Cisco Business Dashboard Probe on site. Cisco Business mobile app Mobile app for Cisco Business Switch and Wireless products. Helps to set up a local network in minutes and provide easy management at your fingertips. Cisco Network Plug and Play (PnP) agent The Cisco Network Plug and Play solution provides a simple, secure, unified, and integrated offering to ease new branch or campus device rollouts or for provisioning updates to an existing network. The solution provides a unified approach to provision Cisco routers, switch
Skladem v eshopu
UBNT UniFi Switch USW-48 USW-48 je plně managovatelný switch se 48x 1Gbps ethernet porty a 4x 1Gbps SFP porty. Switch má ve výbavě bohatou škálu L2 funkcí, navíc je zcela tichý - bez ventilátorů. Díky apliaci UniFi Network Controller a mobilní aplikaci UniFi Network můžete switch konfigurovat a spravovat všechny funkce za pomoci intuitivního grafického rozhraní odkudkoliv. Vlastnosti a funkce: 48x 1Gbps ethernet 4x 1Gbps SFP port L2 funkce Fanless 1.3" dotykový displej, podpora UniFi Network AR Správa pomocí UniFi Network Controller (5.3.10+) Obsah balení Zařízení Napájecí kabel (2) Úchyty do 19" racku Technické specifikace: Konektory a rozhraní Rychlost LAN: (48) 10/100/1000Mbps Optické rozhraní: (4) 1000Mbps Ostatní: Dotykový displej Napájení Typ napájení: Ze sítě (230V) Max. spotřeba energie [W]: 40 Napájení přes konektor/svorkovnici: 230V AC Fyzické charakteristiky Provedení: Rackmount Ventilátory: Bez ventilátoru Šasi: Kovové Tlačítka: Reset Provozní teplota [°C]: -15 až 40 Šířka [mm]: 442 Výška [mm]: 44 Hloubka [mm]: 285 Obecné Rychlost přepínání [Gbps]: 52 Rychlost předávání paketů [Mpps]: 77,4 Software Management: UniFi controller, CLI Funkce: VLAN, QoS, DHCP snooping Výchozí IP adresa: Dynamická z DHCP Výchozí jméno a heslo: ubnt / ubnt Užitečné odkazy: stránky výrobce UBNT.com aktuální verze airOS datasheety, uživatelské příručky výpočet parametrů bezdrátového spoje - AirLink návody pro začátečníky - BeansTalk video-návody (ubnt youtube channel) Ubiquiti Wiki Ubiquiti oficiální fórum
Skladem v eshopu
Teltonika INDUSTRIAL WIRED ROUTER - RUTM08
Dodání 3-5 dní

Hikvision DS-3E0503DP-E/R Nespravovaný switch Nespravovaný Gigabit Ethernet (10/100/1000) Podpora PoE Bílá Výrobce: Hikvision Kategorie:
Dodání 3-5 dní
MERCUSYS switch MS110CMP 8portový 10/100 Mb/s + 2portový gigabitový stolní přepínač s 8 porty PoE+ 8× 10/100 Mb/s PoE+ portů + 2× gigabitové porty bez PoE 8 portů PoE+ umožňuje přenos dat a napájení po jediném kabelu. Podpora výkonu PoE až 30 W pro každý port PoE a 115 W pro všechny porty PoE MS110CMP poskytuje 2× uplink porty při zapnutí režimu izolace. Jeden pro připojení k internetu a jeden pro připojení k NVR Prodloužení přenosové vzdálenosti PoE až na 250 m pomocí režimu Extend Jedním kliknutím rozdělíte provoz pro konkrétní porty, abyste zajistili stabilitu a bezpečnost. Pracuje s PD kompatibilními se standardem IEEE 802.3af/at Jednoduché použití a úspora času a námahy. Automaticky restartuje vypadlá nebo nereagující zařízení s napájením PoE. Umožňuje účinný odvod tepla a dlouhou životnost sítě. Stránky produktu: https://www.mercusys.com/cz/product/details/ms110cmp Technické specifikace Hardware Dimensions (W X D X H) 171*98*27 mm PoE Ports RJ45 Standard: Compliant with 802.3 af/at Powered Devices PoE Ports: Port 1- 8 PoE Power Budget: 115 W Interfaces 8× 10/100 Mbps Ports + 2× Gigabit Ports, Auto-Negotiation AUTO MDI/MDIX External Power Supply External Power Adapter (Output: 53.5V/2.2A) Installation Desktop / Wall Mount Standards and Protocols IEEE 802.3x Flow Control Data Rates 10/100 Mbps at Half Duplex 20/200 Mbps at Full Duplex Jumbo Frame 2 KB Mac Address Table 2K Max Power Consumption • 3.79 W (220V / 50Hz with no PD connected) • 130.49 W (220V / 50Hz with 111 W PD connected) Max Heat Dissipation • 12.92 BTU/h (220V / 50Hz with no PD connected) • 444.97 BTU/h (220V / 50Hz with 111 W PD connected) Others Package Contents 10-Port 10/100Mbps Desktop Switch with 8-Port PoE+ (MS110CMP) Power Adapter Quick Installation Guide Environment Operating Temperature: 0?~40? (32?~104?) Storage Temperature: -40?~70? (-40?~158?) Operating Humidity: 10%~90% RH non-condensing Storage Humidity: 5%~95% RH non-condensing
Ano, centrál. sklad

Na popisu produktu pracujeme a doplníme jej v nejbližší možné době. Produkt je možné zakoupit.
Dodání 3-5 dní
ZTE MF920C zařízení pro mibilní síť Router Kapacita baterie: 2000 mAh Typ zdroje: Baterie Barva: Bílá LED indikátory: Ano Vestavěný displej: Ano Typ zařízení: Router Hmotnost: 102 g Výška: 64,8 mm Hlo
Dodání 3 dny

NETGEAR 16-Port GB PoE+ unmanaged Switch 183W FlexPoE
Ano, centrál. sklad
Přepínač Instant On 1830 Řada přepínačů Aruba Instant On 1830 nabízí snadno použitelné a cenově dostupné kabelové řešení pro sítě podporující IT, mobilní a cloudové aplikace. Tato cenově dostupná a snadno nasaditelná řada inteligentních spravovaných přepínačů je ideální pro firmy hledající cenově d
Dodání 3 dny

Řada Tellur Smart Home je navržena pro lepší a chytřejší bydlení. Pomocí WiFi vypínače můžete ovládat světla ve vaší domácnosti odkudkoli přes internet, takže se nebudete muset bát, že zapomenete zhasnout světla. Dlouhé pracovní dny? Nechcete nechat svého mazlíčka toulat se ve tmě? Snadno peasy! Př
Dodání 3-5 dní
Cisco EOS Meraki MX80 Enterprise License and Support, 1 Day These products have reached end of ...
Dodání 3-5 dní

Switch Hikvision DS-3E0310P-E/M(B) Auto MDI/MDI-X: Ano Spotřeba energie (v klidu): 5 W Vstupní proud: 1.6 A Stejnosměrné vstupní napětí: 54 V Maximální spotřeba energie: 86 W Osvědčení o udržitelnosti
Dodání 3 dny

Cisco switch CBS250-24FP-4G - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Řada Cisco Business 250 představuje novou generaci cenově dostupných inteligentních switchů, které kombinují vysoký síťový výkon, zabezpečení a spolehlivost s komplexní sadou síťových funkcí potřebných pro spolehlivou síť malých firem. Záruka platná do End of Support 31. 10. 2029. Oznámení End of Life pro CISCO CBS250 Stránky produktu: CBS250-24FP-4G Quick start guide: Quick start guide Switching capacity (All switches are wire-speed and nonblocking) Forwarding rate in millions of packets per second (mpps; 64-byte packets) 41,66 Switching capacity in Gigabits per second (Gbps) 56 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 4 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG) VLAN Support for up to 255 active VLANs simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Protocols for automatically propagating and configuring VLANs in a bridged domain IGMP (versions 1, 2, and 3) snooping Internet Group Management Protocol (IGMP) limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported) IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router HOL blocking Head-of-Line (HOL) blocking prevention Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP. Layer 3 routing IPv4 routing Wire-speed routing of IPv4 packets Up to 32 static routes and up to 16 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets Security Secure Sockets Layer (SSL) SSL encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported. IEEE 802.1X (authenticator role) Remote Authentication Dial-In User Service (RADIUS) authentication, guest VLAN, single/multiple host mode, and single/multiple sessions STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices, and secure autoconfig. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC]) Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses RADIUS Supports RADIUS authentication for management access. Switch functions as a client. Storm control Broadcast, multicast, and unknown unicast DoS prevention Denial-of-Service (DoS) attack prevention Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels Access Control Lists (ACLs) Support for up to 512 rules Drop or rate limit based on source and destination MAC, VLAN ID or IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides Time-based ACLs supported QoS Priority levels 8 hardware queues Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and class of service (802.1p/CoS) Class of service Port based; 802.1p VLAN priority based; IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based; Differentiated Services (DiffServ); classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer; egress shaping and rate control; per VLAN, per port, and flow based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.3 ad LACP, IEEE 802.1D (STP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, RFC 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 920, RFC 922, RFC 950, RFC 951, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1213, RFC 1215, RFC 1286, RFC 1350, RFC 1442, RFC 1451, RFC 1493, RFC 1533, RFC 1541, RFC 1542, RFC 1573, RFC 1624, RFC 1643, RFC 1700, RFC 1757, RFC 1867, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2030, RFC 2131, RFC 2132, RFC 2233, RFC 2576, RFC 2616, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 3416, RFC 4330 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet IPv6/IPv4 Dual Stack IPv6 Neighbor Discovery (ND) IPv6 stateless address auto configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) Internet Control Message Protocol (ICMP) version 6 IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) support USGv6 and IPv6 Gold Logo certified IPv6 QoS Prioritize IPv6 packets in hardware IPv6 ACL Drop or rate limit IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) snooping Deliver IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, Ping, Traceroute, Simple Network Time Protocol (SNTP), Trivial File Transfer Protocol (TFTP), Simple Network Management Protocol (SNMP), Remote Authentication D
Ano, centrál. sklad
Aktivní kabel Lindy 41078 s rozhraním DisplayPort 1.2 kombinuje elegantní a moderní design s vysokým výkonem, což umožňuje vysoce kvalitní a spolehlivý přenos signálu DisplayPort na velké vzdálenosti. Aktivní čipová sada v malém pouzdře uprostřed kabelu zesiluje signály DisplayPort a umožňuje tak p
3-5 dní dostupné

Ruijie Networks RG-EG105GW(T) bezdrátový router Gigabit Ethernet Dvoupásmový (2,4 GHz / 5 GHz) Černá Podpora kontroly toku: Ano Typ rozhraní ethernetu LAN: Gigabit Ethernet Statické směrování: Ano Tec
Dodání 3-5 dní

Incorporating the latest Multi-Stream Transport (MST) technology, the CS1924M 4-Port USB 3.0 4K DisplayPort MST KVMP™ Switch is the world’s first DisplayPort KVM switch with a built-in MST hub. The CS1924M enables users to adopt two console displays fro
Dodání 3-5 dní

Esperanza ENS108 10portový PoE switch s 8xPoE a 2xUplink – perfektní řešení pro IP dohled. Přepínač Esperanza ENS108 je moderní zařízení, které kombinuje funkčnost a vysoký výkon, což z něj činí vynikající volbu pro IP dohledové systémy. S 10 porty, včetně 8 PoE portů, tento přepínač nejen umožňuje
Dodání 3 dny

Přístupový bod pro montáž na stěnu či strop, Wi-Fi 6, rychlost přenosu dat 574 / 4804 MB/s (2,4 / 5GHz pásmo), MU-MIMO, Beamforming, RangeBoost, QAM-1024, Kaptivní portál, Seamless Roaming, Omada Mesh, Airtime Fairness, PoE napájení. ABS plast. Bílá.
Skladem v eshopu
Teltonika INDUSTRIAL 4G LTE ROUTER - RUTM11
Dodání 3-5 dní

BCS B-SP0802G Základní přepínač BCS 8x PoE, 2x RJ45 Gigabit Výrobce: BCS Kategorie:
Dodání 3-5 dní
Xiaomi Router AX3000T Xiaomi Router AX3000T vybavený 4 externími anténami, které poskytují silné a stabilní pokrytí. Wi-Fi 6 umožňuje bezdrátové síti pracovat rychlostí 3000 Mb/s, což zaručuje, že budete moci sledovat 4K videa bez ukládání do vyrovnávací paměti. Bezdrátové rychlosti 3000 Mb/s Pásma
Skladem, dodání 2-4 dní
Stolní přepínač HDMI KVM Ovládání 2 počítačů pomocí kombinace klávesnice a myši USB - přepínání mezi dvěma počítači stisknutím tlačítka Použití jednoho monitoru, myši a klávesnice k ovládání dv
Dodání 3 dny

Typ: Switch Počet Gigabit-Portů: 8 Uplink-Port: 2 PoE (Power over Ethernet): ano Šířka (mm): 220 Výška (mm): 161 Barva: černá Hloubka (mm): 44 Hmotnost (g): 1180 IEEE 802.3x Flow Control (Full-Duplex Flow Control): ano IEEE 802.3 10-BASE-T, Ethernet: ano IEEE 802.3ab 1000-BASE-T, Gigabit Ethernet: ano IEEE 802.3af Power Over Ethernet (PoE): ano IEEE 802.3u 100-BASE-TX, Fast Ethernet: ano IEEE 802.3at Power over Ethernet Plus (PoE+): ano
Skladem, dodání 2-4 dní

Ušetříte náklady na instalaci a čas díky PoE 16-portový gigabitový Ethernet PoE+ je Intellinet Switch (č. výr. 560993) je vynikající řešení pro přenos dat a napájení na.
Dodání 3-5 dní

PLANET LS100-DW-868M; Dveřní a okenní senzor nabízí elegantní řešení pro monitorování vchodů do budov v reálném čase . Prostřednictvím připojení LoRaWAN poskytuje tento snímač aktualizace stavu dveří a ok...
Ano, centrál. sklad
Planet ISW-511T, 4x 10/100Base-TX+ 1x 100FX 2km, MM, DIN, IP30, -40~75°C Přepínače pro průmyslový Ethernet jsou určeny do náročných provozních podmínek s velkým rozsahem pracovních teplot, nejistým napájením a častými otřesy. Přepínače řady ISW se snadno instalují na standardní DIN lištu nebo přímo na zeď a umožňují nasazení dobře známé Ethernetové technologie i v průmyslovém prostředí. Stejně tak jsou vhodné pro instalace do venkovně umístěných skříní s velkým kolísáním pracovních teplot (typicky bezdrátové a MAN ISP aplikace). Vlastnosti: - 4 porty 100Base-TX, Switching, Full Duplex (100/200 Mbps), Auto-Negotiation (10/100 Mbps), automatická detekce přímý/křížený kabel na každém portu - 1 port 100Base-FX, full duplex, SC konektory, multimodemode, pro 50/125um a 62,5/125um vlákno, dosah 2km, vlnová délka 1300nm, zdvih min. 15,5dB (vysílací výkon max. -14dBm, min. -19dBm, přijímací citlivost -34,5dBm) - 1M buffer, propustnost sběrnice 1Gbps, 0,74Mpps (64B), tabulka 2k MAC adres - pole LED indikátorů pro diagnostiku provozu - instalace na DIN lištu, montážní díl součástí - instalace na zeď, montážní díl součástí - krytí IP30, skříň celohliníková - napájení: 12-48V DC redundantní, připojení možné ze dvou různých zdrojů (nejsou součástí balení) - ochrana proti přepólování, připojení napájení na svorkovnici, umístění na spodním panelu (nepřekáží při montáži na zeď) - QoS prioritizace provozu dle portu, ToS, 802.1p - zařízení je odolné proti pádu (IEC-60068-2-32) z výšky 75cm na všechny dopadové části - zařízení je odolné proti vibracím (IEC-60068-2-6) 10-500-10Hz, 4x g, 0,5oct/min - zařízení je odolné proti přetížení krátkodobému zrychlení 50g, dlouhodobému 4g, (IEC-60068-2-27) - EMI/EMS, elektromagnetická kompatibilita a slučitelnost dle CE EN-6100-4-2,3,4,5,6 - elektrická bezpečnost dle CE EN-60950 - pracovní teplota -40 až 75°C, vlhkost do 95% - příkon do 14W - rozměry: 135 x 97 x 32 mm - hmotnost: 436g
Dodání 3-5 dní
Přepněte Netgear M4250-10G2F (GSM4212P-100EUS)
Skladem, dodání 2-4 dní
Zenwire 10portový rozbočovač/přepínač, 8 POE, 2 LAN, Ethernet, RJ45 pro IP kamery 1028 Výrobce: Zenwire Kategorie:
Skladem, dodání 2-4 dní
SWITCH LANBERG RSFE-24P-2C-360 24X 100MB POE+/2X COMBO RACK 19" GIGABIT ETHERNET 360W PRO
Dodání 3 dny