

LTE modem Cat7, 300/100 Mb/s, 9 dBi, 2× SIM, 2× LAN PoE, venkovní, -40 až +60 °C.
Skladem v eshopu

Cudy GS1010PE síťový přepínač Gigabit Ethernet (10/100/1000) Podpora napájení po Ethernetu (PoE) Černá Přenosová rychlost sítě Ethernet: 10,100,1000 Mbit/s Podpora VLAN: Ano Síťové standardy: IEEE 802
Skladem, dodání 2-4 dní

Pouzdro pro Nintendo Switch (kompatibilní i se Switch Lite/OLED) + příslušenství, lze přenášet i konzoli s připojenými HORI Split Pad Compact ovladači, motiv Pokémona Eevee
Skladem, dodání 2-4 dní

Objevte plný potenciál vaší sítě. Objevte spolehlivé a efektivní síťové zařízení typu plug-and-play. Díky 16 portům RJ45 10/100/1000 Mbps s PoE a dalším 2 SFP portům (optické vlákno 1000 Mbps) vám zařízení umožňuje vytvořit flexibilní a škálovatelnou LAN síť bez zbytečných napájecích kabelů, extern
Skladem, dodání 2-4 dní
HiLook NS-0505D; Gigabitový 5portový switch bez správy (unmanaged). Nabízí kapacitu 10 Gbps , snadnou instalaci (Plug-and-Play) a odolné kovové tělo. Je vhodný pro domácnosti, školy, ubytovny, kanceláře, malé monitorovací zařízení a další jednoduchá s...
Ano, centrál. sklad

PLANET FSD-604HP; 6portový PoE přepínač 10/100Base-TX, včetně 4x Power over Ethernet injektorů (napáječů) standardu IEEE 802.3at, celkový výkon až 60 W. Extend mód pro spojení rychlostí 10 Mb/s do vzdálenosti až...
Ano, centrál. sklad
Teltonika RUTM20 Průmyslový 5G router s globálním pokrytím pro náročné IoT a IIoT aplikace. RUTM20 je ultra-kompaktní průmyslový 5G router navržený pro IoT a IIoT řešení, kde záleží na velikosti a nákladech. Využívá globální Telit 5G modem podporující
Ano, centrál. sklad
Dvoupásmový Wi-Fi router, standard Wi-Fi 7, rychlost až 4,3 Gbps v pásmu 5 GHz a 688 Mbps v pásmu 2,4 GHz. Zabezpečení WPA3, 1x 2.5G LAN s podporou napájení PoE.
Ano, centrál. sklad

NoName Přepínač PŘEPÍNAČ POE / ROZŠÍŘOVAČ PFT1320 3PORTOVÝ Výrobce:
Skladem, dodání 2-4 dní
TP-Link TL-SG105MPE Gigabitový Easy Smart Switch s 4-Port PoE+ 5 portů 10/100/1 000 Mbit/s RJ45 Je vybaven čtyřmi porty 802.3af/at PoE+ s výkonem až 30 W pro každý port, data a napájení lze přenášet jediným kabelem Podporuje napájení PoE s celkovým výkonem až 120 W ze všech portů PoE Poskytuje monitorování sítě, řízení provozu podle priorit, funkce VLAN a automatické obnovení PoE Jednoduché nastavení sítě a připojení „Plug and Play“ Webové uživatelské rozhraní a konfigurační nástroj Easy Smart zjednodušují nastavení Konstrukce bez ventilátoru snižuje spotřebu energie a eliminuje provozní hlučnost Více informací o technologii TP-LINK PoE > Stránky produktu: https://www.tp-link.com/cz/business-networking/poe-switch/tl-sg105mpe/ Technické specifikace HARDWARE FEATURES Standards and Protocols IEEE 802.3i, IEEE 802.3u, IEEE 802.3ab, IEEE 802.3af, IEEE 802.3x, IEEE 802.1q, IEEE 802.1p, IEEE 802.3at Interface Five 10/100/1000Mbps RJ45 Ports AUTO Negotiation/AUTO MDI/MDIX Network Media 10BASE-T: UTP category 3, 4, 5 cable (maximum 100m) EIA/TIA-568 100? STP (maximum 100m) 100BASE-TX: UTP category 5, 5e cable (maximum 100m) EIA/TIA-568 100? STP (maximum 100m) 1000BASE-T: UTP category 5, 5e, 6 or above cable (maximum 100m) EIA/TIA-568 100? STP (maximum 100m) Fan Quantity Fanless Power Supply External Power Adapter (Output: 53.5 VDC / 2.43 A) PoE Ports (RJ45) Standard: 802.3 af/at compliant PoE Ports: Port 1- Port 4 PoE Power Budget: 120 W Dimensions ( W x D x H ) 3.9 × 3.9 × 1.0 in (99.8 × 98 × 25 mm) Max Power Consumption 4.34 W (220 V/50 Hz with no PD connected) 137.01 W (110 V/50 Hz with 120 W PD connected) Max Heat Dissipation 14.8 BTU/h (with no PD connected) 467.17 BTU/h (with 120 W PD connected) PERFORMANCE Switching Capacity 10 Gbps Packet Forwarding Rate 7.44 Mpps MAC Address Table 2 K Packet Buffer Memory 1 Mb Jumbo Frame 16 KB SOFTWARE FEATURES Quality of Service Support Port-Based/802.1p/DSCP priority Support 4 priority queues Rate Limit Storm Control L2 Features IGMP Snooping V1/V2/V3 Static Link Aggregation Port Mirroring Cable Diagnostics Loop Prevention PoE Auto Recovery Extend Mode VLAN Supports up to 32 VLANs simultaneously (out of 4K VLAN IDs) MTU/Port/Tag VLAN Management Web-based GUI Easy Smart Configuration Utility Transmission Method Store-And-Forward OTHERS Certification FCC, CE, RoHS Package Contents TL-SG105MPE Power Adapter Installation Guide Rubber Feet System Requirements Microsoft Windows for running Utility Environment Operating Temperature: 0°C~40°C (32°F~104°F) Storage Temperature: -40°C~70°C (-40°F~158°F) Operating Humidity: 10%~90%RH non-condensing Storage Humidity: 5%~95%RH non-condensing
Skladem v eshopu
Wi-Fi router s dvoupásmovým připojením, 5 GHz - rychlost 2 880 Mbps, 2,4 GHz - rychlost 688 Mbps, 4 všesměrové antény, 1x 1Gbps WAN port, 3x 1Gbps LAN port, technologie EasyMesh.
Skladem v eshopu

48portový gigabitový L2 řízený switch JetStream se 4 SFP sloty T2600G-52TS (TL-SG3452) Gigabitová ethernetová připojení na všech portech poskytují vysokou rychlost.
Skladem v eshopu
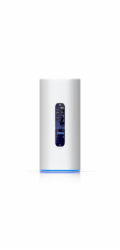
Pokročilý UniFi router s integrovaným 5G modemem, WiFi 7 tri-band, 10G SFP+ portem a plnou podporou UniFi OS aplikací. Ideální pro vzdálené pobočky a flexibilní nasazení s 5G konektivitou až 3,4 Gb/s.
Skladem, dodání 2-4 dní
Cisco Catalyst switch C1300-24XT - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu. Stránky produktu: C1300-24XT Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 357.14 Switching capacity in gigabits per second (Gbps) 480 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4093 VLANs simultaneously Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN Auto surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported) IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wire-speed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Stacking Hardware stacking Up to 8 switches in a stack. Up to 200 ports managed as a single system with hardware failover Stacking is supported on the following models: Family 1: C1300-16P-4X, C1300-24T-4X, C1300-24P-4X, C1300-24FP-4X, C1300-48T-4X, C1300-48P-4X, C1300-48FP-4X, C1300-8MGP-2X, C1300-24MGP-4X, C1300-48MGP-4X Family 2: C1300-12XT-2X, C1300-12XS, C1300-16XTS, C1300-24XS, C1300-24XT, C1300-24XTS PIDs from the same Family can be stacked together. Cross-stacking between Families is not supported. High availability Fast stack failover delivers minimal traffic loss. Support for LAG across multiple units in a stack Plug-and-play stacking configuration/management Active/standby for resilient stack control Auto-numbering Hot swap of units in stack Ring and chain stacking options, auto stacking port speed, flexible stacking port options High-speed stack interconnects Cost-effective high-speed 10 Gigabit Ethernet fiber interfaces Security Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through a web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard Prevents edge devices not in
Ano, centrál. sklad
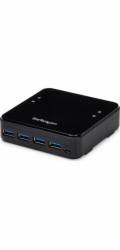
StarTech USB HUB 4x USB-B + 4x USB-A 3.0 (HBS304A24A)
Dodání 3-5 dní

Přístupový bod Camsat Přístupový bod LTE Kat. 4 GLOBALCAM 4.5G-2POE 2.4GHz, 150Mb/s CAMSAT
Dodání 3-5 dní

Acer Connect Ovia T360 WiFi 7 Dual-band Mesh Router Part Number: FF.G38TA.007 Parametry Model: BE3600 Wifi: 802.11 a/b/g/n/ac/ax/be 2x2 MIMO, Dual band 2.4GHz + 5GHz Rozhraní: MLO, 1x WAN 1GbE, 2x LAN 1GbE Procesor: 2.0 GHz Quad-Core ARM Processor Paměť: RAM 512MB DDR3L Storage: 128MB NAND Výbava: Acer Connect App, FOTA software update, WPS button, Pin Hole reset, 4 interní antény, Passive Cooling Bezpečnost: pokročilé šifrování, VPN, firewall, rodičovská kontrola Adaptér: 12 V / 1 A Ethernet kabel: Ano Fyzické parametry: o110x155 mm, 360 g Balení: 3 pack
Skladem, dodání 2-4 dní
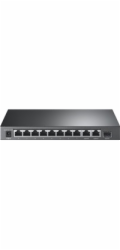
TP-Link TL-SL1311P Desktop switch s 8 porty 100Mb/s, 3 GbE porty a 8 porty PoE+ 8 portů RJ45 10/100 Mbit/s, 2 gigabitové porty RJ45 a 1 gigabitový port SFP. 8 portů PoE+ přenáší data a napájení v jednotlivých kabelech. Podporuje zařízení PD v souladu se standardem IEEE 802.3af/at. Podporuje napájení PoE s celkovým výkonem až 30 W z každého portu PoE. Podporuje napájení PoE s celkovým výkonem až 65 W ze všech 8 portů PoE. Přenos dat a napájení na vzdálenost až 250m v rozšířeném režimu. Režim izolace umožňuje jedním kliknutím oddělit přenos dat klientů k zajištění vyššího zabezpečení a výkonu. Automatické obnovení PoE zaručuje spolehlivý provoz zařízení PoE díky automatickému restartování vypadlých nebo nereagujících napájených zařízení. Konstrukce bez ventilátoru snižuje spotřebu energie a zajišťuje tichý provoz v místě instalace. Zapojení „Plug and Play“ bez nutnosti konfigurace. Více informací o technologii TP-Link PoE > Stránky produktu: https://www.tp-link.com/cz/business-networking/poe-switch/tl-sl1311p/ Technické specifikace HARDWARE FEATURES Interface • 8× 10/100 Mbps 802.3af/at PoE+ Ports, 2× Gigabit RJ45 Ports, 1× Gigabit SFP Port • AUTO Negotiation • AUTO MDI/MDIX Network Media • 10BASE-T: UTP category 3, 4, 5 cable (maximum 100m) • EIA/TIA-568 100? STP (maximum 100m) • 100BASE-TX: UTP category 5, 5e cable (maximum 100m) • EIA/TIA-568 100? STP (maximum 100m) Fan Quantity Fanless Physical Security Lock Yes External Power Supply External Power Adapter (Output: 53.5 VDC / 1.31 A) Packet Forwarding Rate 5.6544 Mpps PoE Ports (RJ45) • Standard: 802.3 af/at compliant • PoE Ports: Ports 1–8 • Power Supply: 65 W Mac Address Table 2K Jumbo Frame 16 KB Switching Capacity 7.6 Gbps Dimensions ( W x D x H ) 8.2 × 4.9 × 1.0 in (209 × 126 × 26 mm) Max Power Consumption • 5.61 W (220 V/50 Hz. no PD connected) • 77.32 W (110 V/50 Hz. with 65 W PD connected) Max Heat Dissipation • 19.13 BTU/h (no PD connected) • 263.7 BTU/h (with 65 W PD connected) SOFTWARE FEATURES Transmission Method Store-And-Forward Advanced Functions • Compatible With IEEE 802.3af/at Compliant PDs • Extend Mode Button (Ports 1–4 and Ports 1–8, Up to 250 m PoE power supply and data transmission) • Isolation Mode Button (Ports 1–8) • PoE Auto Recovery Button (Ports 1–8) • Mac Address Auto-Learning and Auto-Aging • IEEE802.3x Flow Control For Full-Duplex Mode And Backpressure for Half-Duplex Mode OTHERS Certification FCC, CE, RoHS Package Contents • TL-SL1311P • Power Adapter • Installation Guide Environment • Operating Temperature: 0–40°C (32–104°F) • Storage Temperature: -40–70°C (-40–158°F) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% RH non-condensing
Skladem v eshopu
Router, 1x 10G WAN, 1x 2.5G LAN, Tri-band WiFi 7, IDS/IPS, VPN, UniFi Network, USB-C napájení.
Skladem v eshopu

R11e-LoRa8 je nová karta koncentrátoru LoRaWAN ve verzi mini PCIe ve formě čipové sady Semtech SX1301. Umožňuje připojení LoRaWAN pro jakýkoli produkt MikroTik, který má slot mPCIe s připojenými USB linkami.
Skladem v eshopu

Switch HP Aruba Instant na 1960 12xgt (JL805A)
Skladem, dodání 2-4 dní
Wi-Fi extender, třípásmové připojení s rychlostí až 10,8 Gb/s (5 760 Mb/s v pásmu 6 GHz, 4 230 Mb/s v pásmu 5 GHz a 688 v pásmu 2,4 GHz), 4 antény s vysokým ziskem, kompatibilní s EasyMesh.
Skladem v eshopu

Cisco switch CBS250-24FP-4X - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Řada Cisco Business 250 představuje novou generaci cenově dostupných inteligentních switchů, které kombinují vysoký síťový výkon, zabezpečení a spolehlivost s komplexní sadou síťových funkcí potřebných pro spolehlivou síť malých firem. Záruka platná do End of Support 31. 10. 2029. Oznámení End of Life pro CISCO CBS250 Stránky produktu: CBS250-24FP-4X Quick start guide: Quick start guide Switching capacity (All switches are wire-speed and nonblocking) Forwarding rate in millions of packets per second (mpps; 64-byte packets) 95,23 Switching capacity in Gigabits per second (Gbps) 128 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 4 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG) VLAN Support for up to 255 active VLANs simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Protocols for automatically propagating and configuring VLANs in a bridged domain IGMP (versions 1, 2, and 3) snooping Internet Group Management Protocol (IGMP) limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported) IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router HOL blocking Head-of-Line (HOL) blocking prevention Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP. Layer 3 routing IPv4 routing Wire-speed routing of IPv4 packets Up to 32 static routes and up to 16 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets Security Secure Sockets Layer (SSL) SSL encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported. IEEE 802.1X (authenticator role) Remote Authentication Dial-In User Service (RADIUS) authentication, guest VLAN, single/multiple host mode, and single/multiple sessions STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices, and secure autoconfig. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC]) Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses RADIUS Supports RADIUS authentication for management access. Switch functions as a client. Storm control Broadcast, multicast, and unknown unicast DoS prevention Denial-of-Service (DoS) attack prevention Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels Access Control Lists (ACLs) Support for up to 512 rules Drop or rate limit based on source and destination MAC, VLAN ID or IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides Time-based ACLs supported QoS Priority levels 8 hardware queues Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and class of service (802.1p/CoS) Class of service Port based; 802.1p VLAN priority based; IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based; Differentiated Services (DiffServ); classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer; egress shaping and rate control; per VLAN, per port, and flow based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.3 ad LACP, IEEE 802.1D (STP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, RFC 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 920, RFC 922, RFC 950, RFC 951, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1213, RFC 1215, RFC 1286, RFC 1350, RFC 1442, RFC 1451, RFC 1493, RFC 1533, RFC 1541, RFC 1542, RFC 1573, RFC 1624, RFC 1643, RFC 1700, RFC 1757, RFC 1867, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2030, RFC 2131, RFC 2132, RFC 2233, RFC 2576, RFC 2616, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 3416, RFC 4330 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet IPv6/IPv4 Dual Stack IPv6 Neighbor Discovery (ND) IPv6 stateless address auto configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) Internet Control Message Protocol (ICMP) version 6 IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) support USGv6 and IPv6 Gold Logo certified IPv6 QoS Prioritize IPv6 packets in hardware IPv6 ACL Drop or rate limit IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) snooping Deliver IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, Ping, Traceroute, Simple Network Time Protocol (SNTP), Trivial File Transfer Protocol (TFTP), Simple Network Management Protocol (SNMP), Remote Authentication
Ano, centrál. sklad

TP-Link JetStream switch TL-SG2016P 16portový gigabitový smart switch JetStream s 8 porty PoE+ 120 W PoE Budget: 8 × 802.3at/af kompatibilních PoE+ portů s celkovým napájením 120 W. Plně gigabitové porty: 8 × gigabitové porty PoE+ a 8× gigabitové porty bez PoE poskytují vysokorychlostní připojení. Integrováno do Omada SDN: Zero-Touch Provisioning, centralizovaná správa cloudu a inteligentní monitorování. Centralizovaná správa: Přístup ke cloudu a aplikace Omada pro maximální pohodlí a snadnou správu. Robustní bezpečnostní strategie: IP-MAC-Port Binding, ACL, Port Security, DoS Defend, Storm control, DHCP Snooping, 802.1X, Radius Authentication a další. Optimalizujte hlasové a video aplikace: L2/L3/L4 QoS a IGMP snooping. Learn more about TP-Link PoE technology > Learn more about Omada Cloud SDN>? Stránky produktu: https://www.tp-link.com/uk/business-networking/omada-sdn-switch/tl-sg2016p/ Technické specifikace HARDWARE FEATURES Standards and Protocols IEEE 802.3i, IEEE 802.3ab, IEEE 802.3ad, IEEE 802.3af, IEEE 802.3at, IEEE 802.3x, IEEE 802.1d, IEEE 802.1s, IEEE 802.1w, IEEE 802.1q, IEEE 802.1p, IEEE 802.1x Interface • 16× 10/100/1000 Mbps RJ45 Ports (Ports 1–8 Support 802.3at/af PoE+) • Auto-Negotiation/Auto MDI/MDIX Network Media • 10BASE-T: UTP category 3, 4, 5 cable (maximum 100m) • 100BASE-TX/1000Base-T: UTP category 5, 5e or above cable (maximum 100m) Fan Quantity Fanless Power Supply • External Power Adapter (Output: 53.5 VDC/ 1.31 A) PoE Ports (RJ45) • Standard: 802.3af/at compliant • PoE Ports: 8 Ports • Power Supply: 120 W* Dimensions ( W x D x H ) 11.3 x 4.4 x 1.0 in (286 x 111.7 x 25.4 mm) Max Power Consumption 146.5 W (110 V/60 Hz) (with 120 W PD connected) Max Heat Dissipation 499.98 BTU/hr (110 V/60 Hz) (with 120 W PD connected) PERFORMANCE Bandwidth/Backplane 16 Gbps MAC Address Table 8k Packet Buffer Memory 4.1 Mbit Jumbo Frame 9 KB SOFTWARE FEATURES Quality of Service • 802.1p CoS/DSCP priority • 8 priority queues • Priority Schedule Mode - SP (Strict Priority) - WRR (Weighted Round Robin) • Queue Weight Config • Bandwidth Control - Port/Flow-based Rating Limit • Smoother Performance • Storm Control - Multiple Control Modes(kbps/ratio) - Broadcast/Multicast/Unknown-Unicast Control L2 and L2+ Features • DHCP Relay - DHCP VLAN Relay • DHCP L2 Relay • Link Aggregation - Static link aggregation - 802.3ad LACP - Up to 8 aggregation groups and up to 8 ports per group • Spanning Tree Protocol - 802.1D STP - 802.1w RSTP - 802.1s MSTP - STP Security: TC Protect, BPDU Filter/Protect, Root Protect • Loopback Detection • Flow Control - 802.3x Flow Control • Mirroring - Port Mirroring - CPU Mirroring - One-to-One - Many-to-One - Flow-Based - Ingress/Egress/Both • Device Link Detect Protocol (DLDP) • 802.1ab LLDP/ LLDP-MED L2 Multicast • 511 IPv4, IPv6 shared multicast groups • IGMP Snooping - IGMP v1/v2/v3 Snooping - Fast Leave - IGMP Snooping Querier - Static Group Config • Multicast VLAN Registration (MVR) • Multicast Filtering • MLD Snooping - MLD v1/v2 Snooping - Fast Leave - MLD Snooping Querier - Static Group Config • Limited IP Multicast (256 profiles and 16 entries per profile) IPv6 Support • IPv6 Dual IPv4/IPv6 • Multicast Listener Discovery (MLD) Snooping • IPv6 neighbor discovery (ND) • Path maximum transmission unit (MTU) discovery • Internet Control Message Protocol (ICMP) version 6 • TCPv6/UDPv6 • IPv6 applications - DHCPv6 Client - Ping6 - Tracert6 - Telnet (v6) - IPv6 SNMP - IPv6 SSH - IPv6 SSL - Http/Https - IPv6 TFTP VLAN • VLAN Group - Max. 4K VLAN Groups • 802.1Q tag VLAN • MAC VLAN: 12 Entries • Protocol VLAN • GVRP • Voice VLAN Access Control List • Support up to 230 entries • Time-Range - Time Slice - Week Time-Range - Absolute Time-Range - Holiday • Time-based ACL • MAC ACL - Source MAC - Destination MAC - VLAN ID - User Priority - Ether Type • IP ACL - Source IP - Destination IP - IP Protocol - TCP Flag - TCP/UDP Source Port - TCP/UDP Destination Port - DSCP/IP TOS • IPv6 ACL • Combined ACL • Rule Operation - Permit/Deny • Policy Action - Mirror - Rate Limit - Redirect - QoS Remark • ACL Rules Binding - Port Binding - VLAN Binding • Actions for flows - Mirror (to supported interface) - Redirect (to supported interface) - Rate Limit - QoS Remark Security • AAA • 802.1X - Port-based authentication - MAC (Host) based authentication - Authentication Method includes PAP/EAP-MD5 - MAB - Guest VLAN - Support Radius authentication and accountability • IP/IPv6-MAC Binding - 512 Binding Entries - DHCP Snooping - DHCPv6 Snooping - ARP Inspection - ND Detection • IP Source Guard - 253 Entries - Source IP+Source MAC • IPv6 Source Guard - 183 Entries - Source IPv6 Address+Source MAC • DoS Defend • Static/Dynamic/Permanent Port Security - Up to 64 MAC addresses per port • Broadcast/Multicast/Unicast Storm Control - kbps/ratio control mode • Port Isolation • Secure web management through HTTPS with SSLv3/TLS 1.2 • Secure Command Line Interface (CLI) management with SSHv1/SSHv2 • IP/Port/MAC-based access control Advanced Features • Automatic Device Discovery • Batch Configuration • Batch Firmware Upgrading • Intelligent Network Monitoring • Abnormal Event Warnings • Unified Configuration • Reboot Schedule MIBs • MIB II (RFC1213) • Bridge MIB (RFC1493) • P/Q-Bridge MIB (RFC2674) • Radius Accounting Client MIB (RFC2620) • Radius Authentication Client MIB (RFC2618) • Remote Ping, Traceroute MIB (RFC2925) • Support TP-Link private MIBs • RMON MIB(RFC1757, rmon 1,2,3,9) MANAGEMENT Omada App Yes, through • Omada Cloud-Based Controller • OC300 • OC200 • Omada Software Controller Centralized Management • Omada Cloud-Based Controller • Omada Hardware Controller (OC300) • Omada Hardware Controller (OC200) • Omada Software Controller Cloud Access Yes, through • Omada Cloud-Based Controller • OC300 • OC200 • Omada Software Controller Zero-Touch Provisioning Yes. Requiring the use of Omada Cloud-Based Controller Management Features • Web-based GUI • Command Line Interface (CLI) through telnet • SNMPv1/v2c/v3 • SNMP Trap/Inform • RMON (1,2,3,9 groups) • SDM Template • DHCP/BOOTP Client • Dual Image, Dual Configuration • CPU Monitoring • Cable Diagnostics • EEE • SNTP • System Log OTHERS Certification CE, FCC, RoHS Package Contents • TL-SG2016P • Power Adapter • Installation Guide • Rubber Feet System Requirements Microsoft Windows 98SE, NT, 2000, XP, Vista™ or Windows 7/8/10/11, MAC OS, NetWare, UNIX or Linux. Environment • Operating Temperature: 0–40 °C (32–104 °F); • Storage Temperature: -40–70 °C (-40–158 °F) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% RH non-condensing
Skladem v eshopu
Průmyslové přepínače jsou základním aktivním zařízením v jakékoli síťové struktuře - od automatizačních systémů a systémů SCADA přes sítě kabelové televize až po distribuované instalace internetu věcí a dohled. Lehká řada průmyslových přepínačů Lanberg by
Ano, centrál. sklad
Plastový držák/krytka kabelů pro zařízení TP-LINK EAP235-Wall EAP615-Wall bílý
Skladem v eshopu
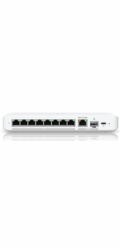
Popis produktu Ubiquiti UniFi Switch Flex 2.5G je kompaktní switch určený pro rozšíření sítě v domácích i kancelářských prostředích. Nabízí 8x 2.5Gbit porty, které umožňují snadnou integraci zařízení s vyššími přenosovými rychlostmi, jako jsou moderní přístupové body, servery nebo NAS úložiště. Switch podporuje správu prostřednictvím aplikace UniFi Network, což usnadňuje jeho konfiguraci a dohled nad sítí. Jako uplink slouží combo port 10G RJ45 / SFP+. Jednou z jeho klíčových funkcí je podpora napájení přes ethernet, což znamená, že zařízení lze napájet přímo přes síťový kabel pomocí PoE vstupu na uplink portu (802.3at / POE+), případně pak pomocí přiloženého USB-C adaptéru. Přestože je uplink port combo, lze nejen využít jen jeden z portů, ale také využít metalický port pro napájení a optický port pro data. Svým minimalistickým designem je ideální pro umístění na pracovním stole nebo montáž na stěnu. S volitelně dokoupeným kitem je možná montáž na DIN lištu. Je plně kompatibilní s produkty UniFi a umožňuje snadné škálování podle potřeby. Pro správu zařízení je potřeba aplikace UniFi Network v9.0.108 a novější. Obsah balení: • Zařízení • Napájecí adaptér USB-C (5V / 3A) • Vrtací šablona • Držák na zeď • Montážní sada Technické parametry Konektory a rozhraní Rychlost LAN:(8) 100/1000/2500 Mbps + (1) 10G RJ45/SFP+ Optické rozhraní:(1) 1/10Gbps Combo Napájení Typ napájení:PoE, USB-C Typy PoE:PoE-In (pouze) Max. spotřeba energie [W]:14 Napájení přes konektor/svorkovnici:5V / 3A Fyzické charakteristiky Provedení:Na zeď, Desktop Ventilátory:Ne Šasi:Plastové Tlačítka:Reset Provozní teplota [°C]:-20 až 45 Šířka [mm]:213 Výška [mm]:34 Hloubka [mm]:76 Obecné Rychlost přepínání [Gbps]:60 Rychlost předávání paketů [Mpps]:44 Software Management:UniFi Network Funkce:L2 Výchozí IP adresa:192.168.1.20, Dynamická z DHCP Výchozí jméno a heslo:ubnt / ubnt
Ano, centrál. sklad
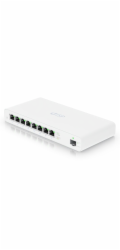
Ubiquiti UISP Router Pro; UISP Router Pro (9× GbE RJ-45 port, 4× 10GbE SFP+ slot) . Může také sloužit jako switch na 2. vrstvě. Router disponuje 1,3" dotykovým displejem, který informuje o stavu a zat...
Ano, centrál. sklad
Huawei S310-48T4X | Přepínač | 48x GE 4x SFP+ AC Omlouváme se, průběžně pracujeme na lepším popisu
Ano, centrál. sklad

Registrace dealerské ceny: https://docs.google.com/forms/d/1sWwsswsbBk36eZx4CJrfl47qUvrORQyYz7kMjrt2f_c/prefill Popis produktu Inteligentní cloudově i přes webové rozhraní spravovatelný smart desktop switch RG-ES205GC od značky Ruijie, nabízí cenově efektivní řešení s 5 Gigabit LAN porty. Tento kompaktní přepínač je ideální pro síťové aplikace, které vyžadují výkon a spolehlivost. Co se výčtu funkcí týče, switch nabízí tichý chod bez ventilátorů, podporu až 16 VLAN, DHCP snooping, testování kabelu a ochranou proti zakruhování. Klíčové vlastnosti • 5× 10/100/1000 Mbps LAN porty • Kvalitní provedení, kovové šasi • Bez venilátoru • Nízká spotřeba - max. 3 W • Správa přes webové rozhraní a cloud • Celoživotní správa na Ruijie Cloud kdykoli a kdekoli • Rozpoznávání IP kamer - jedinečná hodnota pro CCTV síť • Automatická prevence proti zakruhování Obsah balení • Zařízení • Napájecí adaptér 5 V/1 A Technické parametry Konektory a rozhraní Rychlost LAN:(5) 10/100/1000Mbps Napájení Typ napájení:DC konektor Max. spotřeba energie [W]:3 Napájení přes konektor/svorkovnici:5V / 1A Fyzické charakteristiky Provedení:Desktop Ventilátory:Bez ventilátoru Šasi:Kovové Tlačítka:Reset Provozní teplota [°C]:0 až 40 Šířka [mm]:119 Výška [mm]:24 Hloubka [mm]:75 Obecné Rychlost přepínání [Gbps]:10 Tabulka MAC adres:2000 Rychlost předávání paketů [Mpps]:7,4 Software Web management:Ano Management:Webové rozhraní, Ruijie cloud Funkce:VLAN, DHCP snooping Výchozí IP adresa:10.44.77.200 Výchozí jméno a heslo:Nastavuje se při prvním spuštění
Dodání 3-5 dní
Ubiquiti UniFi Wave AP je výkonný Wi-Fi přijímač, který rozšiřuje síťové připojení do odlehlých oblastí. Díky vysoce výkonným anténám a technologii tvarování paprsku nabízí UniFi Wave AP rozšířený dosah a spolehlivost. Integrace s ekosystémem UniFi umožňuje centralizovanou správu a monitorování víc
Ano, centrál. sklad
Popis produktu RB5009UPr+S+OUT je vysoce výkonný router s PoE, který přichází s pasivním chlazením, venkovním šasi s IP66 krytím a vysokým výkonem (o 60 - 90 % vyšší než RB4011) o který se zasluhuje 64bit ARM architektura procesoru s taktem 1400 MHz, 1GB RAM typu DDR4 a 1GB NAND uložiště. Router disponuje 7× Gigabit LAN, 1× 2.5Gbit LAN s možností PoE IN i PoE OUT (802.3af/at) na všech osmi ethernetových portech s celkovým PoE budgetem 130 W, DC svorkovnicí (24 .. 57V DC), 1× SFP+ slot a 1× USB 3.0. Klíčové vlastnosti • Výkonné zařízení s PoE a ARM 64bit architekturou • CPU 1400 MHz, 4 jádra, 1 GB RAM, 1 GB NAND • 2 typy napájení - DC svorkovnice, PoE (24 až 57 V DC) • PoE IN a PoE out na všech osmi ethernetových portech! • Pasivní chlazení bez ventilátorů • Rozhraní: (7) Gigabit, (1) 2.5Gigabit, (1) SFP/SFP+, (1) USB 3.0 • Předinstalován RouterOS L5, verze 7 • Venkovní šasi s IP66 krytím Obsah balení • Zařízení • Šroubky, hmoždinky, kovové příchytky • (2) kovové stahovací pásky Technické parametry Konektory a rozhraní Možnost více WAN:Ano Rychlost LAN:(7) 10/100/1000Mbps + (1) 100M/1G/2.5G Gigabit LAN:Ano Optické rozhraní:(1) 1/10Gbps USB:Ano Napájení Napájení přes PoE:802.3af, 802.3at, 24 .. 57V DC Typ napájení:PoE, DC konektor, DC svorkovnice Počet PoE In portů:8 Typy PoE:PoE-Out + PoE-In Podporované PoE-Out standardy:802.3af, 802.3at Počet PoE Out portů:8 PoE budget [W]:130 Max. spotřeba energie [W]:15 Napájení přes konektor/svorkovnici:24 .. 57V DC Fyzické charakteristiky Provedení:Venkovní Ventilátory:Bez ventilátoru Provozní teplota [°C]:-40 až 70 Šířka [mm]:222 Výška [mm]:239 Hloubka [mm]:57 Hardware CPU:88F7040 Frekvence CPU [MHz]:1400 Počet CPU jader:4 Interní uložiště [MB]:1024 RAM [MB]:1024 Software Operační systém:RouterOS - L5 Podpora IPv6:Ano Výchozí IP adresa:192.168.88.1 Výchozí jméno a heslo:admin / -
Skladem v eshopu
Popis QNAP QSW-2104-2T-R2 QNAP switch 2x 10GbE RJ45, 5x 2,5GbE RJ45, neřízený switch Detaily Typ správy Neřízený Počet portů 6 10GbE BASE-T (RJ45) 2 10 G/5 G/2,5 G/1 G/100 M 2.5GbE (RJ45) 4 Popis napájecí jednotky Adaptér Max. spotřeba ene
Ano, centrál. sklad

Plug-and-play switch, 5 RJ45 portů s podporou rychlostí 100Mbps / 1G / 2.5G / 5G / 10G, přepínací kapacita 100 GB/s, tabulka MAC adres o velikosti 32K, Auto MDI/MDI-X, Auto-Negotiation, Flow Control, DCB, Prioritní režim, IGMP Snooping. Černá.
Skladem v eshopu

Cisco switch CBS350-48FP-4G-EU - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Řízené switche řady Cisco Business 350 jsou spolehlivými stavebními prvky pro sítě malých firem. Díky intuitivnímu ovládacímu panelu, pokročilým funkcím a všudypřítomnému zabezpečení urychlují spravované switche řady Cisco Business 350 vaši digitální transformaci. Záruka platná do End of Support 31. 10. 2029. Oznámení End of Life pro CISCO CBS350 Stránky produktu: CBS350-48FP-4G-EU Quick start guide: Quick start guide Switching capacity and forwarding rate (All switches are wire speed and nonblocking) Capacity in Millions of Packets per Second (mpps) (64-byte packets) 77,38 Switching Capacity in Gigabits per Second (Gbps) 104 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d Spanning Tree support Fast convergence using 802.1w (Rapid Spanning Tree [RSTP]), enabled by default Multiple Spanning Tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+) and Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4,094 VLANs simultaneously Port-based and 802.1Q tag-based VLANs; MAC-based VLAN; protocol-based VLAN; IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1x client authentication CPE VLAN Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers network wide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN Translation Support for VLAN One-to-One Mapping. In VLAN One-to-One Mapping, on an edge interface customer VLANs (C-VLANs) are mapped to service provider VLANs (S-VLANs) and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link Detection (UDLD) UDLD monitors physical connection to detect unidirectional links caused by incorrect wiring or cable/port faults to prevent forwarding loops and black holing of traffic in switched networks Dynamic Host Configuration Protocol (DHCP) Relay at Layer 2 Relay of DHCP traffic to DHCP server in different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; supports 2K multicast groups (source-specific multicasting is also supported) IGMP Querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols. Head-of-Line (HOL) blocking HOL blocking prevention Loopback Detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wirespeed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wirespeed routing of IPv6 packets Layer 3 Interface Configuration of Layer 3 interface on physical port, Link Aggregation (LAG), VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for classless interdomain routing RIP v2 Support for Routing Information Protocol version 2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to different next hop based on IPv4 or IPv6 Access Control List (ACL) DHCP Server Switch functions as an IPv4 DHCP server serving IP addresses for multiple DHCP pools/scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Security ecure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (Authenticator role) 802.1X: Remote Authentication Dial-In User Service (RADIUS) authentication and accounting, MD5 hash; guest VLAN; unauthenticated VLAN, single/multiple host mode and single/multiple sessions Supports time-based 802.1X; dynamic VLAN assignment; MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard This prevents edge devices not in the network administrator’s control from becoming Spanning Tree Protocol root nodes STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) DHCP snooping Filters out DHCP messages with unregistered IP addresses and/or from unexpected or untrusted interfaces. This prevents rogue devices from behaving as DHCP Servers. IP Source Guard (IPSG) When IP Source Guard is enabled at a port, the switch filters out IP packets received from the port if the source IP addresses of the packets have not been statically configured or dynamically learned from DHCP snooping. This prevents IP address spoofing. Dynamic ARP Inspection (DAI) The switch discards ARP packets from a port if there are no static or dynamic IP/MAC bindings or if there is a discrepancy between the source or destination addresses in the ARP packet. This prevents man-in-the-middle attacks. IP/MAC/Port Binding (IPMB) The preceding features (DHCP Snooping, IP Source Guard, and Dynamic ARP Inspection) work together to prevent DOS attacks in the network, thereby increasing network availability Secure Core Technology (SCT) Makes sure that the switch wil
Skladem v eshopu


Registrace dealerské ceny: https://docs.google.com/forms/d/1sWwsswsbBk36eZx4CJrfl47qUvrORQyYz7kMjrt2f_c/prefill Popis produktu Inteligentní cloudově i přes webové rozhraní spravovatelný smart desktop PoE switch RG-ES205GC-P od značky Ruijie, nabízí cenově efektivní řešení s 5 Gigabit LAN porty z čehož 4 porty podporují 802.3af/at PoE s celkovým PoE budgetem 54 W. Tento kompaktní přepínač je ideální pro síťové aplikace, které vyžadují výkon a spolehlivost. Co se výčtu funkcí týče, switch nabízí tichý chod bez ventilátorů, podporu až 16 VLAN, DHCP snooping, testování kabelu, ochranou proti zakruhování a v rámci PoE možnost použití až na vzdálenost 250 m při snížení linkové rychlosti na 10 Mbps. Klíčové vlastnosti • 5× 10/100/1000 Mbps LAN porty • 4× 802.3af/at PoE - max. 30 W/port, PoE budget 54 W • Kvalitní provedení, kovové šasi • Bez venilátoru • Nízká spotřeba - max. 6 W • Správa přes webové rozhraní a cloud • Celoživotní správa na Ruijie Cloud kdykoli a kdekoli • Rozpoznávání IP kamer - jedinečná hodnota pro CCTV síť • Automatická prevence proti zakruhování • Podpora Long Range PoE na vzdálenost 250 m Obsah balení • Zařízení • Napájecí adaptér 5 4V/1.1 A Technické parametry Konektory a rozhraní Rychlost LAN:(5) 10/100/1000Mbps Napájení Typ napájení:DC konektor Typy PoE:PoE-Out (pouze) Podporované PoE-Out standardy:802.3af, 802.3at Počet PoE Out portů:4 PoE budget [W]:54 PoE na vzdálenost až 250m:Ano Max. spotřeba energie [W]:6 Napájení přes konektor/svorkovnici:54V / 1,1A Fyzické charakteristiky Provedení:Desktop Ventilátory:Bez ventilátoru Šasi:Kovové Tlačítka:Reset Provozní teplota [°C]:0 až 40 Šířka [mm]:148 Výška [mm]:26 Hloubka [mm]:78 Obecné Rychlost přepínání [Gbps]:10 Tabulka MAC adres:2000 Rychlost předávání paketů [Mpps]:7,4 Software Web management:Ano Management:Webové rozhraní, Ruijie cloud Funkce:VLAN, DHCP snooping Výchozí IP adresa:10.44.77.200 Výchozí jméno a heslo:Nastavuje se při prvním spuštění
Dodání 3-5 dní
Plastový držák je určený pro uchycení síťových jednotek značky TP-Link do 19" a 10" racku . V případě montáže do 19" racku je možné jej namontovat na levou i pravou stranu nebo dva držáky vedle sebe. Rozměry (WxDxH): Vnitřní (mm): 226 × 131 × 35 mm Vnější (mm): 250 x 140 x 44 mm Kompatibilní zařízení: TL-SG108-M2 TL-SX105 ER7206 ER7212PC
Skladem v eshopu

PRŮMYSLOVÁ BRÁNA IOT TRB246 je průmyslová 4G LTE brána vybavená I/O, RS232, RS485 a ethernetovými rozhraními pro IoT řešení vyžadující všestrannost a spolehlivou podporu M2M komunikace. Tato brána má funkci dual SIM a podporuje více protokolů, jako jsou
Ano, centrál. sklad

NETGEAR GS724TP Řízený L2/L3/L4 Gigabit Ethernet (10/100/1000) Podpora napájení po Ethernetu (PoE) Modrá Podpora kontroly toku: Ano Podpora 10G: Ano Podpora VLAN: Ano Broadcast storm control: Ano Prot
Dodání 3 dny

8PORTOVÝ PŘEPÍNAČ DAHUA SF1008-EUR – Perfektní řešení pro malé počítačové sítě PŘEPÍNAČ SF1008-EUR je spolehlivý 8portový přepínač od společnosti Dahua, určený pro malé počítačové sítě a rezidenční sítě. Jeho robustní konstrukce a vysoký výkon z něj činí vynikající volbu pro ty, kteří hledají efekt
Dodání 3-5 dní
TP-Link. Model - Archer AX1500. Typ routeru - WiFi / LAN / VPN. Šířka - 260 mm. Hloubka - 135 mm. Výška - 38,6 mm. Barva - Černá. Konektory - RJ-45. Síťové standardy- IEEE 802.11a, IEEE 802.11ac, IEEE 802.11b, IEEE 802.11g, IEEE 802.11n, IEEE 802.11ax (Wi-Fi 6). Režim pásma - Dual Band (2,4, 5 GHz)
3-5 dní dostupno
Aruba 6100 12G Class4 PoE 2G/2SFP+ 139W Switch JL679A#ABB Aruba 6100 12G Class4 PoE 2G/2SFP+ 139W Switch (JL679A) Description 12x ports 10/100/1000BASE-T Ports 2x 1G/10G SFP ports 2x 1GbE ports Supports PoE Standards IEEE 802.3af, 802.3at 1x USB-C Console Port 1x USB Type-A Host port Power supplies Fixed power supply (165W) Up to 139W of Class 4 PoE Power Fans Fanless Physical characteristics Dimensions (H) 4.39 cm (W) 25.4 cm (D) 25.5 cm (1.73" x 10.0" x 10.04") Configuration Weight 2.78 kg (6.13 lbs) Additional Specifications CPU Dual Core ARM Cortex A9 @ 1016 Mhz Memory and Flash 4 GB DDR3 16 GB eMMC Packet Buffer 12.38MB (4.5MB Ingress/7.875MB Egress) Performance Model Switching Capacity 68 Gbps Model Throughput Capacity 45.1 Mpps Average Latency (LIFO-64-bytes packets) 1 Gbps: 2.3 µSec , 10 Gbps: 2.6 µSec Switched Virtual Interfaces (dual stack) 16 IPv4 Host Table (ARP) 1,024 IPv6 Host Table (ND) 512 IPv4 Unicast Routes 512 IPv6 Unicast Routes 512 MAC Table Capacity 8,192 IGMP Groups 512 MLD Groups 512 IPv4/IPv6/MAC ACL Entries (ingress) 256 / 128 / 256 Environment Operating Temperature 32°F to 113°F (0°C to 45°C) up to 5000 ft (1.5 km) derate -1°C for every 1000 ft (305 m) from 5000 ft (1.5 km) to 10000 ft (3.0 km) Operating Relative Humidity 15% to 95% at 104°F (40°C) non-condensing Non-Operating -40°F to 158°F (-40°C to 70°C) up to 15000 ft (4.6 km) Non-Operating Storage Relative Humidity 15% to 90% @ 149°F (65°C) non-condensing Max Operating Altitude 10000 feet (3 km) Max Max Non-Operating Altitude 15000 feet (4.6 km) Max Acoustic Sound Power, LWAd = 0 Bel Sound Pressure, LpAm (Bystander) = 0 dB Primary Airflow - Aruba 6100 12G Class4 PoE 2G/2SFP+ 139W Switch (JL679A) Electrical Characteristics Frequency 50 / 60 Hz AC Voltage 100-127 VAC / 200-240 VAC Current 1.8 A / 0.9 A Power Consumption (230 VAC) Idle: 16W Max Power (w/o PoE): 21.9W Max Power (w/ PoE): 170W Safety UL 60950-1; IEC 60950-1; EN 60950-1; CAN/ CSA-C22.2 No. 60950-1; EN 60825-1 UL 62368-1 Ed. 2; IEC 62368-1 Ed. 2; EN 62368- 1:2014 Emissions VCCI-CISPR 32, Class A; CNS 13438; ICES-003 Issue 6 Class A; FCC CFR 47 Part 15, Class A; EN 55032: 2015 +AC:2016 / CISPR-32, Class A Lasers EN 60825-1:2007 / IEC 60825- 1:2007 Class 1 Class 1 Laser Products / Laser Klasse 1 (Applicable for accessories - Optical Transceivers only) Immunity Generic CISPR 24 / CISPR 35 EN EN 55024:2010 / EN 55035:2017 ESD IEC 61000-4-2 Radiated IEC 61000-4-3 EFT/Burst IEC 61000-4-4 Surge IEC 61000-4-5 Conducted IEC 61000-4-6 Power frequency magnetic field IEC 61000-4-8 Voltage dips and interruptions IEC 61000-4-11 Harmonics EN 61000-3-2, IEC 61000-3-2 Flicker EN 61000-3-3, IEC 61000-3-3 Mounting and Enclosure Mounts in an EIA-standard 19-inch telco rack or equipment cabinet (rack-mounting kit available); horizontal surface mounting; wall mounting
Ano, centrál. sklad
TP-Link JetStream switch TL-SX3206HPP 6portový řízený switch JetStream 10GE L2+ se 4 PoE++ porty Bleskurychlé připojení s plnou 10G rychlostí - Nabízí připojení s velkou šířkou pásma pomocí čtyř 10Gbit/s RJ45 portů a dvou 10Gbit/s SFP+ slotů. Napájení PoE++ s výstupním výkonem až 200 W - Čtyři 10G RJ45 porty podporující 802.3af/at/bt PoE++ napájení až 60 W na port jsou ideální pro nasazení přístupových bodů Omada WiFi 6 a WiFi 6E. Multi-Gigabitové sítě - 10G RJ45 porty podporují 5 rychlostí připojení (100M/1G/2,5G/5G/10G) a SFP+ sloty lze osadit 10G i 1G transceivery Pokročilé L2 a L2+ funkce - Podporuje kompletní sadu L2 a L2+ funkcí, jako jsou statický routing, QoS na podnikové úrovni a IGMP Snooping. Robustní bezpečnostní strategie - Pomáhá chránit investice do místní sítě pomocí integrované funkce vázání na IP-MAC-Port, ACL, zabezpečením portů, ověřováním 802.1X a dalšími funkcemi. Statický routing - Pomáhá směrovat interní provoz pro efektivnější využítí síťových prostředků. Centralizovaná cloudová správa - Integrace s platformou Omada SDN pro cloudový přístup a vzdálenou správu. Samostatná správa - Web, CLI (konzole port, Telnet, SSH), SNMP, RMON a Dual Image přináší výkonné možnosti správy. Více informací o TP-Link PoE technologii > Zjistit více o Omada Cloud SDN>? Více informací o TP-Link 10G Multi-Gig technologii > Stránky produktu: https://www.tp-link.com/cz/business-networking/managed-switch/tl-sx3206hpp/ Technické specifikace HARDWARE FEATURES Interface • 4× 100/1000/2500/5000/10000 Mbps RJ45 Ports • 2× 10G SFP+ Slots • 1× RJ45 Console Port • 1× Micro-USB Console Port Fan Quantity 2 Power Supply 100-240 V AC~50/60 Hz PoE Ports (RJ45) • Standard: 802.3bt/at/af compliant • PoE++ Ports: 4 Ports, up to 60 W per port • Power Budget: 200 W Dimensions ( W x D x H ) 11.6 × 7.1 × 1.7 in (294× 180 × 44 mm) Mounting • Rack Mountable • Desktop Max Power Consumption • 27.29 W (110V/60Hz) (no PD connected) • 244.90 W (110V/60Hz) (with 200 W PD connected) Max Heat Dissipation • 93.12 BTU/h (110 V/60 Hz) (no PD connected) • 835.67 BTU/h (110 V/60 Hz) (with 200 W PD connected) PERFORMANCE Switching Capacity 120 Gbps Packet Forwarding Rate 89.28 Mpps MAC Address Table 32 K Jumbo Frame 9 KB SOFTWARE FEATURES Quality of Service • 8 priority queues • 802.1p CoS/DSCP priority • Queue scheduling - SP (Strict Priority) - WRR (Weighted Round Robin) - SP+WRR • Bandwidth Control - Port/Flow based Rating Limiting • Smoother Performance • Action for Flows - Mirror (to supported interface) - Redirect (to supported interface) - Rate Limit - QoS Remark L2 and L2+ Features • Link Aggregation - static link aggregation - 802.3ad LACP - Up to 8 aggregation groups, containing 8 ports per group • Spanning Tree Protocol - 802.1d STP - 802.1w RSTP - 802.1s MSTP - STP Security: TC Protect, BPDU Filter, Root Protect • Loopback Detection - Port based - VLAN based • Flow Control - 802.3x Flow Control - HOL Blocking Prevention • Mirroring - Port Mirroring - CPU Mirroring - One-to-One - Many-to-One - Tx/Rx/Both L2 Multicast • IGMP Snooping - IGMP v1/v2/v3 Snooping - Fast Leave - IGMP Snooping Querier - IGMP Authentication • IGMP Authentication • MLD Snooping - MLD v1/v2 Snooping - Fast Leave - MLD Snooping Querier - Static Group Config - Limited IP Multicast • MVR • Multicast Filtering: 256 profiles and 16 entries per profile VLAN • VLAN Group - Max 4K VLAN Groups • 802.1Q Tagged VLAN • MAC VLAN: 10 Entries • Protocol VLAN: Protocol Template 16, Protocol VLAN 16 • Private VLAN • GVRP • VLAN VPN (QinQ) - Port-Based QinQ - Selective QinQ • Voice VLAN Access Control List • Time-based ACL • MAC ACL - Source MAC - Destination MAC - VLAN ID - User Priority - Ether Type • IP ACL -Source IP - Destination IP - Fragment - IP Protocol - TCP Flag - TCP/UDP Port - DSCP/IP TOS - User Priority • Combined ACL • Packet Content ACL • IPv6 ACL • Policy - Mirroring - Redirect - Rate Limit - QoS Remark • ACL apply to Port/VLAN Security • IP-MAC-Port Binding - 512 Entries - DHCP Snooping - ARP Inspection - IPv4 Source Guard: 100 Entries • IPv6-MAC-Port Binding - 512 Entries - DHCPv6 Snooping - ND Detection - IPv6 Source Guard: 100 Entries • DoS Defend • Static/Dynamic Port Security - Up to 64 MAC addresses per port • Broadcast/Multicast/Unicast Storm Control - kbps/ratio control mode • 802.1X - Port base authentication - Mac base authentication - VLAN Assignment - MAB - Guest VLAN - Support Radius authentication andaccountability • AAA (including TACACS+) • Port Isolation • Secure web management through HTTPS with SSLv3/TLS 1.2 • Secure Command Line Interface (CLI) management with SSHv1/SSHv2 • IP/Port/MAC based access control IPv6 • IPv6 Dual IPv4/IPv6 • Multicast Listener Discovery (MLD) Snooping • IPv6 ACL • IPv6 Interface • Static IPv6 Routing • IPv6 neighbor discovery (ND) • Path maximum transmission unit (MTU) discovery • Internet Control Message Protocol (ICMP) version 6 • TCPv6/UDPv6 • IPv6 applications - DHCPv6 Client - Ping6 - Tracert6 - Telnet (v6) - IPv6 SNMP - IPv6 SSH - IPv6 SSL - Http/Https - IPv6 TFTP L3 Features • 16 IPv4/IPv6 Interfaces • Static Routing - 48 static routes • Static ARP - 128 Static Entries • Proxy ARP • Gratuitous ARP • DHCP Server • DHCP Relay - DHCP Interface Relay - DHCP VLAN Relay • DHCP L2 Relay Advanced Features • Automatic Device Discovery • Batch Configuration • Batch Firmware Upgrading • Intelligent Network Monitoring • Abnormal Event Warnings • Unified Configuration • Reboot Schedule MIBs • MIB II (RFC1213) • Interface MIB (RFC2233) • Ethernet Interface MIB (RFC1643) • Bridge MIB (RFC1493) • P/Q-Bridge MIB (RFC2674) • RMON MIB (RFC2819) • RMON2 MIB (RFC2021) • Radius Accounting Client MIB (RFC2620) • Radius Authentication Client MIB (RFC2618) • Remote Ping, Traceroute MIB (RFC2925) • Support TP-Link private MIB MANAGEMENT Omada App Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Centralized Management • Omada Cloud-Based Controller • Omada Hardware Controller (OC300) • Omada Hardware Controller (OC200) • Omada Software Controller Cloud Access Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Zero-Touch Provisioning Yes. Requiring the use of Omada Cloud-Based Controller. Management Features • Web-based GUI • Command Line Interface (CLI) through the console port, telnet • SNMP v1/v2c/v3 - Trap/Inform - RMON (1,2,3,9 groups) • SDM Template • DHCP/BOOTP Client • 802.1ab LLDP/LLDP-MED • DHCP AutoInstall • Dual Image, Dual Configuration • CPU Monitoring • Cable Diagnostics • EEE • Password Recovery • SNTP • System Log OTHERS Certification CE, FCC, RoHS Package Contents •TL-SX3206HPP Switch • Power Cord • Quick Installation Guide • Rackmount Kit • Rubber Feet System Requirements Microsoft Windows 98SE, NT, 2000, XP, Vista™ or Windows 7/8/10/11, MAC OS, NetWare, UNIX or Linux. Environment • Operating Temperature: 0–50 °C (32–122 °F); • Storage Temperature: -40–70 °C (-40–158 °F) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% RH non-condensing
Skladem v eshopu
Cisco Catalyst switch C1300-8T-E-2G Sada pro montáž do racku není součástí balení. Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu. Stránky produktu: C1300-8T-E-2G Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 14.88 Switching capacity in gigabits per second (Gbps) 20.0 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4093 VLANs simultaneously Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN Auto surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported) IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wire-speed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Security Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through a web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard Prevents edge devices not in the network administrator’s control from becoming STP root nodes STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) DHCP snooping Filters out DHCP messages with unregistered IP addresses and/or from unexpected or untrusted interfaces. This prevents rogue devices from behaving as DHCP servers IP Source Guard (IPSG) When IPSG is enabled at a port, the switch filters out IP packets received from the port if the source IP addresses of the packets have not been statically configured or dynamically learned from DHCP snooping. This prevents IP address spoofing Dynamic ARP Inspection (DAI) The switch discards ARP packets from a port if there are no static or dynamic IP/MAC bindings or if there is a discrepancy between the source or destination addresses in the ARP packet. This prevents man-in-the-middle attacks IP/MAC/port binding (IPMB) The preceding features (DHCP snooping, IPSG, and DAI) work together to prevent Denial-of-Service (DoS) attacks in the network, thereby increasing network availability Secure Core Technol
Ano, centrál. sklad
TP-Link ER707-M2 Omada Multi-Gigabit VPN Router Dva 2,5G porty : 1× 2,5G WAN a 1× 2,5G WAN/LAN porty poskytují vysokorychlostní agregační konektivitu. Až 6 portů WAN : 2,5G RJ45, gigabitové vlákno a gigabitové RJ45 WAN porty s vyvážením zátěže zvyšují míru využití vícelinkového širokopásmového připojení. Vysoce bezpečná VPN : SSL/IPSec/GER/PPTP/L2TP VPN a OpenVPN jsou ideální pro použití ve více pobočkách a pro WFH. Integrováno do Omada SDN : Podporuje Zero-Touch Provisioning (ZTP), centralizovanou správu cloudu, inteligentní monitorování a další. Centralizovaná správa : Přístup ke cloudu a aplikace Omada poskytují maximální pohodlí při správě. Rozsáhlé funkce zabezpečení : Chraňte svou síť a data pomocí pokročilých zásad brány firewall, obrany proti DoS, filtrování IP/MAC/URL a dalších funkcí zabezpečení. Více informací o Omada Cloud SDN>? Stránky produktu: https://www.tp-link.com/cz/business-networking/vpn-router/er707-m2/ Technické specifikace HARDWARE FEATURES Standards and Protocols • IEEE 802.3, IEEE802.3u, IEEE802.3ab, IEEE802.3z, IEEE 802.3x, IEEE 802.1q • TCP/IP, DHCP, ICMP, NAT, PPPoE, NTP, HTTP, HTTPS, DNS, IPSec, PPTP, L2TP, OpenVPN, SNMP Interface • 1× 2.5G RJ45 WAN Port • 1× 2.5G RJ45 WAN/LAN Port • 1× Gigabit SFP WAN/LAN Port • 4× Gigabit RJ45 WAN/LAN Ports • 1× USB 2.0 Port (Supports USB storage, and LTE backup with LTE dongle) Network Media • 10BASE-T: UTP category 3, 4, 5 cable (Max 100 m) EIA/TIA-568 100? STP (Max 100 m) • 100BASE-TX: UTP category 5, 5e cable (Max 100 m) EIA/TIA-568 100? STP (Max 100 m) • 1000BASE-T: UTP category 5, 5e, 6 cable (Max 100 m) • 2500BASE-T: UTP category 5, 5e, 6 cable (Max 100 m) Fan Quantity Fanless Button Reset Button Power Supply 12V/1.5A Adapter PoE Budget - Flash 128MB NAND DRAM 1 GB DDR4 LED PWR, SYS, SFP, USB, WAN (Speed, Link/Act), LAN (Speed, Link/Act) Dimensions ( W x D x H ) 8.9 × 5.2 × 1.4 in (226 × 131 × 35 mm) Protection 4 kV surge protection Enclosure Steel Mounting Desktop/Wall Mounting Max Power Consumption 14.2 W (with USB2.0 connected) 7.1 W (without USB2.0 connected) PERFORMANCE Concurrent Session 500 New Sessions /Second 4,2 NAT (Static IP) 2364.45 Mbps / 2343.28 Mbps NAT(DHCP) 2364.24 Mbps / 2326.21 Mbps NAT(PPPoE) 2350.93 Mbps / 2125.83 Mbps NAT (L2TP) 1249.04 Mbps / 831.12 Mbps NAT (PPTP) 1169.23 Mbps / 1175.52 Mbps IPsec VPN Throughput ESP-MD5-AES256: 537.12 Mbps ESP-SHA1-AES256: 754.65 Mbps L2TP VPN Throughput Unencrypted: 1442.65 Mbps Encrypted: 346.43 Mbps SSL VPN Throughput 142.99 Mbps 66 Byte Packet forwarding rate 1832.69 Mbps / 1741.84 Mbps 1,518 Byte Packet forwarding rate 2461.18 Mbps / 2457.32 Mbps BASIC FUNCTIONS WAN Connection Type • IPv4_Static IP • IPv4_Dynamic IP • IPv4_PPPOE • IPv4_L2TP • IPv4_PPTP • IPv6_PPP • IPv6_DHCPv6 • IPv6_Static IP • IPv6_6in4 • IPv6_Pass-Through • Mobile Broadband: 4G/3G modem for backup via USB port MAC Clone Modify WAN/LAN MAC Address† DHCP • DHCP Server/Client • DHCP Address Reservation • Multi-IP Interfaces* • Multi-Net DHCP* IPv6 WAN Connection VLAN 802.1Q VLAN IPTV IGMP v2/v3 Proxy ADVANCED FUNCTIONS Advanced Routing • Static Routing • Policy Routing Bandwidth Control • IP/Port-based Bandwidth Control • Guarantee & Limited Bandwidth Load Balance • Intelligent Load Balance • Application Optimized Routing • Link Backup (Timing§, Failover) • Online Detection NAT • One-to-One NAT§ • Multi-Net NAT • Virtual Server • Port Triggering§ • NAT-DMZ • FTP/H.323/SIP/IPSec/PPTP ALG • UPnP Security • Attack Defense: TCP/UDP/ICMP Flood Defense Block TCP Scan (Stealth FIN/Xmas/Null) Block Ping from WAN • Filtering Web Group Filtering URL Filtering Web Security • ARP Inspection: Sending GARP Packets ARP Scanning IP-MAC Binding • Access Control Source/Destination IP Based Access Control Session Limit IP-based Session Limit VPN IPsec VPN • 100 IPSec VPN Tunnels • LAN-to-LAN, Client-to-LAN • Main, Aggressive Negotiation Mode • DES, 3DES, SHA1, AES128, AES192, AES256 Encryption Algorithm • IKEv1/v2 • MD5, SHA1 Authentication Algorithm • NAT Traversal (NAT-T) • Dead Peer Detection (DPD) • Perfect Forward Secrecy (PFS) PPTP VPN • PPTP VPN Server • PPTP VPN Clients (12) • 60 Tunnels (Shared with L2TP) • PPTP with MPPE Encryption L2TP VPN • L2TP VPN Server • L2TP VPN Clients (12) • 60 Tunnels (Shared with PPTP) • L2TP over IPSec OpenVPN • OpenVPN Server • OpenVPN Clients (6) • 66 OpenVPN Tunnels* SECURITY Filtering WEB Group Filtering§ URL Filtering Web Security§ ARP Inspection • Sending GARP Packets§ • ARP Scanning§ • IP-MAC Binding§ Attack Defense • TCP/UDP/ICMP Flood Defense • Block TCP Scan (Stealth FIN/Xmas/Null) • Block Ping from WAN Access Control Source/Destination IP Based Access Control AUTHENTICATION Web Authentication • No Authentication • Simple Password* • Hotspot (Local User/Voucher* /SMS*/Radius*) • External Radius Sever • External Portal Sever* • Facebook* MANAGEMENT Omada App Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Centralized Management • Omada Cloud-Based Controller • Omada Hardware Controller (OC300) • Omada Hardware Controller (OC200) • Omada Software Controller Cloud Access Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Service Dynamic DNS (Dyndns, No-IP, Peanuthull, Comexe) Maintenance • Web Management Interface • Remote Management • Export & Import Configuration • SNMP v1/v2c/v3* • Diagnostics (Ping & Traceroute)§ • NTP Synchronize§ • Syslog Support Zero-Touch Provisioning Yes. Requiring the use of Omada Cloud-Based Controller. Management Features • Automatic Device Discovery • Intelligent Network Monitoring • Abnormal Event Warnings • Unified Configuration • Reboot Schedule • Captive Portal Configuration • ZTP (Zero-Touch Provisioning) OTHERS Certification CE, FCC, RoHS Package Contents • ER707-M2 • Power Adapter • Quick Installation Guide System Requirements Microsoft Windows 98SE, NT, 2000, XP, Vista™ or Windows 7/8/8.1/10, MAC OS, NetWare, UNIX or Linux Environment • Operating Temperature: 0–40 °C (32–104 °F); • Storage Temperature: -40–70 °C (-40–158 °F) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% non-condensing
Skladem v eshopu
MikroTik Switch CRS320-8P-8B-4S+RM; Vysoce výkonný PoE++ (802.bt) switch pro snadné a cenově výhodné napájení bezpečnostních kamer 4K, reklamních panelů nebo dokonce průmyslových automatizačních systémů. CRS320...
Ano, centrál. sklad
20pack Aruba Instant On 1930 24G 4SFP/SFP+ Switch I/O Ports and Slots 24 RJ-45 autosensing 10/100/1000 ports (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE- TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 4 SFP+ 1/10GbE ports Physical Characteristics Dimensions 17.42(w) x 8.72(d) x 1.73(h) in (44.25 x 22.15 x 4.39 cm) (1U height) Weight 5.32 lb (2.41 kg) Processor and Memory ARM Cortex-A9 @ 800 MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5 MB Packet Buffer 1.5 MB Performance 100 Mb latency < 4.7 uSec 1000 Mb latency 10000 Mb latency Throughput (Mpps) 95.23 Mpps Capacity 128 Gbps Routing table size (# of static entries) 32 MAC address table size (# of entries) 16,000 Reliability MTBF (years) 158 Environment Operating temperature 32°F to 104°F (0°C to 40°C) Operating relative humidity 15% to 95% @ 104°F (40°C) Non-operating temperature -40°F to 158°F (-40°C to 70°C) Non-operating relative humidity 15% to 95% @ 140°F (60°C) Altitude Up to 10,000ft (3.048 Km) Acoustic Power: 0 dB (no fan) Electrical Characteristics Frequency 50-60 Hz AC voltage 100-240V Current 0.5/0.3 A Maximum power rating 22.6 W Idle power 9.3 W PoE power n/a Power supply Internal power supply Safety UL 60950-1; IEC 60950-1;EN 60950-1; CAN/CSA-C22.2 No. 60950-1; EN 60825-1 UL 62368-1 Ed. 2; IEC 62368-1 Ed. 2; EN 62368-1:2014 Emissions VCCI-CISPR 32, Class A; CNS 13438; ICES-003 Issue 6 Class A; FCC CFR 47 Part 15, Class A; EN 55032: 2015 +AC:2016 / CISPR-32, Class A Immunity Generic CISPR 24 / CISPR 35 EN EN 55024:2010 / EN 55035:2017 ESD IEC 61000-4-2 Radiated IEC 61000-4-3 EFT/Burst IEC 61000-4-4 Surge IEC 61000-4-5 Conducted IEC 61000-4-6 Power frequency magnetic field IEC 61000-4-8 Voltage dips and interruptions IEC 61000-4-11 Harmonics IEC 61000-3-2, EN 61000-3-2 Flicker IEC 61000-3-3, EN 61000-3-3 Device Management Aruba Instant On Cloud; Web browser; SNMP Manager Mounting Mounts in an EIAstandard 19 in. telco rack or equipment cabinet. 2-post rack kit included Supports table-top mounting Supports rackmounting Supports wall-mounting with ports facing either up or down Supports under-table mounting using the brackets provided Must be mounted top surface up. To prevent possible impact to longterm reliability, product should not be mounted Transceivers Aruba Instant On 1G SFP LC SX 500m OM2 MMF Transceiver (R9D16A) Aruba 1G SFP LC LX 10km SMF XCVR (J4859D) Aruba 1G SFP RJ45 T 100m Cat5e XCVR (J8177D) Aruba Instant On 10G SFP+ LC SR 300m OM3 MMF Transceiver (R9D18A) Aruba 10G SFP+ LC LR 10km SMF Transceiver (J9151E) Aruba Instant On 10G SFP+ to SFP+ 1m DAC (R9D19A) Aruba Instant On 10G SFP+ to SFP+ 3m DAC (R9D20A) High-performance, smart-managed switches designed with small businesses in mind Whether you own a cafe, a design firm or a tech startup, a reliable and secure network plays a critical role in the success of your business. And you need a network solution that gives you peace of mind, allowing you to focus on growing your business instead of managing problems with your network. Aruba Instant On makes it easy to keep network users happy, mobile and IoT devices connected, and your network secure. The Aruba Instant On 1930 switches features advanced, smart-managed, fixed- configuration Gigabit switches designed for small businesses that are easy-to-deploy and affordable. They re made to handle today s bandwidth-heavy applications like voice and video conferencing, enabling consistent connectivity to enhance performance. Using either the Instant On mobile app or the cloud-based web portal, you can quickly set up, monitor and manage the 1930 switch series from anywhere at any time. What s more, up to 30 W PoE power delivery is available out-of-the-box for your class 4 PoE devices, like access points, surveillance cameras and VoIP phones, all easily managed from the same platform. Built-in security features protect your network from unauthorized access by allowing you to segment traffic and define access to each area of the network. And all of this is included in the price of the hardware - there are no hidden subscription or licensing fees. Key Features Smart-managed layer 2+ Ethernet switch series ready to deploy in 8-, 24-and 48-port for non-PoE and Class 4 PoE (i.e. PoE+) models PoE to power APs and IoT devices like IP phones, surveillance cameras and door locks Two (2) dedicated 1G SFP fiber ports on 8-port models, and four (4) dedicated 1G/10G SFP+ fiber ports on 24-/48-port models to eliminate traffic bottlenecks across your network Security controls let you define access in each area of your network, keeping your business data safe Convenient mobile app and web- based GUI for set up, management and troubleshooting. Standard Features Simplicity at its best Plug-and-play switches that work together with Instant On APs right out of the box Mobile app to easily setup, monitor and manage your network Security you can count on Protect your network from unauthorized access with IEEE 802.1X and VLANs Automatic denial-of-service (DOS) monitors and protects the network against malicious attacks We ve got you covered No extra licensing or subscription fees Industry-leading limited lifetime warranty and support. The Instant On Differentiators Easy setup and management The Aruba Instant On mobile app allows you to set up, manage, and monitor Instant On switches and access points directly from your phone. Within the app, you get guided step-by-step instructions to install Instant On devices to get your network up and running quickly - no technical expertise required. And cloud-based access allows you to access the network from anywhere, at any time. Non-intrusive, aesthetic design Aruba Instant On switches are designed to complement the sleek and clean look of the Instant On access points, and to blend discreetly into your site s environment. The 8-port models, as well as the 24- and 48-port non PoE+ models, are fan-less, making them ideal for quiet office deployments. High performance with flexible options The series consists of four (4) Class 4 PoE (PoE+) switches, and three (3) non-POE switches including 8- 24- and 48-port Gigabit Ethernet switches. The two (2) dedicated 1G SFP fiber ports on 8-port models, and four (4) dedicated 1G/10G SFP+ fiber ports on 24-/48-port models, ensure high performance and eliminate traffic bottlenecks across the network. Customizable features include basic Layer 2 features like VLANs and link aggregation, as well as advanced features such as Layer 3 IPv4 static routing, ACLs, and Spanning Tree Protocols, and IPv6 Host mode. Optimized user experience The Aruba Instant On mobile app provides common workflows for Instant On switches and access points making it easier to configure, monitor and manage your network remotely without the need for additional hardware like cloud keys or VPN. You can also update firmware on your Instant On devices dir...
Ano, centrál. sklad
WiFi 6 AX, LTE Cat. 7 300/100 Mb/s, 1× 2,5Gb LAN, 4× GLAN, 1 GB RAM, RouterOS L4, USB, Micro SIM.
Ano, centrál. sklad
Popis produktu Systémové řešení platforem firmy MikroTik pro poskytovatele bezdrátového připojení k síti. Cloud Router Switch CRS304-4XG-IN je 5portový switch, poháněný operačním systémem RouterOS, se čtyřmi 10G a jedním 1G ethernetovým portem v desktopovém provedení. Tento switch je kompaktní, ale vysoce výkonný, navržený tak, aby zjednodušil vaše rutinní nastavení sítě. Narozdíl od typických podobných produktů je nový CRS304 vybaven čtyřmi 10gigabitovými ethernetovými porty připravenými k okamžitému použití. Nepotřebujete žádné další moduly SFP, je čistě plug-and-play. Navíc zde má k dispozici další gigabitový ethernetový port - pro účely správy. Je vybaven bočním držákem na lištu DIN a standardními šroubovými upevňovacími body na zadní straně, což umožňuje snadnou instalaci. Kromě toho lze boční držák na lištu DIN přesunout na zadní stranu switche. CRS304 je vybaven krytem, který slouží jako robustní, lehký chladič, což eliminuje potřebu aktivního chlazení. Toto provedení bez ventilátoru zajištuje tichý provoz, takže je ideální pro jakékoliv prostředí, kde je problémem hluk - kanceláře, knihovny... Více možností napájení pro maximální spolehlivost Redundance napájení je klíčovou vlastností CRS304. Nabízí čtyři různé možnosti napájení: 2x jack (12 - 57V DC), dvoupinový konektor a PoE-in. Přepínač automaticky vybírá zdroj napájení s nejvyšším napětím, čímž zajišťuje nepřerušovaný provoz. CRS304 je poháněn dvoujádrovým procesorem ARM, který poskytuje dostatečný výkon. Mezi jeho funkce patří např. přesměrování portu, filtrování MAC, VLAN, broadcast storm control, či omezení šířky pásma. Obsah balení • Napájecí adaptér (48V / 0,95A) • Montážní sada CRS304-4XG-IN CRS304-4XG-IN je vysoce výkonný a kompaktní 5portový switch od renomované společnosti MikroTik, určený pro profesionální síťová řešení. Tento model disponuje čtyřmi 10G ethernetovými porty a jedním 1G ethernetovým portem, což umožňuje bleskově rychlé datové přenosy. Switch je vybaven operačním systémem RouterOS, který nabízí pokročilé funkce jako VLAN, filtrování MAC adres, QoS a mnoho dalších možností síťového managementu. Díky kompaktnímu desktopovému provedení je zařízení vhodné pro umístění na pracovní plochu, ať už v kanceláři nebo domácím prostředí. Pasivní chlazení bez ventilátorů zajišťuje tichý provoz, což je ideální pro prostředí, kde je hluk nežádoucí, jako jsou knihovny nebo kanceláře. CRS304-4XG-IN nabízí také redundance napájení se dvěma DC jacky a PoE-in, čímž zajišťuje vysokou spolehlivost a nepřerušovaný provoz i v náročných podmínkách. Zařízení je navíc vybaveno bočním držákem pro montáž na lištu DIN a šroubovacími upevňovacími body, což usnadňuje instalaci. Technické parametry Konektory a rozhraní Rychlost LAN:(4) 100M/1G/2.5G/5G/10Gbps + (1) 10/100/1000Mbps Gigabit LAN:Ano Napájení Napájení přes PoE:802.3af, 802.3at, 36 .. 57V DC Typ napájení:PoE, DC konektor Redundantní napájení:Ano Max. spotřeba energie [W]:21 Napájení přes konektor/svorkovnici:48V / 1A Fyzické charakteristiky Provedení:Na DIN lištu Provozní teplota [°C]:-40 až 70 Šířka [mm]:128 Výška [mm]:176 Hloubka [mm]:35 Hardware CPU:Dual Core Frekvence CPU [MHz]:1200 Počet CPU jader:2 Interní uložiště [MB]:32 RAM [MB]:512
Ano, centrál. sklad

Registrace dealerské ceny: https://docs.google.com/forms/d/1sWwsswsbBk36eZx4CJrfl47qUvrORQyYz7kMjrt2f_c/prefill Popis produktu Ruijie RG-EG310GH-E je kabelový Gigabitový router do 19" racku s dostatečným VPN výkonem pro obsloužení poboček a vzdáleně pracujících pracovníků v rámci firmy. Bezpečný a spolehlivý router s vlastním webovým managementem, možností správy přes Ruijie Cloud odkudkoliv, blokování obsahu podle typu aplikace, inteligentní Multi-WAN load balancing s možností využít až 4 WAN porty zároveň. Router nabízí 1 Gigabitovými WAN port, 6x Gigabit LAN, 3 Gigabitový LAN/WAN porty a celkový výkon v NATu 1.5 Gbps. Router pro přístup do lokální sítě umožňuje i několik možností VPN serverů a to konkrétně: IPsec, PPTP, L2TP a OpenVPN. Limity VPN • IPsec: 230 Mbps, max. 64 tunelů • L2TP: 640 Mbps, max. 64 tunelů • OpenVPN: 100 Mbps, max. 64 tunelů Obsah balení • Zařízení • Napájecí kabel • Úchyty do racku • Racková sada Technické parametry Konektory a rozhraní Rychlosti WAN:(1) 10/100/1000Mbps Možnost více WAN:Ano Rychlost LAN:(6) 10/100/1000Mbps + (3) 10/100/1000Mbps LAN/WAN Gigabit LAN:Ano Napájení Typ napájení:Ze sítě (230V) Max. spotřeba energie [W]:15 Napájení přes konektor/svorkovnici:230V AC Fyzické charakteristiky Provedení:Rackmount Ventilátory:Bez ventilátoru Šasi:Kovové Tlačítka:Reset Provozní teplota [°C]:0 až 40 Šířka [mm]:440 Výška [mm]:44 Hloubka [mm]:200 Hardware Frekvence CPU [MHz]:1350 Počet CPU jader:2 Obecné Propustnost NAT [Mb/s]:1500 Propustnost VPN IPsec VPN [Mb/s]:230 Software Podporované VPN:PPTP, L2TP, IPSec, OpenVPN Web management:Ano Management:Webové rozhraní, Ruijie cloud Podpora IPv6:Ano Výchozí IP adresa:192.168.110.1 Výchozí jméno a heslo:Nastavuje se při prvním spuštění
Dodání 3-5 dní

Omada SG6654X je L3 managovatelný switch, který nabízí L3 routing, bleskurychlé optické připojení 10 Gb/s, stohování a redundantní napájecí zdroje. Switch přichází s 48 gigabitovými RJ45 porty, 6× 10 Gbps SFP+ sloty a má možnost fyzického stohování. V kom
Ano, centrál. sklad

Klíčové vlastnosti Trasy přizpůsobené pro velká vozidla Živá upozornění na omezení Velký HD dotykový displej Prověřené světové mapy TomTom Služba TomTom Traffic Upozornění na rychlostní radary na 1 rok Vysoký výkon a rychlé reakce Pohodlné hlasové ovládání Pohyblivé navádění jízdními pruhy Rychlé aktualizace map přes Wi-Fi NOVĚ Vylepšené vizuální nápovědy NOVĚ Uložení profilů pro více vozidel NOVĚ Vyhýbání se nízkoemisním zónám NOVĚ USB-C Video TomTom GO Expert Plus Nová špičková navigace pro profesionální řidiče Na cestách na vás mohou čekat různá překvapení. Se správnou GPS navigací však budete vždy připraveni na vše. Zařízení TomTom GO Expert Plus je navrženo tak, aby profesionální řidiče dovedlo do cíle co nejefektivnější cestou. Nabízí spoustu navigačních funkcí pro velká vozidla. Mimořádně zřetelná obrazovka, pohodlné hlasové ovládání Prohlédněte si svou trasu ve velmi vysokých detailech na 6" / 7" dotykovém displeji, který se může chlubit nejlepším rozlišením na trhu. A díky ovládání pomocí hlasových příkazů můžete zařízení TomTom GO Expert Plus ovládat, aniž byste museli sundat ruce z volantu. Snadno použitelný držák Click-and-Drive navíc drží GPS navigaci bezpečně na místě. Nastavení profilu vozidla Jízda po silnici, mostě nebo v tunelu, které nejsou vhodné pro vaše vozidlo, není nikdy příjemná a většinou vás zpozdí. Proto zařízení TomTom GO Expert Plus přizpůsobuje každou trasu rozměrům vašeho vozidla. Stačí přejít do nabídky „Nastavení“ v hlavní nabídce, klepnout na položku „Mé vozidlo“ a klepnutím na jednotlivá nastavení zadat informace o vašem vozidle. TomTom Traffic Živé dopravní informace jsou skvělým způsobem, jak mít přehled o dopravních zácpách, uzavírkách silnic a nehodách, ale služba TomTom Traffic umí mnohem víc. Nabízí rychlejší, alternativní trasy, když zjistí, že je před vámi hustý provoz, díky čemuž strávíte jízdou méně času, spotřebujete méně paliva a v konečném důsledku budete mít i menší dopad na životní prostředí. Ukázka nastavení BT připojení Vyhýbání se nízkoemisním zónám Nyní můžete zvolit, že se chcete vyhnout nízkoemisním zónám, což bude zohledněno při plánování trasy. To je užitečné zejména pro starší nákladní vozidla. Vylepšené vizuální nápovědy Poutavé animace přes celou obrazovku, které zobrazují nadcházející navigační pokyny. Nikdy nezmeškáte odbočku nebo sjezd, ani když jedete s vypnutým zvukem. Přizpůsobte si zařízení Go Expert Plus Nikdo nepoužívá GPS navigaci tak často jako profesionální řidič. Proto navigační zařízení TomTom GO Expert Plus nabízí možnost úpravy vzhledu. Můžete změnit barvu mapy, čáru trasy a další prvky podle svých preferencí nebo potřeb zlepšení viditelnosti. Velmi rychlá odezva a snadné používání Díky vysokému výpočetnímu výkonu zařízení TomTom GO Expert Plus okamžitě reaguje na váš dotyk. Jednoduché rozhraní přináší intuitivnější navigaci, od plánování tras až po vyhledávání bodů zájmu v okolí. 5GHz pásmo Wi-Fi pak zajišťuje rychlé aktualizace map a softwaru. Pokrytí map Albánie, Alžírsko 70 %, Andorra, Angola 42 %, Antigua a Barbuda, Argentina, Austrálie 99 %, Rakousko, Bahamy, Bahrajn, Barbados, Bělorusko 73 %, Belgie, Belize, Benin 14 %, Bermudy, Bolívie 70 %, Bonaire, Svatý Eustach a Saba, Bosna a Hercegovina, Botswana 62 %, Brazílie, Brunej, Bulharsko, Burkina Faso 12 %, Burundi 7 %, Kamerun 12 %, Kanada, Kapverdy, Kajmanské ostrovy, Středoafrická republika 18 %, Čad 11 %, Chile, Kolumbie, Kongo 27 %, Kostarika 95 %, Chorvatsko, Kuba 31 %, Kypr, Česká republika, Demokratická republika Kongo 29 %, Dánsko, District of Columbia, Džibuti 70 %, Dominika 38 %, Dominikánská republika 32 %, Ekvádor 64 %, Egypt 96 %, Salvador 94 %, Rovníková Guinea 20 %, Estonsko, Etiopie 3 %, Faerské ostrovy, Finsko, Francie, Francouzská Guyana, Gabon 51 %, Gambie 44 %, Německo, Ghana 42 %, Gibraltar, Řecko, Grenada, Guadeloupe, Guatemala 94 %, Guinea 21 %, Guinea-Bissau 92 %, Guyana 86 %, Haiti 31 %, Honduras 95 %, Hongkong, Maďarsko, Island, Indonésie 78 %, Irák 20 %, Irsko, Izrael, Itálie, Pobřeží slonoviny, Jamajka 3 %, Jordánsko, Kazachstán, Keňa 30 %, Kosovo, Kuvajt, Lotyšsko, Libanon, Lesotho, Libérie 32 %, Lichtenštejnsko, Litva, Lucembursko, Macao, Makedonská republika, Madagaskar 28 %, Malawi 13 %, Malajsie 97 %, Mali 17 %, Malta, Martinik, Mauritánie 24 %, Mauricius, Mayotte, Mexiko, Moldavsko, Monako, Černá Hora, Maroko, Mosambik 25 %, Namibie 96 %, Nový Zéland, Nikaragua 94 %, Niger 17 %, Nigérie 53 %, Norsko, Omán, Panama, Paraguay, Peru 79 %, Filipíny 78 %, Polsko, Portugalsko, Portoriko, Katar, Rumunsko, Ruská federace 97 %, Rwanda 14 %, Réunion, Svatý Bartoloměj, Svatý Kryštof a Nevis 32 %, Svatá Lucie, Svatý Martin (francouzská část), San Marino, Svatý Tomáš a Princův ostrov 56 %, Saúdská Arábie, Senegal 49 %, Srbsko, Seychely, Sierra Leone 56 %, Singapur, Slovensko, Slovinsko, Jihoafrická republika, Jižní Súdán, Španělsko, Surinam 90 %, Svazijsko, Švédsko, Švýcarsko, Tchaj-wan, Sjednocená tanzanská republika 18 %, Thajsko, Nizozemsko, Togo 23 %, Trinidad a Tobago 2 %, Tunisko 98 %, Turecko 99 %, Uganda 12 %, Ukrajina, Spojené arabské emiráty, United Kingdom, Spojené státy americké, Uruguay 98 %, Venezuela 53 %, Vermont, Vietnam, Panenské ostrovy, USA, Jemen, Zambie 40 %, Zimbabwe 60 %, Vatikán Podrobné pokrytí dopravy Andorra, Rakousko, Belgie, Bulharsko, Chorvatsko, Česká republika, Dánsko, Estonsko, Finsko, Francie, Německo, Gibraltar, Řecko, Maďarsko, Island, Irsko, Itálie, Lotyšsko, Lichtenštejnsko, Litva, Lucembursko, Malta, Monako, Nizozemsko, Norsko, Polsko, Portugalsko, Rumunsko, Rusko, San Marino, Slovensko, Slovinsko, Španělsko, Švédsko, Švýcarsko, Turecko, Ukrajina, Spojené království, Vatikán, Kanada, Mexiko, Spojené státy americké, Brazílie, Chile, Kolumbie, Argentina, Peru, Uruguay, Mosambik, Egypt, Keňa, Lesotho, Maroko, Nigérie, Jižní Afrika, Brunej, Hongkong, Indonésie, Japonsko, Malajsie, Filipíny, Singapur, Tchaj-wan, Thajsko, Vietnam, Bahrajn, Izrael, Kuvajt, Omán, Katar, Saúdská Arábie, Spojené arabské emiráty, Austrálie, Nový Zéland Pokrytí rychlostních radarů Argentina, Austrálie, Rakousko, Belgie, Brazílie, Bulharsko, Kanada, Chile, Chorvatsko, Česká republika, Dánsko, Estonsko, Finsko, Řecko, Hongkong, Maďarsko, Indonésie, Irsko, Itálie, Lotyšsko, Litva, Lucembursko, Malajsie, Malta, Mexiko, Nový Zéland, Norsko, Polsko, Portugalsko, Rumunsko, Rusko, Srbsko, Singapur, Slovensko, Slovinsko, Španělsko, Švédsko, Thajsko, Nizozemsko, Ukrajina, United Kingdom, Spojené státy americké, Uruguay. Podporované jazyky Čeština, Bulharština, Katalánština, Chorvatština,Dánština, Holandština, Estonština, Finština, Francouzská, Němčina, Řečtina, Maďarština, Italština, Lotyština, Litevština, Norština, Polština, Portugalština, Slovenština, Slovinština, Jihoafrická angličtina, Španělština, Španělština (Latinská Amerika), Švédština, Turečtina, Britská angličtina, Americká angličtina Hlasové pokyny Čeština, Afrikánština, Arabština, Australská angličtina, Bulharština, Katalánština, Chorvatština, Dánština, Holandština, Holandština (Belgie), Finština, Francouzská, Němčina, Řečtina, Maďarština, Irská angličtina, Italština, Litevština, Novozélandská angličtina, Norština, Polština, Portugalština, Portugalština (Brazílie), Srbština, Slovinština, Španělština, Španělština (Latinská Amerika), Španělština (Argentina/latinská), Španělština (Chile), Švédština, Turečtina, Britská angličtina, Americká angličtina Technické specifikace Rozlišení displeje: 1280 x 720 pixelů (High Definition) Interní paměť: 32 GB Paměť RAM: 2 GB Wi-Fi: 2,4 GHz a 5 GHz Bluetooth (k příjmu služeb TomTom): Ano Hlasové ovládání: Ano Služby TomTom prostřednictvím smartphonu: Ano 3D budovy: Ano Rychlostní radary: ANo. 1 rok Obsah balení:
Ano, centrál. sklad
TP-Link TL-SG3428XPP-M2 JetStream 24-Port 2.5GBASE-T and 4-Port 10GE SFP+ L2+ Managed Switch witch 16-Port PoE+ and 8-Port PoE++ 2,5G PoE++/PoE+ porty pro WiFi 7/6E/6 : 24× 2,5 Gbps porty pokořují 2,5G bariéru a odemykají plný potenciál WiFi 7/6E/6 AP. 10G Lightning-Fast Uplink : 4× 10 Gbps SFP+ sloty umožňují širokopásmové připojení a neblokující přepínací kapacitu. 500 W PoE Budget : 8× 802.3bt/at/af/-kompatibilní PoE++ a 16× 802.3at/af-kompatibilní PoE+ porty s celkovým napájením 500 W. Integrováno do Omada SDN : Zero-Touch Provisioning (ZTP), centralizovaná správa cloudu a inteligentní monitorování. Centralizovaná správa : Přístup ke cloudu a aplikace Omada pro maximální pohodlí a snadnou správu. Static Routing : Pomáhá směrovat interní provoz pro efektivnější využití síťových zdrojů. Robustní bezpečnostní strategie : IP-MAC-Port Binding, ACL, Port Security, DoS Defend, Storm control, DHCP Snooping, 802.1X, Radius Authentication a další. Optimalizujte hlasové a video aplikace : L2/L3/L4 QoS a IGMP snooping. Learn more about TP-Link PoE technology > Learn more about TP-Link 10G Multi-Gig technology > Learn more about Omada Cloud SDN>? Stránky produktu : https://www.tp-link.com/uk/business-networking/poe-switch/tl-sg3428xpp-m2/ Technické specifikace HARDWARE FEATURES Interface • 24× 2.5 Gbps RJ45 Ports • 4× 10G SFP+ Slots • 1× RJ45 Console Port • 1× Micro-USB Console Port Fan Quantity 3 Power Supply 100-240 V AC~50/60 Hz PoE Ports (RJ45) • Standard: 802.3bt/at/af compliant • PoE++ Ports(802.3bt PoE): 8 Ports, up to 60 W per port • PoE+ Ports(802.3at PoE): 16 Ports, up to 30 W per port • Power Budget: 500 W Dimensions ( W x D x H ) 17.3 × 13.0 × 1.7 in (440 × 330 × 44 mm) Mounting Rack Mountable Max Power Consumption 629.1 W (110V/60Hz) Max Heat Dissipation 2153.45 BTU/h (110 V/60 Hz) PERFORMANCE Switching Capacity 200 Gbps Packet Forwarding Rate 148.80 Mpps MAC Address Table 32 K Packet Buffer Memory 16 Mbit Jumbo Frame 9 KB SOFTWARE FEATURES Quality of Service • 8 priority queues • 802.1p CoS/DSCP priority • Queue scheduling - SP (Strict Priority) - WRR (Weighted Round Robin) - SP+WRR • Bandwidth Control - Port/Flow based Rating Limiting • Smoother Performance • Action for Flows - Mirror (to supported interface) - Redirect (to supported interface) - Rate Limit - QoS Remark L2 and L2+ Features • Link Aggregation - static link aggregation - 802.3ad LACP - Up to 8 aggregation groups, containing 8 ports per group • Spanning Tree Protocol - 802.1d STP - 802.1w RSTP - 802.1s MSTP - STP Security: TC Protect, BPDU Filter, Root Protect • Loopback Detection - Port based - VLAN based • Flow Control - 802.3x Flow Control - HOL Blocking Prevention • Mirroring - Port Mirroring - CPU Mirroring - One-to-One - Many-to-One - Tx/Rx/Both L2 Multicast • IGMP Snooping - IGMP v1/v2/v3 Snooping - Fast Leave - IGMP Snooping Querier - IGMP Authentication • IGMP Authentication • MLD Snooping - MLD v1/v2 Snooping - Fast Leave - MLD Snooping Querier - Static Group Config - Limited IP Multicast • MVR • Multicast Filtering: 256 profiles and 16 entries per profile VLAN • VLAN Group - Max 4K VLAN Groups • 802.1Q Tagged VLAN • MAC VLAN: 256 Entries • Protocol VLAN: Protocol Template 16, Protocol VLAN 16 • GVRP • VLAN VPN (QinQ) - Port-Based QinQ - Selective QinQ • Voice VLAN Access Control List • Time-based ACL • MAC ACL - Source MAC - Destination MAC - VLAN ID - User Priority - Ether Type • IP ACL -Source IP - Destination IP - Fragment - IP Protocol - TCP Flag - TCP/UDP Port - DSCP/IP TOS - User Priority • Combined ACL • Packet Content ACL • IPv6 ACL • Policy - Mirroring - Redirect - Rate Limit - QoS Remark • ACL apply to Port/VLAN Security • IP-MAC-Port Binding - 512 Entries - DHCP Snooping - ARP Inspection - IPv4 Source Guard: 100 Entries • IPv6-MAC-Port Binding - 512 Entries - DHCPv6 Snooping - ND Detection - IPv6 Source Guard: 100 Entries • DoS Defend • Static/Dynamic Port Security - Up to 64 MAC addresses per port • Broadcast/Multicast/Unicast Storm Control - kbps/ratio control mode • 802.1X - Port base authentication - Mac base authentication - VLAN Assignment - MAB - Guest VLAN - Support Radius authentication andaccountability • AAA (including TACACS+) • Port Isolation • Secure web management through HTTPS with SSLv3/TLS 1.2 • Secure Command Line Interface (CLI) management with SSHv1/SSHv2 • IP/Port/MAC based access control IPv6 • IPv6 Dual IPv4/IPv6 • Multicast Listener Discovery (MLD) Snooping • IPv6 ACL • IPv6 Interface • Static IPv6 Routing • IPv6 neighbor discovery (ND) • Path maximum transmission unit (MTU) discovery • Internet Control Message Protocol (ICMP) version 6 • TCPv6/UDPv6 • IPv6 applications - DHCPv6 Client - Ping6 - Tracert6 - Telnet (v6) - IPv6 SNMP - IPv6 SSH - IPv6 SSL - Http/Https - IPv6 TFTP L3 Features • 32 IPv4/IPv6 Interfaces • Static Routing - 48 static routes • Static ARP - 128 Static Entries • Proxy ARP • Gratuitous ARP • DHCP Server • DHCP Relay - DHCP Interface Relay - DHCP VLAN Relay • DHCP L2 Relay Advanced Features • Automatic Device Discovery • Batch Configuration • Batch Firmware Upgrading • Intelligent Network Monitoring • Abnormal Event Warnings • Unified Configuration • Reboot Schedule MIBs • MIB II (RFC1213) • Interface MIB (RFC2233) • Ethernet Interface MIB (RFC1643) • Bridge MIB (RFC1493) • P/Q-Bridge MIB (RFC2674) • RMON MIB (RFC2819) • RMON2 MIB (RFC2021) • Radius Accounting Client MIB (RFC2620) • Radius Authentication Client MIB (RFC2618) • Remote Ping, Traceroute MIB (RFC2925) • Support TP-Link private MIB MANAGEMENT Omada App Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Centralized Management • Omada Cloud-Based Controller • Omada Hardware Controller (OC300) • Omada Hardware Controller (OC200) • Omada Software Controller Cloud Access Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Zero-Touch Provisioning Yes. Requiring the use of Omada Cloud-Based Controller. Management Features • Web-based GUI • Command Line Interface (CLI) through the console port, telnet • SNMP v1/v2c/v3 - Trap/Inform - RMON (1,2,3,9 groups) • SDM Template • DHCP/BOOTP Client • 802.1ab LLDP/LLDP-MED • DHCP AutoInstall • Dual Image, Dual Configuration • CPU Monitoring • Cable Diagnostics • EEE • Password Recovery • SNTP • System Log OTHERS Certification CE, FCC, RoHS Package Contents • TL-SG3428XPP-M2 Switch • Power Cord • Quick Installation Guide • Rackmount Kit • Rubber Feet System Requirements Microsoft Windows 98SE, NT, 2000, XP, Vista™ or Windows 7/8/10/11, MAC OS, NetWare, UNIX or Linux. Environment • Operating Temperature: 0–40 °C (32–104 °F); • Storage Temperature: -40–70 °C (-40–158 °F) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% RH non-condensing
Skladem v eshopu

MikroTik G1483-0600WNB; Interní napájecí hot-swap zdroj pro PoE++ switch MikroTik CRS320-8P-8B-4S+RM . ZÁKLADNÍ SPECIFIKACE; Výkon: 600 W; Výstupní napětí: 54,5 V;...
Ano, centrál. sklad

Zboží má rozbalený obal. Z tohoto důvodu je poskytnuta sleva. Produkt je nepoškozený, plně funkční a s plnou zárukou. Směrovač TP-LINK M7350 je špičkové zařízení pro sdílení v bezdrátových 4G sítích. Stačí vložit 4G SIM kartu do zařízení a okamžitě vytvořit volitelný dvoupásmový Wi-Fi hotspot. Hlavní přednosti Podporuje 4G LTE - rychlost stahování až 150 Mbit/s a uploadu 50 Mbit/s Podporuje až 15 zařízení současně Veškeré užitečné informace se zobrazí v přehledu na displeji Baterie s kapacitou 2550 mAh vydrží až 10 hodin provozu Možnost volby pásma Wi-Fi 2,4 GHz nebo 5 GHz Vybaven slotem na micro SD kartu s volitelnou kapacitou až 32 GB Vysoká rychlost a kapesní design Směrovač M7350 dokáže díky rychlosti stahování 150 Mbit/s a uploadování 50 Mbit/s poskytnout možnost sdílení v 4G síti až 15 uživatelům najednou . Díky jeho kapesní velikosti a výkonné interní baterii s kapacitou 2550 mAh se z něj stává ideální zařízení na cesty, kdy uživatelům umožní 10 hodin práce či hraní. Je vybavený inovativním TFT displejem , takže uživatelé získají mnohem intuitivněji informace o provozním stavu zařízení, jako např. o síle signálu, typu sítě (4G/3G/2G), dostupnosti Wi-Fi, zprávách, internetu, statistikách provozu a stavu baterie Specifikace Značka: TP-Link Model: M7350 Určení: modem Network Type: FDD-LTE Cat4 (800/900/1800/2100/2600MHz), DC-HSPA+/HSPA/UMTS (900/2100MHz), EDGE/GPRS/GSM (850/900/1800/1900MHz) Tlačítko: Power On/Off tlačítko, Menu tlačítko Anténa: Internal Antenna Přenosové rychlosti DL: 150Mbps, UL: 50Mbps Napájení: interní 2550mAh dobíjení baterka Čtečka karet: až 32 GB Informace na displeji: Traffic statistics, Wi-Fi status, user numbers, network type (2G/3G/4G), signal strength, Internet connection status, messages, battery meter Certifikace: CE, RoHS Systémové požadavky: Windows 8/7/vista/XP, Mac OS, Android, iOS, Windows Phone Funkce bezdrátové sítě Standardy bezdrátové sítě: IEEE 802.11a, IEEE 802.11b, IEEE 802.11g, IEEE 802.11n Frekvence: 2.4GHz & 5GHz EIRP: <20dBm Zabezpečení bezdrátové sítě: Support WPA-PSK/WPA2-PSK,Wireless MAC Filtering, Enable/Disable SSID Broadcast DHCP: DHCP server, DHCP Client List Rozhraní 1 micro USB port for power supply SIM card slot Micro SD card slot Fyzické parametry Barva: černá Rozměry (š x v x h): 106 x 16 x 66 mm Obsah balení 1x modem 1x Micro USB kabel 1x Micro to Standard SIM Card Adaptér 1x Nano to Standard SIM Card Adaptér 1x síťový adaptér 1x návod
Skladem, dodání 2-4 dní
Modem: Kabel Počet Gigabit-Portů: 4 WAN-Port: ano USB: USB-A 2.0 Typ: Síťový router s modemem Max. přenosová rychlost (Mbit/Sek.): 2880 + 720
3-5 dní dostupné

Router ZTE MF79N USB modem LTE CAT.4 Přenosová rychlost sítě Ethernet: 1001000 Mbit/s10 Typ rozhraní ethernetu LAN: Gigabit Ethernet Aktivace portů: Ano VPN Passthrough: Ano Připojení na síť Ethernet:
Dodání 3 dny
Cisco Catalyst switch C1200-8P-E-2G Sada pro montáž do racku není součástí balení. Řada Cisco Catalyst 1200 je další generací cenově dostupných chytrých přepínačů, které kombinují vysoký výkon a spolehlivost s kompletní sadou funkcí, které potřebujete pro malé a středně velké podnikové sítě. Přepínače fungují na přizpůsobeném softwaru operačního systému Linux a poskytují flexibilní možnosti správy, komplexní možnosti zabezpečení a funkce statického směrování na 3. vrstvě, které daleko přesahují možnosti neřízeného nebo levného přepínače a to za nižší cenu než u plně spravovaných přepínačů. Když potřebujete spolehlivé řešení pro sdílení online zdrojů a připojení počítačů, telefonů a bezdrátových přístupových bodů, chytré přepínače Catalyst řady 1200 poskytují ideální řešení za dostupnou cenu. Stránky produktu: C1200-8P-E-2G Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 14,88 Switching capacity in gigabits per second (Gbps) 20 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 4 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG) VLAN Support for up to 255 active VLANs simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Auto Surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Enable automatically propagation and configuration of VLANs in a bridged domain Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping Limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported) IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 routing IPv4 routing Wire-speed routing of IPv4 packets Up to 32 static routes and up to 16 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets Security Secure Sockets Layer (SSL) Encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch SSH Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported. IEEE 802.1X (authenticator role) RADIUS authentication, guest VLAN, single/multiple host mode, and single/multiple sessions STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices and a secure auto-configuration. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC]) Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses RADIUS Supports RADIUS authentication for management access. Switch functions as a client Storm control Broadcast, multicast, and unknown unicast DoS prevention DoS attack prevention Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels ACLs Support for up to 512 rules Drop or rate limit based on source and destination MAC, VLAN ID, IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides Time-based ACLs supported Quality of service Priority levels 8 hardware queues Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and Class of Service (802.1p/CoS) Class of service Port based, 802.1p VLAN priority based, IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based, Differentiated Services (DiffServ), classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer, egress shaping and rate control per VLAN, per port, and flow based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.3 ad LACP, IEEE 802.1D (STP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, RFC 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 920, RFC 922, RFC 950, RFC 951, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1213, RFC 1215, RFC 1286, RFC 1350, RFC 1442, RFC 1451, RFC 1493, RFC 1533, RFC 1541, RFC 1542, RFC 1573, RFC 1624, RFC 1643, RFC 1700, RFC 1757, RFC 1867, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2030, RFC 2131, RFC 2132, RFC 2233, RFC 2576, RFC 2616, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 3416, RFC 4330 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet Dual IPv6/IPv4 stack IPv6 Neighbor Discovery (ND) IPv6 stateless address auto-configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) ICMP version 6 IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) support IPv6 QoS Prioritizes IPv6 packets in hardware IPv6 ACL Drop or rate-limit IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) snooping Delivers IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, Ping, Traceroute, Simple Network
Ano, centrál. sklad

Wi-Fi router, Wi-Fi 6 a podpora PoE+, dvoupásmové připojení (v pásmu 5 GHz rychlost až 1 201 Mbps, 2,4 GHz až 574 Mbps), krytí IP67, technologie Omada Mesh, centralizovaná správa v Omada SDN. Montáž na sloup/zeď.
Skladem v eshopu

20 x Aruba Instant On 1930 24G Class4 PoE 4SFP/SFP+ 370W Switch ( 20 pack ) I/O Ports and Slots 24 RJ-45 autosensing 10/100/1000 Class 4 PoE ports (IEEE 802.3 Type 10BASE-T, IEEE 802.3u Type 100BASE- TX, IEEE 802.3ab Type 1000BASE-T); Duplex: 10BASE-T/100BASE-TX: half or full; 1000BASE-T: full only 4 SFP+ 1/10GbE ports Physical Characteristics Dimensions 17.42(w) x 10.42(d) x 1.73(h) in (44.25 x 26.47 x 4.39 cm) (1U height) Weight 8.23 lb (3.73 kg) Processor and Memory ARM Cortex-A9 @ 800 MHz, 512 MB SDRAM, 256 MB flash; packet buffer: 1.5 MB Memory And Flash 512 MB SDRAM 256 MB flash Packet Buffer 1.5 MB Performance 100 Mb latency < 4.7 uSec 1000 Mb latency <2.4 uSec 10000 Mb latency <1.3 uSec Throughput (Mpps) 95.23 Mpps Capacity 128 Gbps Routing table size (# of static entries) 32 MAC address table size (# of entries) 16,000 Reliability MTBF (years) 71 Environment Operating temperature 32°F to 104°F (0°C to 40°C) Operating relative humidity 15% to 95% @ 104°F (40°C) Non-operating temperature -40°F to 158°F (-40°C to 70°C) Non-operating relative humidity 15% to 95% @ 140°F (60°C) Altitude Up to 10,000ft (3.048 Km) Acoustic 1 LWAd = 4.0 Bel LpAm (Bystander) = 24 dB Notes: 1 Acoustics measured in 23°C semi-anechoic chamber with a loading of 100% traffic and 50% PoE on all ports. Measured in accordance with ISO 7779. Declared in accordance with ECMA-109:2010. Values presented are the Declared A-Weighted Sound Power Level (LWAd) and the mean Bystander A-Weighted Sound Pressure Level (LpAm) Electrical Characteristics Frequency 50-60 Hz AC voltage 100 - 127 / 200 - 240 VAC Current 4.9 A/2.4 A Maximum power rating 440.4W Idle power 20.3W PoE power 370 W Class 4 PoE Power supply Internal power supply Safety UL 60950-1; IEC 60950-1;EN 60950-1; CAN/CSA-C22.2 No. 60950-1; EN 60825-1 UL 62368-1 Ed. 2; IEC 62368-1 Ed. 2; EN 62368-1:2014 Emissions VCCI-CISPR 32, Class A; CNS 13438; ICES-003 Issue 6 Class A; FCC CFR 47 Part 15, Class A; EN 55032: 2015 +AC:2016 / CISPR-32, Class A Immunity Generic CISPR 24 / CISPR 35 EN EN 55024:2010 / EN 55035:2017 ESD IEC 61000-4-2 Radiated IEC 61000-4-3 EFT/Burst IEC 61000-4-4 Surge IEC 61000-4-5 Conducted IEC 61000-4-6 Power frequency magnetic field IEC 61000-4-8 Voltage dips and interruptions IEC 61000-4-11 Harmonics IEC 61000-3-2, EN 61000-3-2 Flicker IEC 61000-3-3, EN 61000-3-3 Device Management Aruba Instant On Cloud; Web browser; SNMP Manager Mounting Mounts in an EIAstandard 19 in. telco rack or equipment cabinet. 2-post rack kit included Supports table-top mounting Supports rackmounting Supports wall-mounting with ports facing either up or down Supports under-table mounting using the brackets provided Transceivers Aruba Instant On 1G SFP LC SX 500m OM2 MMF Transceiver (R9D16A) Aruba 1G SFP LC LX 10km SMF Transceiver (J4859D) Aruba Instant On 1G SFP RJ45 T 100m Cat5e Transceiver (R9D17A) Aruba Instant On 10G SFP+ LC SR 300m OM3 MMF Transceiver (R9D18A) Aruba 10G SFP+ LC LR 10km SMF Transceiver (J9151E)
Ano, centrál. sklad
Cisco Catalyst switch C1200-16T-2G Sada pro montáž do racku není součástí balení. Řada Cisco Catalyst 1200 je další generací cenově dostupných chytrých přepínačů, které kombinují vysoký výkon a spolehlivost s kompletní sadou funkcí, které potřebujete pro malé a středně velké podnikové sítě. Přepínače fungují na přizpůsobeném softwaru operačního systému Linux a poskytují flexibilní možnosti správy, komplexní možnosti zabezpečení a funkce statického směrování na 3. vrstvě, které daleko přesahují možnosti neřízeného nebo levného přepínače a to za nižší cenu než u plně spravovaných přepínačů. Když potřebujete spolehlivé řešení pro sdílení online zdrojů a připojení počítačů, telefonů a bezdrátových přístupových bodů, chytré přepínače Catalyst řady 1200 poskytují ideální řešení za dostupnou cenu. Stránky produktu: C1200-16T-2G Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 26,78 Switching capacity in gigabits per second (Gbps) 36 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 4 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad Link Aggregation Group (LAG) VLAN Support for up to 255 active VLANs simultaneously Port-based and 802.1Q tag-based VLANs Management VLAN Guest VLAN Auto Surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) Enable automatically propagation and configuration of VLANs in a bridged domain Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping Limits bandwidth-intensive multicast traffic to only the requesters; supports 255 multicast groups (source-specific multicasting is also supported) IGMP querier Used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 routing IPv4 routing Wire-speed routing of IPv4 packets Up to 32 static routes and up to 16 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of Layer 3 interface on physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Dynamic Host Configuration Protocol (DHCP) relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BootP)/DHCP packets Security Secure Sockets Layer (SSL) Encrypts all HTTPS traffic, allowing secure access to the browser-based management GUI in the switch SSH Protocol SSH is a secure replacement for Telnet traffic. Secure Copy (SCP) also uses SSH. SSH v1 and v2 are supported. IEEE 802.1X (authenticator role) RADIUS authentication, guest VLAN, single/multiple host mode, and single/multiple sessions STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) Secure Core Technology (SCT) Ensures that the switch will receive and process management and protocol traffic no matter how much traffic is received Secure Sensitive Data (SSD) A mechanism to manage sensitive data (such as passwords, keys, and so on) securely on the switch, populating this data to other devices and a secure auto-configuration. Access to view the sensitive data as plain text or encrypted is provided according to the user-configured access level and the access method of the user Trustworthy systems Trustworthy systems provide a highly secure foundation for Cisco products Run-time defenses (Executable Space Protection [X-Space], Address Space Layout Randomization [ASLR], Built-In Object Size Checking [BOSC]) Port security Ability to lock source MAC addresses to ports and limit the number of learned MAC addresses RADIUS Supports RADIUS authentication for management access. Switch functions as a client Storm control Broadcast, multicast, and unknown unicast DoS prevention DoS attack prevention Multiple user privilege levels in CLI Level 1, 7, and 15 privilege levels ACLs Support for up to 512 rules Drop or rate limit based on source and destination MAC, VLAN ID, IPv4 or IPv6 address, IPv6 flow label, protocol, port, Differentiated Services Code Point (DSCP)/IP precedence, TCP/UDP source and destination ports, 802.1p priority, Ethernet type, Internet Control Message Protocol (ICMP) packets, IGMP packets, TCP flag; ACL can be applied on both ingress and egress sides Time-based ACLs supported Quality of service Priority levels 8 hardware queues Scheduling Strict priority and Weighted Round-Robin (WRR) queue assignment based on DSCP and Class of Service (802.1p/CoS) Class of service Port based, 802.1p VLAN priority based, IPv4/v6 IP precedence/Type of Service (ToS)/DSCP based, Differentiated Services (DiffServ), classification and re-marking ACLs, trusted QoS Rate limiting Ingress policer, egress shaping and rate control per VLAN, per port, and flow based Congestion avoidance A TCP congestion avoidance algorithm is required to reduce and prevent global TCP loss synchronization Standards Standards IEEE 802.3 10BASE-T Ethernet, IEEE 802.3u 100BASE-TX Fast Ethernet, IEEE 802.3ab 1000BASE-T Gigabit Ethernet, IEEE 802.3ad Link Aggregation Control Protocol, IEEE 802.3z Gigabit Ethernet, IEEE 802.3x Flow Control, IEEE 802.3 ad LACP, IEEE 802.1D (STP), IEEE 802.1Q/p VLAN, IEEE 802.1w RSTP, IEEE 802.1s Multiple STP, IEEE 802.1X Port Access Authentication, IEEE 802.3af, IEEE 802.3at, RFC 768, RFC 783, RFC 791, RFC 792, RFC 793, RFC 813, RFC 879, RFC 896, RFC 826, RFC 854, RFC 855, RFC 856, RFC 858, RFC 894, RFC 919, RFC 920, RFC 922, RFC 950, RFC 951, RFC 1042, RFC 1071, RFC 1123, RFC 1141, RFC 1155, RFC 1157, RFC 1213, RFC 1215, RFC 1286, RFC 1350, RFC 1442, RFC 1451, RFC 1493, RFC 1533, RFC 1541, RFC 1542, RFC 1573, RFC 1624, RFC 1643, RFC 1700, RFC 1757, RFC 1867, RFC 1907, RFC 2011, RFC 2012, RFC 2013, RFC 2030, RFC 2131, RFC 2132, RFC 2233, RFC 2576, RFC 2616, RFC 2618, RFC 2665, RFC 2666, RFC 2674, RFC 2737, RFC 2819, RFC 2863, RFC 3164, RFC 3411, RFC 3412, RFC 3413, RFC 3414, RFC 3415, RFC 3416, RFC 4330 IPv6 IPv6 IPv6 host mode IPv6 over Ethernet Dual IPv6/IPv4 stack IPv6 Neighbor Discovery (ND) IPv6 stateless address auto-configuration Path Maximum Transmission Unit (MTU) discovery Duplicate Address Detection (DAD) ICMP version 6 IPv6 over IPv4 network with Intrasite Automatic Tunnel Addressing Protocol (ISATAP) support IPv6 QoS Prioritizes IPv6 packets in hardware IPv6 ACL Drop or rate-limit IPv6 packets in hardware Multicast Listener Discovery (MLD v1/2) snooping Delivers IPv6 multicast packets only to the required receivers IPv6 applications Web/SSL, Telnet server/SSH, Ping, Traceroute, Simple Network Ti
Ano, centrál. sklad

Mikrotik ATLGM&EG18-EA zesilovač mobilního signálu Zesilovač mobilního signálu na ven Bílá Typ SIM karty: MicroSIM Model procesoru: 88F3720 Počet jader procesoru: 2 Vnitřní paměť: 256 MB Barva: Bílá P
Dodání 3 dny
Ubiquiti U7 Pro Wall je velice výkonná triple-band jednotka s podporou Wi-Fi 7. Pracuje v pásmu 2,4 GHz o rychlosti 688 Mb/s, v pásmu 5 GHz o rychlosti 4,3 Gb/s, v pásmu 6 GHz, dokonce 5,7 Gb/s. Díky triple bandu zaručuje jednotka opravdu velmi dobré přip
Ano, centrál. sklad

Rack Mount rámeček pro CISCO Catalyst 1200 a 1300 (8,12 a 16 portů) Vyžadován pouze pro 8, 12 a 16 portové switche C1200 a C1300. Modely s 24 a 48 porty obsahují rámeček v balení!
Ano, centrál. sklad
Cisco Catalyst switch C1200-24P-4X (24xGbE,4xSFP+,24xPoE+,195W,fanless)
Dodání 3-5 dní

ASUS ExpertWiFi EBG15 Kabelový router Gigabit VPN, až 3 ethernetové porty WAN + 1 USB WAN, prevence narušení IPS, firewall na 7. vrstvě, zabezpečení sítě na komerční úrovni, snadná centralizovaná správa Aplikace ExpertWiFi Nastavení snadnější než kdy jindy — Pohodlná a snadná správa routeru prostřednictvím webového prohlížeče nebo mobilní aplikace ASUS ExpertWiFi prostřednictvím nastavení Bluetooth. VLAN pro přidané zabezpečení – Každý z ethernetových portů lze přiřadit k jednomu nebo více VLAN ID, které poskytuje dodatečné zabezpečení vaší firmy. Až 3 porty WAN Ethernet – 1 gigabitový port WAN a 2 gigabitové porty WAN/LAN s vyrovnáváním zátěže optimalizují vícelinkové širokopásmové využití. Záložní WAN pro stabilní konektivitu – USB port lze použít jako záložní WAN připojením k mobilnímu telefonu s hotspotem pro udržení spolehlivého internetového připojení. Zabezpečení sítě na komerční úrovni a VPN — Zabezpečte veřejná WiFi připojení pomocí funkcí Bezpečné prohlížení a VPN. Užijte si bezplatné předplatné ASUS AiProtection Pro, včetně robustních funkcí systému prevence narušení (IPS), jako je hloubková kontrola paketů (DPI) a virtuální opravy pro blokování škodlivého provozu. Specifikace Technické Specifikace Síťový standard Bluetooth 3.0 Bluetooth 3.2 IEEE 802.1p IEEE 802.1q IEEE 802.3 IEEE 802.3ab IEEE 802.3i IEEE 802.3u IEEE 802.3x IPv4 IPv6 Anténa 1x Interní Bluetooth anténa Procesor 1.8GHz 2-jádrový ARMv8 Paměť 256 MB Flash 512 MB RAM Konektory 1x Gigabit WAN Port 4x Gigabit LAN Port (2x Vyměnitelné WAN/LAN Port) 1x USB 3.2 Gen 1 Napájení AC Vstup: 110V~240V (50~60Hz) DC Výstup: 12 V s max. 1.5 A proudem Rozměry a váha Rozměry 121 x 75 x 26 mm Váha 250 g Co je v krabici 1x RJ-45 Kabel Napájecí kabel
Dodání 3-5 dní

Cisco switch CBS350-48FP-4X-EU - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Řízené switche řady Cisco Business 350 jsou spolehlivými stavebními prvky pro sítě malých firem. Díky intuitivnímu ovládacímu panelu, pokročilým funkcím a všudypřítomnému zabezpečení urychlují spravované switche řady Cisco Business 350 vaši digitální transformaci. Záruka platná do End of Support 31. 10. 2029. Oznámení End of Life pro CISCO CBS350 Stránky produktu: CBS350-48FP-4X-EU Quick start guide: Quick start guide Switching capacity and forwarding rate (All switches are wire speed and nonblocking) Capacity in Millions of Packets per Second (mpps) (64-byte packets) 130,94 Switching Capacity in Gigabits per Second (Gbps) 176 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d Spanning Tree support Fast convergence using 802.1w (Rapid Spanning Tree [RSTP]), enabled by default Multiple Spanning Tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+) and Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4,094 VLANs simultaneously Port-based and 802.1Q tag-based VLANs; MAC-based VLAN; protocol-based VLAN; IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1x client authentication CPE VLAN Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers network wide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN Translation Support for VLAN One-to-One Mapping. In VLAN One-to-One Mapping, on an edge interface customer VLANs (C-VLANs) are mapped to service provider VLANs (S-VLANs) and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) Generic VLAN Registration Protocol (GVRP) and Generic Attribute Registration Protocol (GARP) enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link Detection (UDLD) UDLD monitors physical connection to detect unidirectional links caused by incorrect wiring or cable/port faults to prevent forwarding loops and black holing of traffic in switched networks Dynamic Host Configuration Protocol (DHCP) Relay at Layer 2 Relay of DHCP traffic to DHCP server in different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; supports 2K multicast groups (source-specific multicasting is also supported) IGMP Querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols. Head-of-Line (HOL) blocking HOL blocking prevention Loopback Detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wirespeed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wirespeed routing of IPv6 packets Layer 3 Interface Configuration of Layer 3 interface on physical port, Link Aggregation (LAG), VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for classless interdomain routing RIP v2 Support for Routing Information Protocol version 2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to different next hop based on IPv4 or IPv6 Access Control List (ACL) DHCP Server Switch functions as an IPv4 DHCP server serving IP addresses for multiple DHCP pools/scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Stacking Hardware stacking Up to 4 units in a stack. Up to 200 ports managed as a single system with hardware failover High availability Fast stack failover delivers minimal traffic loss. Support link aggregation across multiple units in a stack Plug-and-play stacking configuration/management Active/standby for resilient stack control Autonumbering Hot swap of units in stack Ring and chain stacking options, auto stacking port speed, flexible stacking port options High-speed stack interconnects Cost-effective high-speed 10G fiber interfaces. Security ecure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (Authenticator role) 802.1X: Remote Authentication Dial-In User Service (RADIUS) authentication and accounting, MD5 hash; guest VLAN; unauthenticated VLAN, single/multiple host mode and single/multiple sessions Supports time-based 802.1X; dynamic VLAN assignment; MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard This prevents edge devices not in the network administrator’s control from becoming Spanning Tree Protocol root nodes STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) DHCP snooping Filters out DHCP messages with unregistered IP addresses and/or from unexpected or untrusted interfaces. This prevents rogue devices from behaving as DHCP Servers. IP Source Guard (IPSG) When IP Source Guard is enabled at a port, the switch filters out IP packets received from the port if the source IP addresses of the packets have not been statically configured or dynamically learned from DHCP
Ano, centrál. sklad
Cisco Catalyst switch C1300-48P-4X Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu. Stránky produktu: C1300-48P-4X Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 130.94 Switching capacity in gigabits per second (Gbps) 176.0 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4093 VLANs simultaneously Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN Auto surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported) IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wire-speed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Stacking Hardware stacking Up to 8 switches in a stack. Up to 200 ports managed as a single system with hardware failover Stacking is supported on the following models: Family 1: C1300-16P-4X, C1300-24T-4X, C1300-24P-4X, C1300-24FP-4X, C1300-48T-4X, C1300-48P-4X, C1300-48FP-4X, C1300-8MGP-2X, C1300-24MGP-4X, C1300-48MGP-4X Family 2: C1300-12XT-2X, C1300-12XS, C1300-16XTS, C1300-24XS, C1300-24XT, C1300-24XTS PIDs from the same Family can be stacked together. Cross-stacking between Families is not supported. High availability Fast stack failover delivers minimal traffic loss. Support for LAG across multiple units in a stack Plug-and-play stacking configuration/management Active/standby for resilient stack control Auto-numbering Hot swap of units in stack Ring and chain stacking options, auto stacking port speed, flexible stacking port options High-speed stack interconnects Cost-effective high-speed 10 Gigabit Ethernet fiber interfaces Security Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through a web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard Prevents edge devices not in the network administrator’s control from becoming STP root nodes STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) D
Ano, centrál. sklad
Popis produktu Nový Mikrotik RouterBOARD L23UGSR-5HaxD2HaxD je dual-band WiFi6 RouterBOARD pomocí, kterého si můžete vytvořit své vlastní instalace. Můžete ho použít k vytvoření vlastních low-cost venkovních přístupových bodů nebo CPE, pro jakékoliv domácí či kancelářské připojení nebo ho můžete využít pro osazení vašeho vlastního produktu, jako jsou např. chytré prodejní automaty či jako IoT gateway. Výhodou řešení Mikrotik RouterBOARD je, že je vybaven RouterOS s licencí L4 a neobsahuje žádné další měsíční či licenční poplatky, zakoupíte a používáte. RouterBOARD L23UGSR-5HaxD2HaxD je vybaven 1x1G ETH portem, 2.5G SFP portem a USB portem. Pro připojení antén jsou na RouterBOARDU umístěny 4x MMCX konektory. Dále obsahuje volný miniPCIe slot se SIM slotem pro osazení LTE modemu nebo LoRA karty, můžete tak vytvořit záložní mobilní připojení nebo IoT bránu. Technické parametry Bezdrátové vlastnosti Bezdrátové frekvence:2.4 + 5 GHz (dual band) WiFi standardy:802.11n, 802.11a, 802.11ac, 802.11b/g, 802.11ax Přenosová rychlost - 5GHz [Mb/s]:2402 Přenosová rychlost - 2.4GHz [Mb/s]:574 2.4GHz MIMO:2 x 2 5GHz MIMO:2 x 2 Konektory a rozhraní VF konektory:(4) MMCX Rychlost LAN:(1) 10/100/1000Mbps Gigabit LAN:Ano Optické rozhraní:(1) 1G/2.5Gbps Počet miniPCI-e slotů:1 Slot na SIM kartu:Ano Počet SIM slotů:1 USB:Ano Napájení Napájení přes PoE:18 .. 28V DC Typ napájení:DC konektor, PoE Typy PoE:PoE-In (pouze) Max. spotřeba energie [W]:12 Napájení přes konektor/svorkovnici:12 .. 28V DC Fyzické charakteristiky Provedení:RouterBOARD Provozní teplota [°C]:-40 až 70 Hardware CPU:IPQ-5010 Frekvence CPU [MHz]:800 Počet CPU jader:2 Interní uložiště [MB]:128 RAM [MB]:256 Software Operační systém:RouterOS - L4 Výchozí IP adresa:192.168.88.1 Výchozí jméno a heslo:admin / -
Ano, centrál. sklad

DN-651149 je odolný 4+2portový průmyslový Gigabit Ethernet PoE switch pro drsná prostředí. Nabízí neblokující rychlost drátu. 4x 10/100/1000 BASE-TX RJ45 (každý až 30 W PoE) + 2x 1000Base-Fx porty. Kryt IP40 s redundantním napájením je ideální pro monitor
Skladem v eshopu
Cisco Catalyst switch C1300-24XTS - REFRESH CISCO REFRESH jsou repasované produkty, které společnost CISCO dodává s certifikací kvality, zárukou a servisní podporou odpovídající ekvivalentnímu novému produktu Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu. Stránky produktu: C1300-24XTS Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 357.12 Switching capacity in gigabits per second (Gbps) 480 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4093 VLANs simultaneously Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN Auto surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported) IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wire-speed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Stacking Hardware stacking Up to 8 switches in a stack. Up to 200 ports managed as a single system with hardware failover Stacking is supported on the following models: Family 1: C1300-16P-4X, C1300-24T-4X, C1300-24P-4X, C1300-24FP-4X, C1300-48T-4X, C1300-48P-4X, C1300-48FP-4X, C1300-8MGP-2X, C1300-24MGP-4X, C1300-48MGP-4X Family 2: C1300-12XT-2X, C1300-12XS, C1300-16XTS, C1300-24XS, C1300-24XT, C1300-24XTS PIDs from the same Family can be stacked together. Cross-stacking between Families is not supported. High availability Fast stack failover delivers minimal traffic loss. Support for LAG across multiple units in a stack Plug-and-play stacking configuration/management Active/standby for resilient stack control Auto-numbering Hot swap of units in stack Ring and chain stacking options, auto stacking port speed, flexible stacking port options High-speed stack interconnects Cost-effective high-speed 10 Gigabit Ethernet fiber interfaces Security Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through a web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard Prevents edge devices not i
Ano, centrál. sklad
Cisco Catalyst switch C1300-48T-4X Cisco Catalyst řady 1300 jsou managovatelné switche Gigabit Ethernet Layer 3 podnikové třídy určené pro malé a střední podniky a pobočky. Tyto jednoduché, flexibilní a bezpečné switche jsou ideální pro nasazení mimo rozvodnou skříň. Řada Catalyst 1300 pracuje na přizpůsobeném softwaru operačního systému Linux s intuitivním grafickým rozhraním, který zjednodušuje nastavení sítě a pokročilými funkcemi, které urychlují digitální transformaci, zatímco všudypřítomné zabezpečení chrání kritické obchodní transakce. Přepínače řady 1300 poskytují ideální kombinaci cenové dostupnosti a možností pro malé a střední podniky a pomáhají vám vytvořit efektivnější a lépe propojenou pracovní sílu. Stránky produktu: C1300-48T-4X Performance Switching capacity and forwarding rate (All switches are wire-speed and nonblocking) Capacity in millions of packets per second (mpps) (64-byte packets) 130.94 Switching capacity in gigabits per second (Gbps) 176.0 Layer 2 switching Spanning Tree Protocol (STP) Standard 802.1d spanning tree support Fast convergence using 802.1w (Rapid Spanning Tree Protocol [RSTP]), enabled by default Multiple spanning tree instances using 802.1s (MSTP); 8 instances are supported Per-VLAN Spanning Tree Plus (PVST+); 126 instances are supported Rapid PVST+ (RPVST+); 126 instances are supported Port grouping/link aggregation Support for IEEE 802.3ad Link Aggregation Control Protocol (LACP) Up to 8 groups Up to 8 ports per group with 16 candidate ports for each (dynamic) 802.3ad link aggregation VLAN Support for up to 4093 VLANs simultaneously Port-based and 802.1Q tag-based VLANs, MAC-based VLAN, protocol-based VLAN, IP subnet-based VLAN Management VLAN Private VLAN with promiscuous, isolated, and community port Private VLAN Edge (PVE), also known as protected ports, with multiple uplinks Guest VLAN, unauthenticated VLAN Dynamic VLAN assignment via RADIUS server along with 802.1X client authentication Customer premises equipment (CPE) VLAN Auto surveillance VLAN (ASV) Voice VLAN Voice traffic is automatically assigned to a voice-specific VLAN and treated with appropriate levels of QoS. Voice Services Discovery Protocol (VSDP) delivers networkwide zero-touch deployment of voice endpoints and call control devices Multicast TV VLAN Multicast TV VLAN allows the single multicast VLAN to be shared in the network while subscribers remain in separate VLANs. This feature is also known as Multicast VLAN Registration (MVR) VLAN translation Support for VLAN one-to-one mapping, in which customer VLANs (C-VLANs) on an edge interface are mapped to service provider VLANs (S-VLANs), and the original C-VLAN tags are replaced by the specified S-VLAN Q-in-Q VLANs transparently cross a service provider network while isolating traffic among customers Selective Q-in-Q Selective Q-in-Q is an enhancement to the basic Q-in-Q feature and provides, per edge interface, multiple mappings of different C-VLANs to separate S-VLANs Selective Q-in-Q also allows configuring of the Ethertype (Tag Protocol Identifier [TPID]) of the S-VLAN tag Layer 2 protocol tunneling over Q-in-Q is also supported Generic VLAN Registration Protocol (GVRP)/Generic Attribute Registration Protocol (GARP) GVRP and GARP enable automatic propagation and configuration of VLANs in a bridged domain Unidirectional Link UDLD monitors physical connections to detect unidirectional links caused by incorrect Detection (UDLD) wiring or cable/port faults to prevent forwarding loops and blackholing of traffic in switched networks DHCP relay at Layer 2 Relay of DHCP traffic to a DHCP server in a different VLAN; works with DHCP Option 82 Internet Group Management Protocol (IGMP) versions 1, 2, and 3 snooping IGMP limits bandwidth-intensive multicast traffic to only the requesters; it supports 2000 multicast groups (source-specific multicasting is also supported) IGMP querier IGMP querier is used to support a Layer 2 multicast domain of snooping switches in the absence of a multicast router IGMP proxy The IGMP proxy provides a mechanism for multicast forwarding based on IGMP membership information without the need for more complicated multicast routing protocols Head-of-Line (HOL) blocking HOL blocking prevention Loopback detection Loopback detection provides protection against loops by transmitting loop protocol packets out of ports on which loop protection has been enabled. It operates independently of STP Layer 3 IPv4 routing Wire-speed routing of IPv4 packets Up to 990 static routes and up to 128 IP interfaces IPv6 routing Wire-speed routing of IPv6 packets Layer 3 interface Configuration of a Layer 3 interface on a physical port, LAG, VLAN interface, or loopback interface Classless Interdomain Routing (CIDR) Support for CIDR Routing Information Protocol (RIP) v2 Support for RIP v2 for dynamic routing Policy-Based Routing (PBR) Flexible routing control to direct packets to a different next hop based on an IPv4 or IPv6 Access Control List (ACL) DHCP server Switch functions as an IPv4 DHCP server, serving IP addresses for multiple DHCP pools or scopes Support for DHCP options DHCP relay at Layer 3 Relay of DHCP traffic across IP domains User Datagram Protocol (UDP) relay Relay of broadcast information across Layer 3 domains for application discovery or relaying of Bootstrap Protocol (BOOTP)/DHCP packets Stacking Hardware stacking Up to 8 switches in a stack. Up to 200 ports managed as a single system with hardware failover Stacking is supported on the following models: Family 1: C1300-16P-4X, C1300-24T-4X, C1300-24P-4X, C1300-24FP-4X, C1300-48T-4X, C1300-48P-4X, C1300-48FP-4X, C1300-8MGP-2X, C1300-24MGP-4X, C1300-48MGP-4X Family 2: C1300-12XT-2X, C1300-12XS, C1300-16XTS, C1300-24XS, C1300-24XT, C1300-24XTS PIDs from the same Family can be stacked together. Cross-stacking between Families is not supported. High availability Fast stack failover delivers minimal traffic loss. Support for LAG across multiple units in a stack Plug-and-play stacking configuration/management Active/standby for resilient stack control Auto-numbering Hot swap of units in stack Ring and chain stacking options, auto stacking port speed, flexible stacking port options High-speed stack interconnects Cost-effective high-speed 10 Gigabit Ethernet fiber interfaces Security Secure Shell (SSH) Protocol SSH is a secure replacement for Telnet traffic. Secure Copy Protocol (SCP) also uses SSH. SSH v1 and v2 are supported Secure Sockets Layer (SSL) SSL support: Encrypts all HTTPS traffic, allowing highly secure access to the browser-based management GUI in the switch IEEE 802.1X (authenticator role) 802.1X: RADIUS authentication and accounting, MD5 hash, guest VLAN, unauthenticated VLAN, single/multiple host mode, and single/multiple sessions Supports time-based 802.1X, dynamic VLAN assignment, and MAC authentication IEEE 802.1X supplicant A switch can be configured to act as a supplicant to another switch. This enables extended secure access in areas outside the wiring closet (such as conference rooms) Web-based authentication Web-based authentication provides network admission control through a web browser to any host devices and operating systems STP Bridge Protocol Data Unit (BPDU) Guard A security mechanism to protect the network from invalid configurations. A port enabled for BPDU Guard is shut down if a BPDU message is received on that port. This avoids accidental topology loops STP Root Guard Prevents edge devices not in the network administrator’s control from becoming STP root nodes STP loopback guard Provides additional protection against Layer 2 forwarding loops (STP loops) D
Ano, centrál. sklad
ASUS RT-BE88U ASUS RT-BE88U Dvoupásmový WiFi 7 AiMesh Extendable Performance Router, 4K-QAM, MLO, Duální 10G porty, SFP+, Čtyři 2,5G porty, Čtyři 1G porty, 34G WAN/LAN kapacita, Zabezpečení sítě bez předplatného, ??VPN Bleskově rychlá technologie WiFi 7 zvyšuje propustnost až na 7200 Mb/s díky provozu Multi-Link a 4096-QAM. Zvyšte kapacitu své kabelové sítě až na 34G pomocí jednoho špičkového portu 10G SFP+ a jednoho standardního portu 10G WAN/LAN. Zajistěte si neustálý internet díky detekci AI WAN, všestranným možnostem konfigurace WAN a praktickému portu USB připravenému pro 4G LTE a 5G mobilní tethering. Uvolněte náročné síťové aplikace WiFi 7 a 10G s výkonným čtyřjádrovým 2,6 GHz 64bitovým CPU. Snadno vytvořte až pět SSID pomocí Guest Network Pro pro snadné nastavení a správu zařízení IoT, okamžitá připojení VPN a pohodlnou rodičovskou kontrolu. Zůstaňte v bezpečí s komerční AiProtection Pro poháněnou Trend Micro, bezpečnostním skenováním jedním klepnutím, komplexní podporou VPN a site-to-site VPN. Zajistěte bezproblémovou konektivitu pro všechna zařízení pomocí celodomácí sítě s bohatými funkcemi poháněné AiMesh. Specifikace Technické Specifikace Síťový standard IEEE 802.11a IEEE 802.11b IEEE 802.11g WiFi 4 (802.11n) WiFi 5 (802.11ac) WiFi 6 (802.11ax) WiFi 7 (802.11be) IPv4 IPv6 Přenos dat WiFi WiFi 7 (802.11be) (2.4GHz): up to 1376 Mbps WiFi 7 (802.11be) (5GHz): up to 5764 Mbps Anténa 4x Externí odpojitelná anténa Procesor 2.6GHz 4-jádrový procesor Paměť 256MB Flash 2GB RAM Operační frekvence 2.4 GHz 5 GHz Konektory 1x 10Gbps pro WAN/LAN, 1x 10Gbps SFP+ pro WAN, 1x 2.5Gbps pro WAN/LAN, 3x 2.5 Gbps pro LAN, 4x RJ45 10/100/1000Mbps pro WAN/LAN, 1x USB 3.2 Napájení AC vstup: 110V~240V (50~60Hz) DC výstup: 19 V s max. Proud 2,37 A ; 19,5 V s max. Proud 2,31A Rozměry a váha Rozměry 300 x 188 x 60.5 mm Váha 1060 g
Dodání 3-5 dní

PLANET IGS-6325-4UP2X; Průmyslový L3 PoE spravovatelný přepínač 4× RJ-45 2.5G Base-T, 2× SFP+ 10G Base-SR/LR (zpětně kompatibilní s 1000 Base-SX/LX/BX a 2500 Base-X SFP), podpora DDM diagnostiky. Porty 1-4 podporují PoE++ napájení (802.3af/802.3at/802...
Ano, centrál. sklad

Plně spravovaný přepínač M4350-24F4V (XSM4328FV) -24xSFP+ a 4xSFP28 25G řízený přepínač -24 portů 10GBASE-X SFP+ se 4 uplinky 25GBASE-X SFP28 -Vnitřní zdroj 240W -1 slot pro modulární napájecí zdroj (redundance 1+1) -Lze použít jakýkoli APS350Wv1, AP
Dodání 3-5 dní
TP-Link EAP653 UR Přístupový bod AX3000 WiFi 6 pro montáž na strop Velmi rychlé WiFi 6 rychlostí: - 2402 Mb/s na 5 GHz t+ 574 Mb/s na 2,4 GHz Bezdrátové pokrytí s mimořádným dosahem díky většímu počtu antén s vyšším vysílacím výkonem Podpora technologií WiFi 6, jako je HE160, 1024-QAM atd Pokročilé funkce: Omada Mesh, bezproblémový roaming atd Napájení PoE+: Podporuje standard 802.3at PoE+ i stejnosměrný proud (adaptér není součástí dodávky) Velmi tenký design: Elegantní design ?16cm × 3,3cm přináší větší agilitu. Integrace s platformou Omada SDN pro centralizovanou správu Stránky produktu: https://www.tp-link.com/cz/business-networking/omada-sdn-access-point/eap653-ur/ Technické specifikace HARDWARE FEATURES Interface 1× Gigabit PoE+ Port Button Reset Power Supply • 802.3at PoE • 12V DC / 1.5 A (Power Adapter IS NOT included) • 48V Passive PoE Power Consumption • EU: 14.2 W • US: 15.5 W Dimensions ( W x D x H ) 6.3 × 6.3 × 1.3 in (160 × 160 × 33.6 mm) Antenna Type Internal Omni • 2.4 GHz: 2× 5 dBi • 5 GHz: 3× 5 dBi Mounting • Ceiling /Wall Mounting (Kits included) • Junction Box Mounting WIRELESS FEATURES Coverage 140?(1500 ft2)*** Concurrent Clients 250+** Wireless Standards IEEE 802.11ax/ac/n/g/b/a Frequency 2.4 GHz and 5 GHz Signal Rate • 5 GHz: Up to 2402 Mbps† • 2.4 GHz: Up to 574 Mbps† Wireless Functions • 1024-QAM • 4× Longer OFDM Symbol • OFDMA • Multiple SSIDs (Up to 16 SSIDs, 8 for each band) • Enable/Disable Wireless Radio • Automatic Channel Assignment • Transmit Power Control (Adjust Transmit Power on dBm) • QoS(WMM) • MU-MIMO(2G: 2*2 MU-MIMO DL/UL; 5G:2*2 MU-MIMO DL/UL) • HE160 (160 MHz Bandwidth)‡ • Seamless Roaming(802.11k/v/r)§ • Omada Mesh§ • Band Steering • Load Balance • Airtime Fairness • Beamforming • Rate Limit • Reboot Schedule • Wireless Schedule • Wireless Statistics based on SSID/AP/Client Wireless Security • Captive Portal Authentication§ • Access Control • Wireless Mac Address Filtering • Wireless Isolation Between Clients • SSID to VLAN Mapping • Rogue AP Detection • 802.1X Support • WPA-Personal/Enterprise, WPA2-Personal/Enterprise, WPA3-Personal/Enterprise Transmission Power • CE: <20 dBm(2.4 GHz, EIRP) <23 dBm(5 GHz, Band1 & Band2, EIRP) • FCC: <26 dBm (2.4 GHz) MANAGEMENT Omada App Yes Centralized Management • Omada Hardware Controller (OC300) • Omada Hardware Controller (OC200) • Omada Software Controller • Omada Cloud-Based Controller Cloud Access Yes. Requiring the use of OC300, OC200, Omada Cloud-Based Controller, or Omada Software Controller. Email Alerts Yes LED ON/OFF Control Yes Management MAC Access Control Yes SNMP v1, v2c, v3 System Logging Local/Remote Syslog Local/Remote Syslog SSH Yes Web-based Management HTTP/HTTPS L3 Management Yes Multi-site Management Yes Management VLAN Yes Zero-Touch Provisioning Yes. Requiring the use of Omada Cloud-Based Controller. OTHERS Certification CE, FCC, RoHS Package Contents • EAP653 UR • Ceiling/Wall Mounting Kit • Installation Guide Note: DC adapter is not included in the package, and is sold separately. System Requirements Microsoft Windows XP, Vista, Windows 7, Windows 8, Windows10, Windows 11, Linux Environment • Operating Temperature: 0–40 ? (32–104 ?) • Storage Temperature: -40–70 ? (-40–158 ?) • Operating Humidity: 10–90% RH non-condensing • Storage Humidity: 5–90% RH non-condensing
Ano, centrál. sklad
Router Brovi 5G CPE 5 (H155-381) VPN Passthrough: Ano Typ rozhraní ethernetu LAN: Gigabit Ethernet Přiřazení sítě VLAN na základě SSID: Ano Přenosová rychlost sítě Ethernet: 1001000 Mbit/s10 Připojení
Dodání 3 dny

Síťový přepínač Ruijie Networks RG-NBS3200-24GT4XS-P Spravovaný L2 Gigabit Ethernet (10/100/1000) Napájení přes Ethernet (PoE) Šedá Omlouváme se, průběžně pracujeme na lepším popisu
Dodání 3-5 dní
GWN7710R je 6portový (5GE+1SFP) venkovní řízený PoE switch Lite, který je vybaven vodotěsným a prachotěsným krytem se stupněm krytí IP66, který chrání před nepříznivými povětrnostními podmínkami včetně deště, sněhu a vysokých teplot. Pro zajištění stabilního a výkonného síťového výkonu podporuje GWN7710R flexibilní a komplexní segmentaci provozu pomocí globálních VLAN nebo VLAN pro jednotlivé porty, poskytuje režimy správy priorit DSCP/802.1p QoS. Nabízí 4 gigabitové porty s pasivním výstupem PoE++, 1 gigabitový port se vstupem PoE++ a jeden port 2,5G SFP. Zařízení GWN7710R lze spravovat různými způsoby, včetně lokální správy prostřednictvím webového uživatelského rozhraní, prostřednictvím cloudu s GDMS a lokální správy pomocí nástroje GWN Manager. Tento venkovní Lite managed switch podporuje instalaci na sloupek, lištu DIN a na stěnu pro různé venkovní i vnitřní aplikace. S modelem GWN7710R mohou uživatelé vytvářet škálovatelné, bezpečné, vysoce výkonné a snadno spravovatelné podnikové sítě pro venkovní prostory, hotely, restaurace, parky, kampusy, veřejné prostory a další místa. Klíčové vlastnosti: - 5 gigabitových portů RJ45 (4 výstupní porty PoE, 1 vstupní port PoE) - IEEE 802.3 at/af nebo 24V/48V DC pasivní PoE výstup,až 60W na portu 1 a až 30W na portu 2-4; Podporuje funkci PoE Watchdog - SFP Fiber Port pro přenos na dlouhé vzdálenosti - DHCP Snooping – Povolte pouze pakety DHCP z důvěryhodných portů, aby bylo podnikové prostředí DHCP bezpečné - Třída odolnosti proti prachu a vodě IP66; Široký rozsah provozních teplot: -40°C a 60°C - Podporuje pohodlnou a inteligentní místní webovou konfiguraci, GWN Manager a GDMS Network Management - STP/RSTP zaručují rychlou konvergenci, zajišťují stabilitu sítě a poskytují vyvážení zatížení a redundanci spojů - Vestavěná QoS umožňuje prioritizaci síťového provozu Ethernetové porty 5 × RJ45 1Gbps Funkce L2 Management Ano Počet VLAN 32 PoE napájení Ano POE-in Ano POE-out Ano SFP 1, Ano Stupeň krytí IP66
Ano, centrál. sklad
Typ: Switch Barva: bílá Šířka (mm): 92 Výška (mm): 51 Hloubka (mm): 21,5
Ano, centrál. sklad
48portový gigabitový switch TL-SG1048 48 portů 10/100/1 000 Mbit/s RJ45 Podporuje automatické učení adres MAC a Auto MDI/MDIX Ocelové pouzdro pro montáž do standardních racků 19 K čemu slouží tento produkt 48portový gigabitový přepínač TL-SG
Ano, centrál. sklad
Popis produktu Robustní rackový POE switch, který je ideální pro nasazení v kritických místech infrastruktury, to je USW Mission Critical. Díky trojí možnosti vstupního napájení nepřetržitě napájí připojená zařízení i během výpadku elektřiny. Kromě běžného napájení 230V AC switch disponuje integrovanou baterií, která dokáže dodat energii až 368Wh. Externě lze také připojit baterii s napětím 48V. Switch disponuje celkem 9 ethernetovými porty 10/100/1000Mbps, z nichž 4 porty podporují standard 802.3at (PoE+), další 4 porty popdorují standard 802.3bt (PoE++) a poslední port je bez možnosti PoE. Celkový PoE budget činní 120W. Dalších 80W pak poskytne dvojice standardních elektrických zásuvek na zadní straně switche. Správa switche probíhá ve známém rozhraní aplikace UniFi Network Application, kterou lze nainstalovat na zařízení s operačními systémy Windows, macOS nebo Linux. Stejně tak lze využít hotových řešení. Obsah balení • Zařízení • (2) rackový úchyt • (16) Šroub M4 • (6) Šroub 10#-32 • (2) Výsuvné kolejnice do racku • Napájecí kabel 230V • Kabel pro připojení baterie • Jehla na SIM • (4) Gumová podložka Technické parametry Konektory a rozhraní Rychlost LAN:(10) 10/100/1000Mbps Ostatní:Dotykový displej Napájení Typ napájení:Ze sítě (230V), Baterie Typy PoE:PoE-Out (pouze) Podporované PoE-Out standardy:802.3af, 802.3at, 802.3bt Redundantní napájení:Ano Počet PoE Out portů:8 PoE budget [W]:120 Max. spotřeba energie [W]:240 Napájení přes konektor/svorkovnici:48V DC, 230V AC Fyzické charakteristiky Provedení:Rackmount Šasi:Kovové Tlačítka:Reset Provozní teplota [°C]:-5 až 40 Šířka [mm]:442 Výška [mm]:44 Hloubka [mm]:480 Obecné Rychlost přepínání [Gbps]:18 Rychlost předávání paketů [Mpps]:26,78 Software Management:UniFi controller Funkce:VLAN, DHCP snooping Výchozí IP adresa:Dynamická z DHCP Výchozí jméno a heslo:Nastavuje se při prvním spuštění
Skladem v eshopu
Omada SG6428X je L3 managovatelný switch, který nabízí L3 routing, bleskurychlé optické připojení 10 Gb/s, stohování a redundantní napájecí zdroje. Switch přichází s 24 gigabitovými RJ45 porty, 4× 10 Gbps SFP+ sloty a má možnost fyzického stohování. V kom
Ano, centrál. sklad

Ubiquiti U7-Outdoor je celopovětrnostní přístupový bod WiFi 7 se 4 prostorovými streamy, integrovanou směrovou superanténou a všestrannými možnostmi montáže. Číslo položky: 100066716
Skladem v eshopu
Zyxel USG FLEX 50 H, 5 Gigabit user-definable ports, 1*USB with 1 YR Entry Defense Pack
Ano, centrál. sklad

STRONG SW5000M; Kompaktní gigabitový 5portový switch, který plně vyhoví všem požadavkům domácnosti či malé kanceláře. Nabízí kapacitu 10 Gbps , snadnou instalaci a odolné kovové tělo....
Ano, centrál. sklad
WAN-Port: 1x 2,5 Gbit/s Počet 10/100 Mbit/s Portů: 2 Počet Gigabit-Portů: 3 USB: 1x USB-A 2.0 Frekvence: 2,4 / 5 GHz Kódování: WPS WiFi-Standard: Wi-Fi 7 (IEEE 802.11be) Modem: ano Hmotnost (g): 800 Barva: bílá Rozměry: 254 x 191 x 63 Typ: WiFi-Router zásobování energií: Síť Provoz na baterie: ne Max. přenosová rychlost WiFi (Mbit/s): 5760 / 1376
3-5 dní dostupné

Netgear 350W 100-240VAC MODULAR PSU
Ano, centrál. sklad

PLANET GS-6311-24HP4X; Spravovatelný multigigabitový L3 přepínač s PoE++ napájením (802.3bt) , 16× 10/100/1000 Base-T RJ-45 PoE+, 8× 10/100/1000 Base-T RJ-45 PoE++, PoE napájení až 480 W , 4× 10G Base-X SFP+. Konzole/Telnet/Web/SNMP v1/v2c/v3 manageme...
Ano, centrál. sklad

UFiber GPON SFP modul s označením UF-GP-B+ je určen do GPON slotů v OLT jednotce od Ubiquiti Networks. Jedná se o speciální SFP modul s asymetrickou rychlostí 2,5 Gbps upload, 1,25 Gbps download ve směru ke klientům.
Skladem v eshopu